


Interact with Live PingOne Data in Warp via CData Connect AI
Warp is an agentic development environment that combines a modern terminal with an AI agent. It supports large language model (LLM) interactions and Model Context Protocol (MCP) server integrations, so the agent can reach live external data sources without leaving the terminal.
By integrating Warp with CData Connect AI through its built-in MCP Server, the Warp Agent gets governed, real-time access to live PingOne data. You can explore PingOne data, ask questions in plain language, and work with your records without writing custom integration code.
This article walks through configuring PingOne connectivity in Connect AI, configuring the CData MCP Server in Warp, and interacting with live PingOne data from the Warp Agent.
Step 1: Configure PingOne connectivity for Warp
Connectivity to PingOne from Warp is made possible through Connect AI's Remote MCP Server. To interact with PingOne data from Warp, start by creating and configuring a PingOne connection in Connect AI.
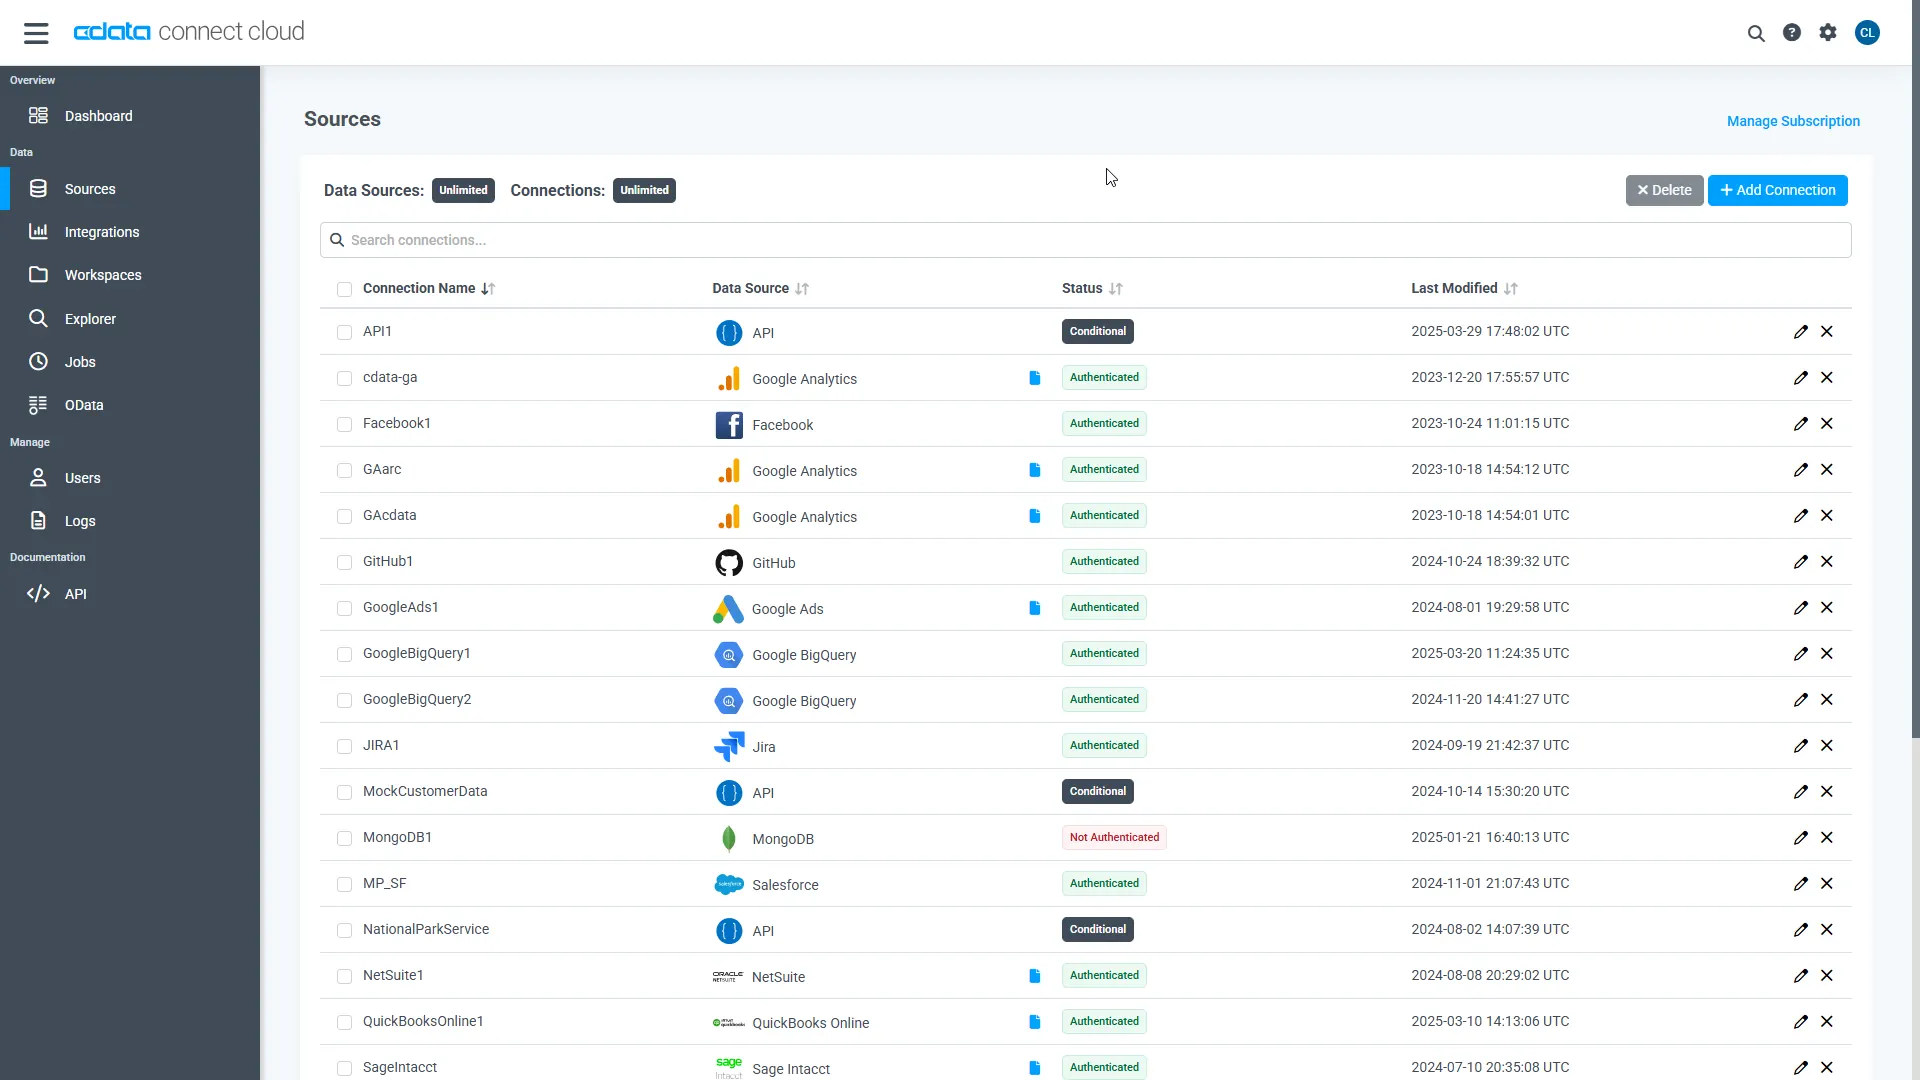
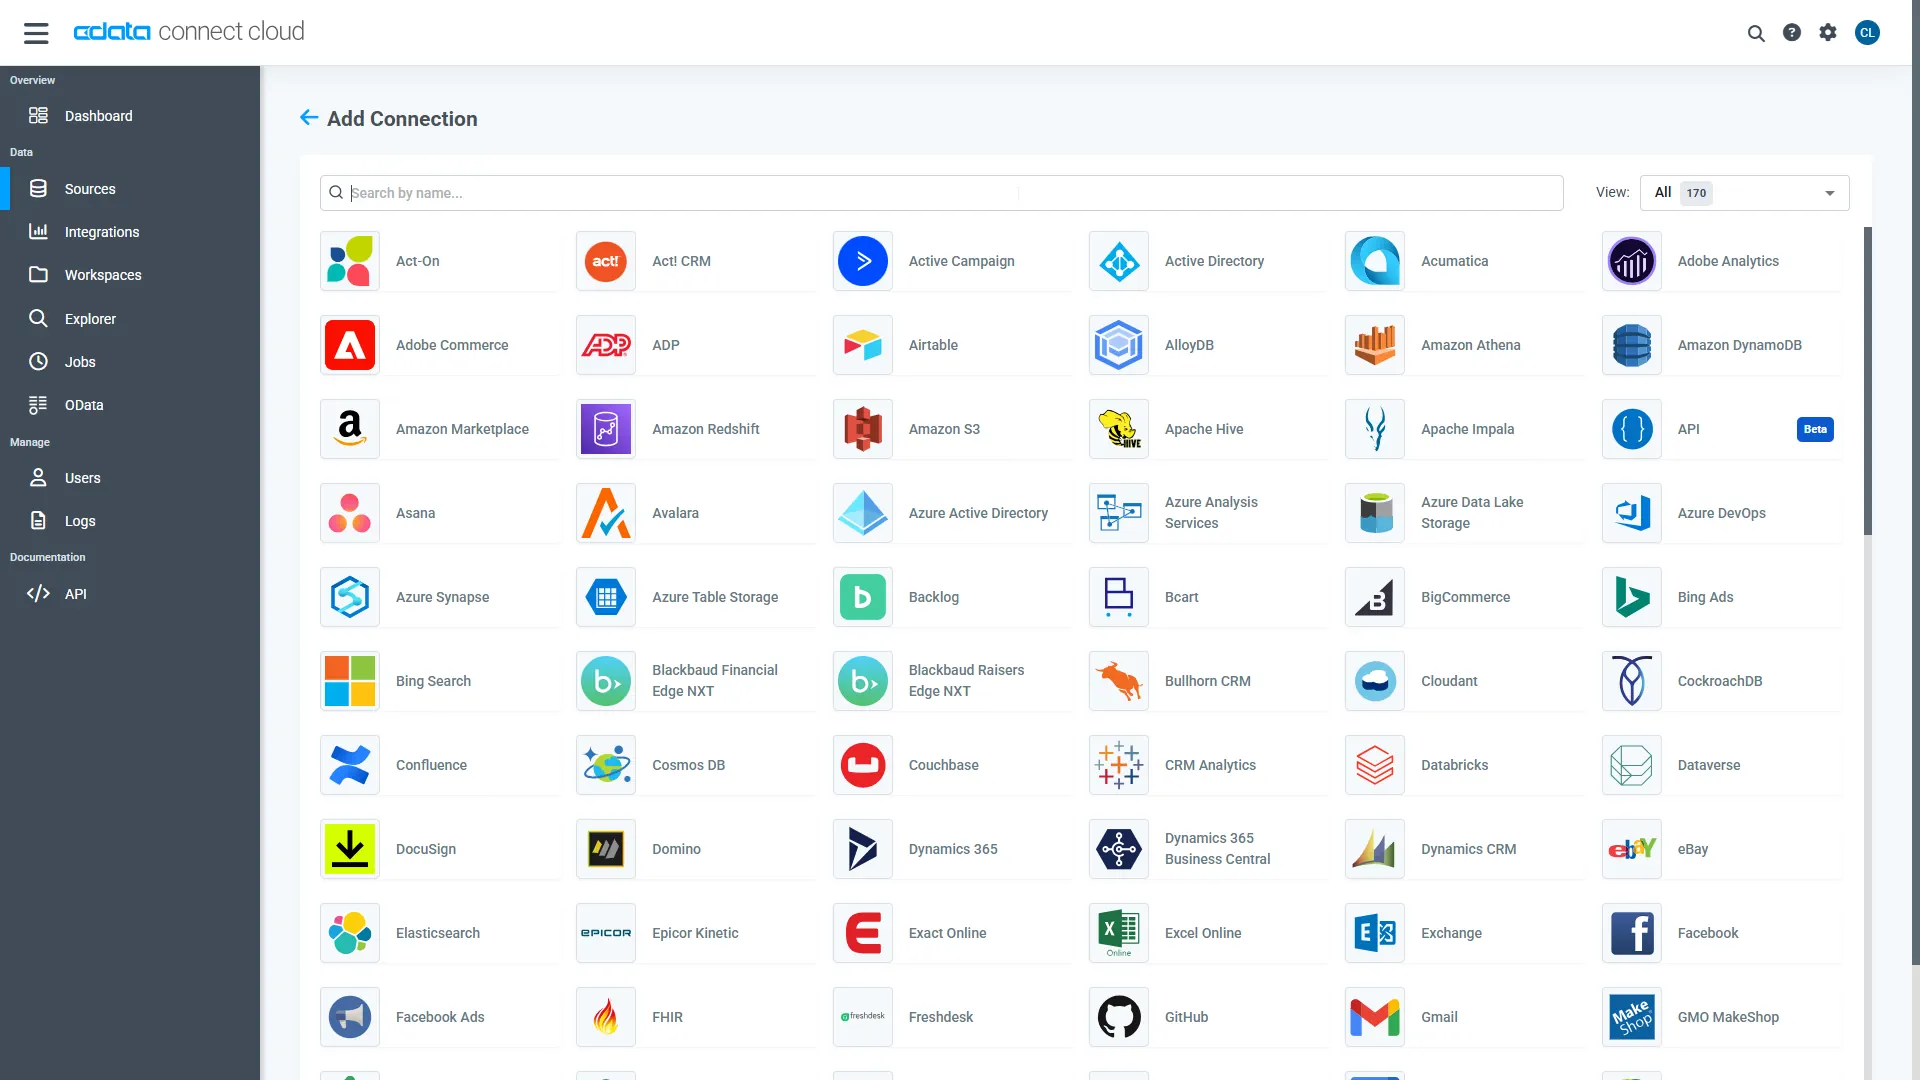
- Log into Connect AI, click Sources, and then click Add Connection
- Select PingOne from the Add Connection panel
-
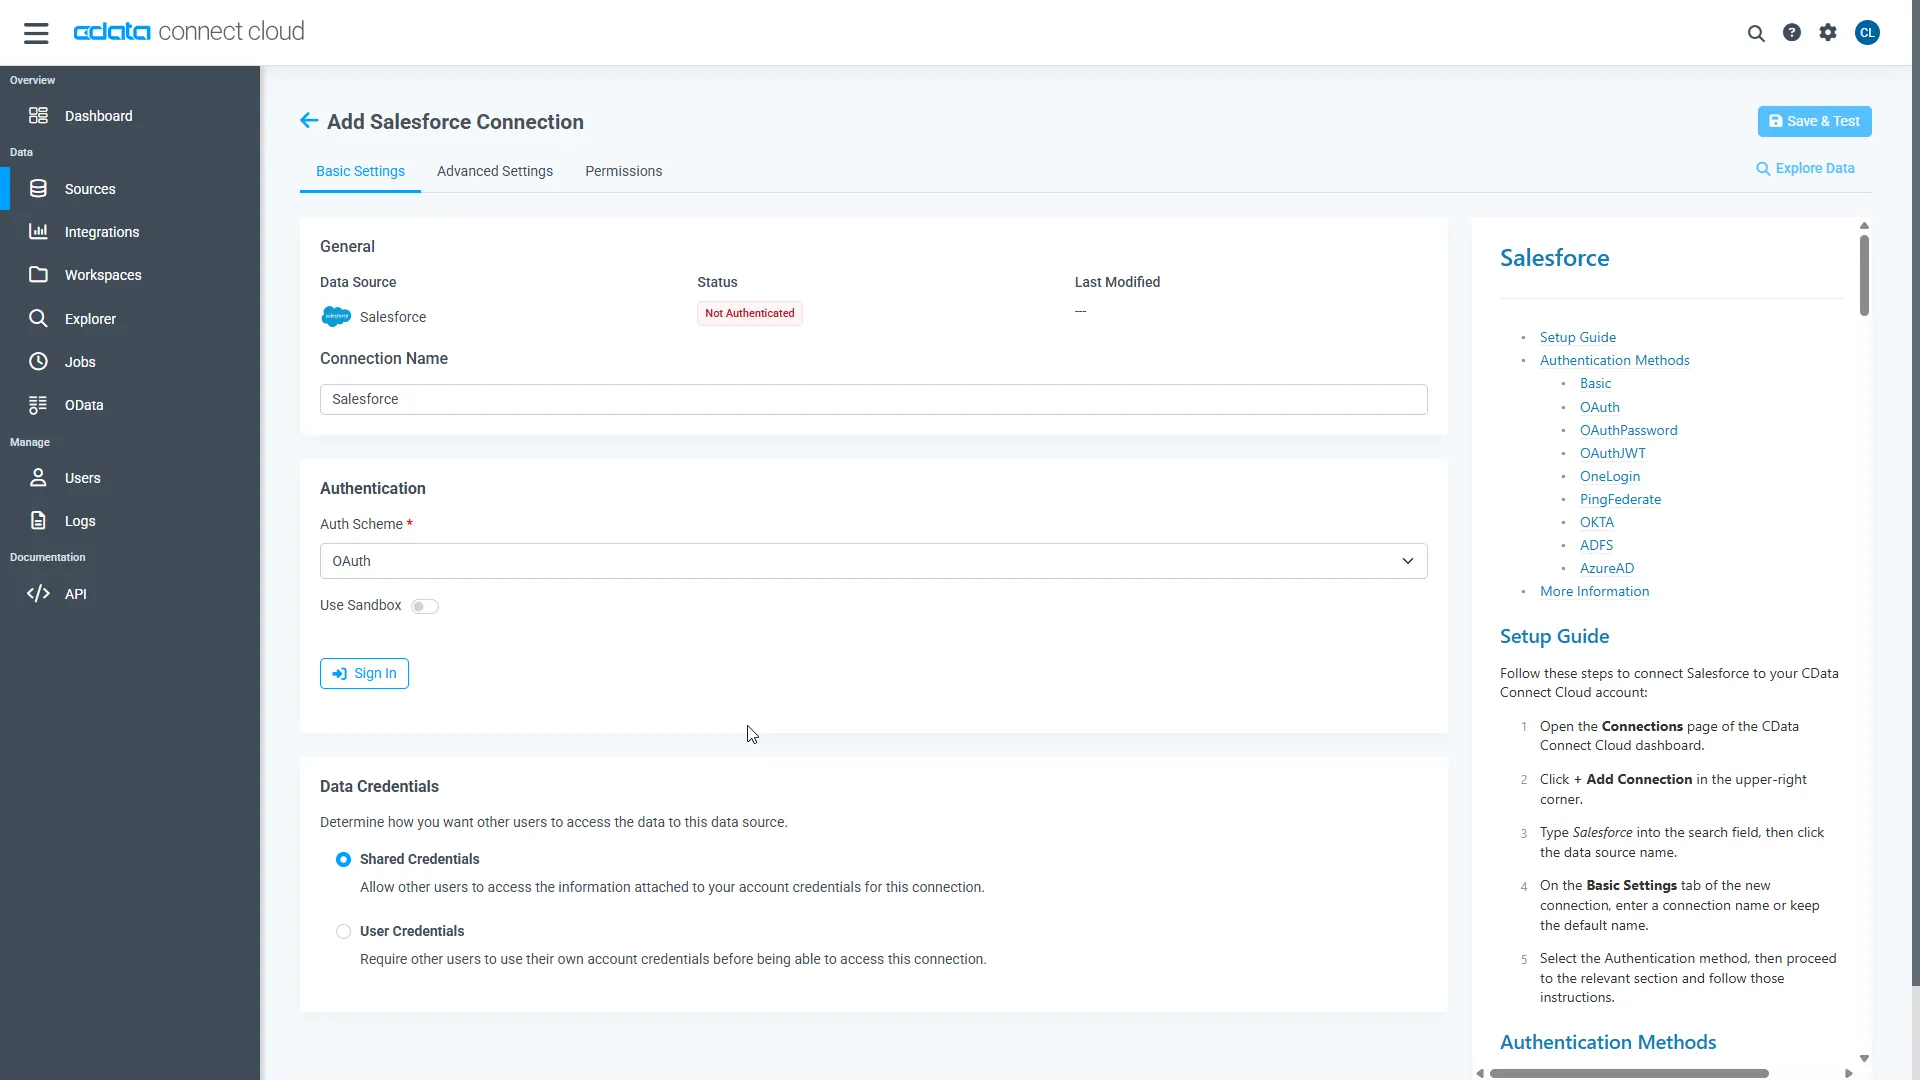
Enter the necessary authentication properties to connect to PingOne.
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
- Click Save & Test
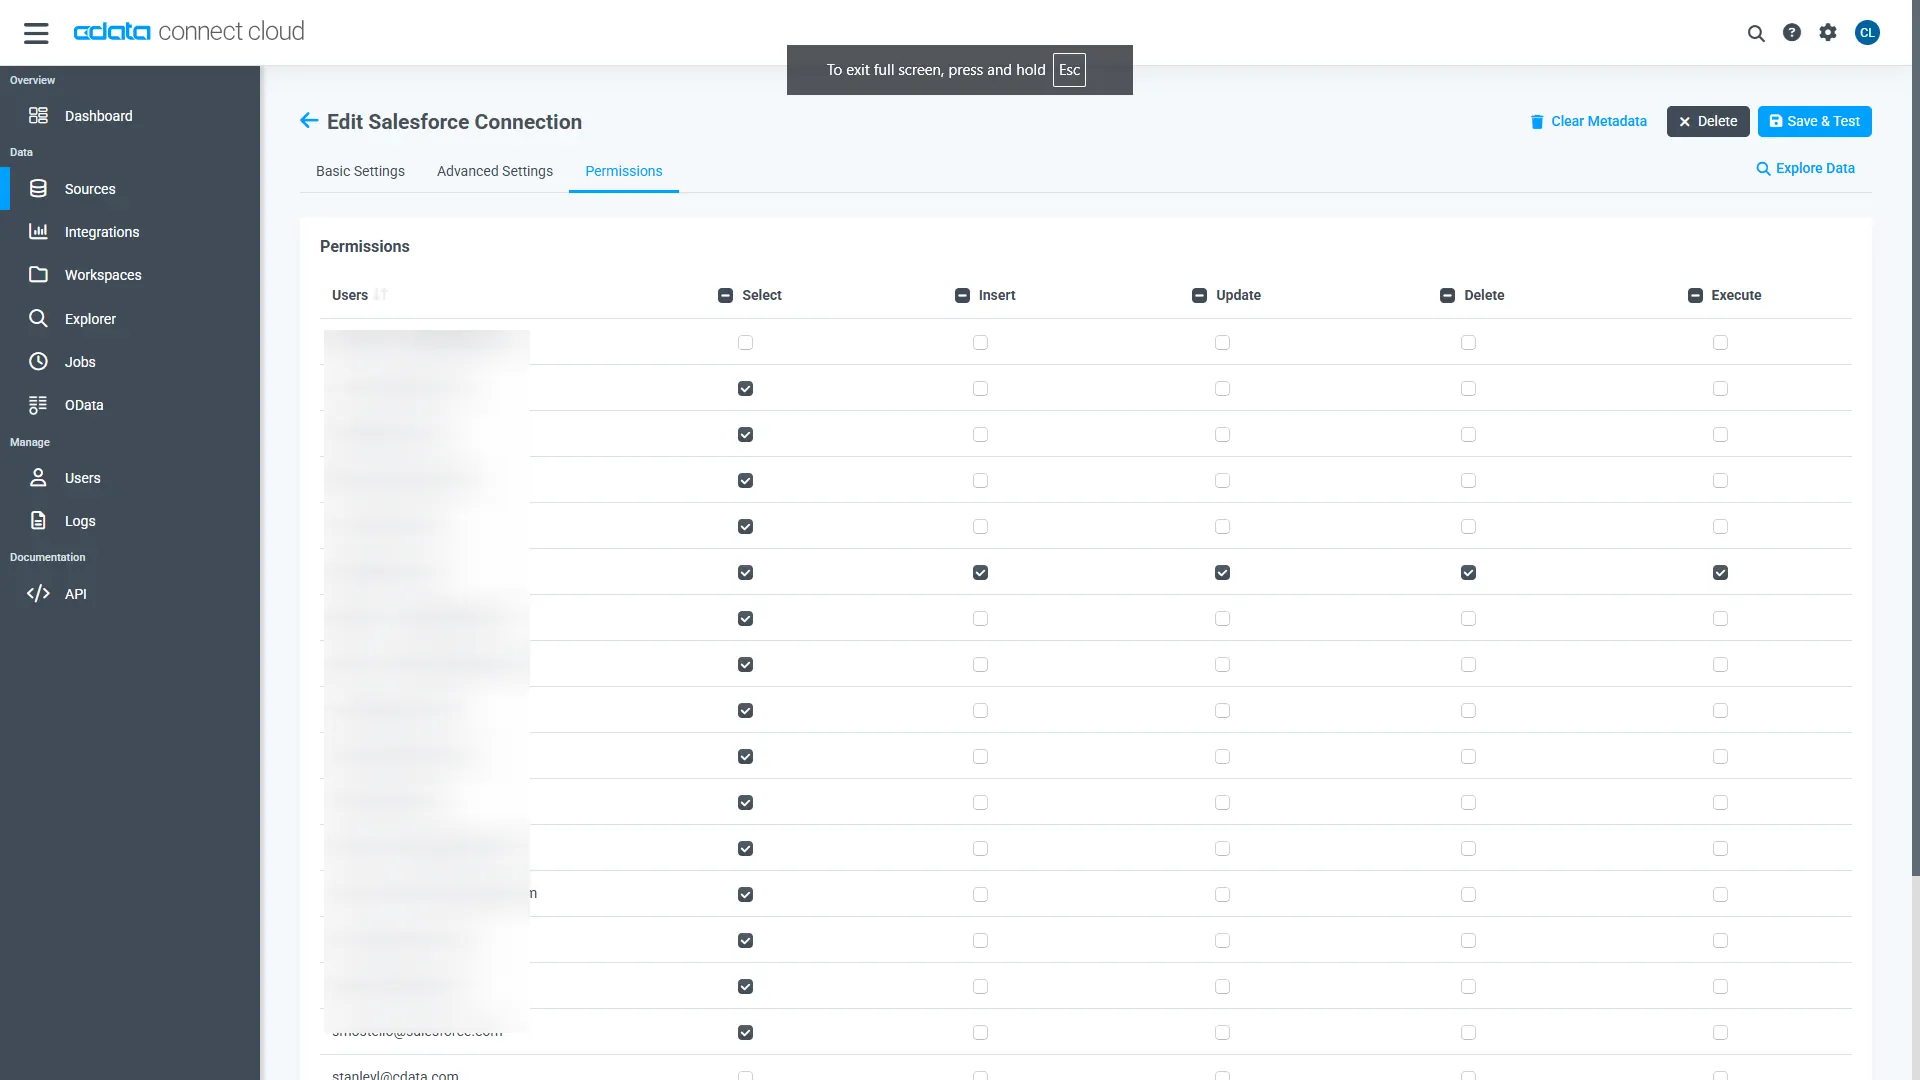
- Navigate to the Permissions tab and update user-based permissions
Add a Personal Access Token
A Personal Access Token (PAT) is used to authenticate the connection to Connect AI from Warp. It is best practice to create a separate PAT for each integration to maintain granular access control.
- Click the gear icon () at the top right of the Connect AI app to open Settings
- On the Settings page, go to the Access Tokens section and click Create PAT
- Give the PAT a descriptive name and click Create
- Copy the token when displayed and store it securely. It will not be shown again
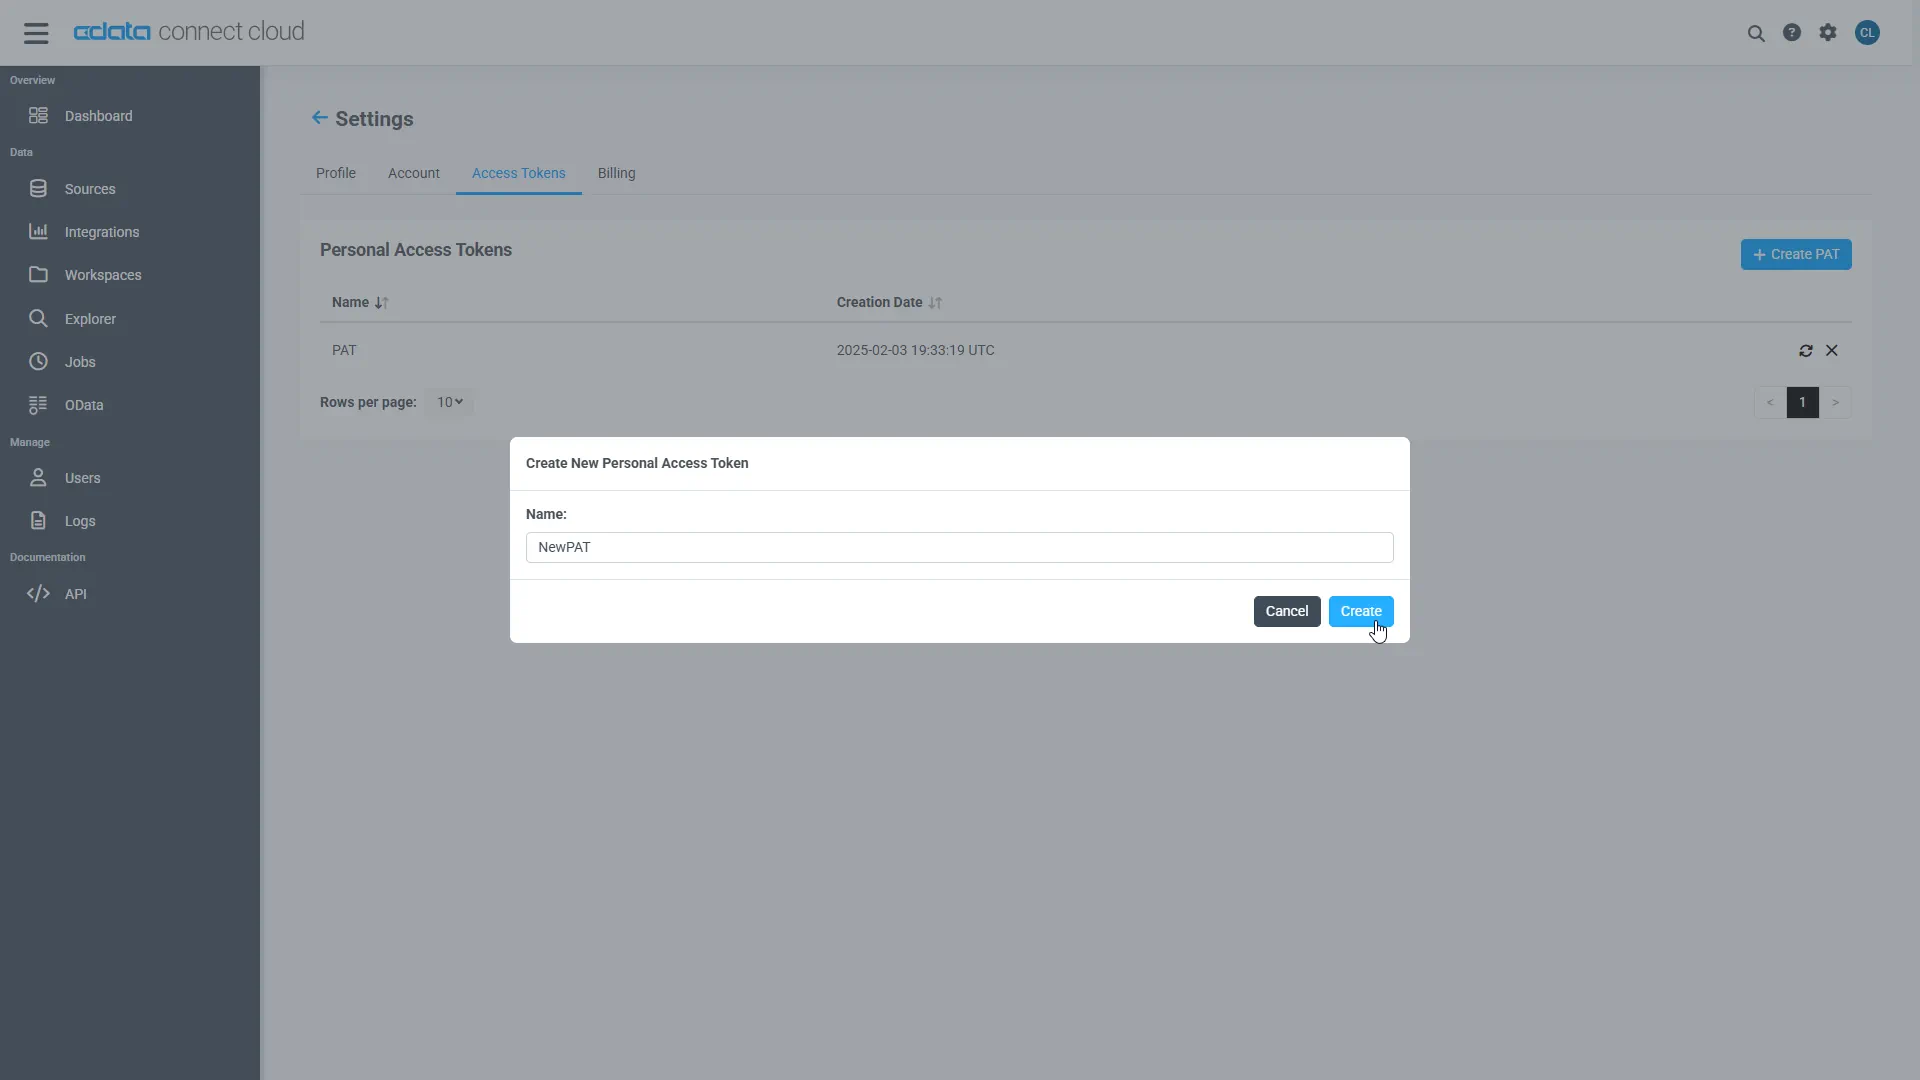
With the PingOne connection configured and a PAT generated, Warp can now connect to PingOne data through Connect AI.
Step 2: Configure Connect AI in Warp
Enable the Warp Agent, configure an LLM provider, and the Connect AI MCP endpoint in Warp so the agent can discover and call live data tools.
- Download and install Warp, and then sign up or log in to your Warp account
-
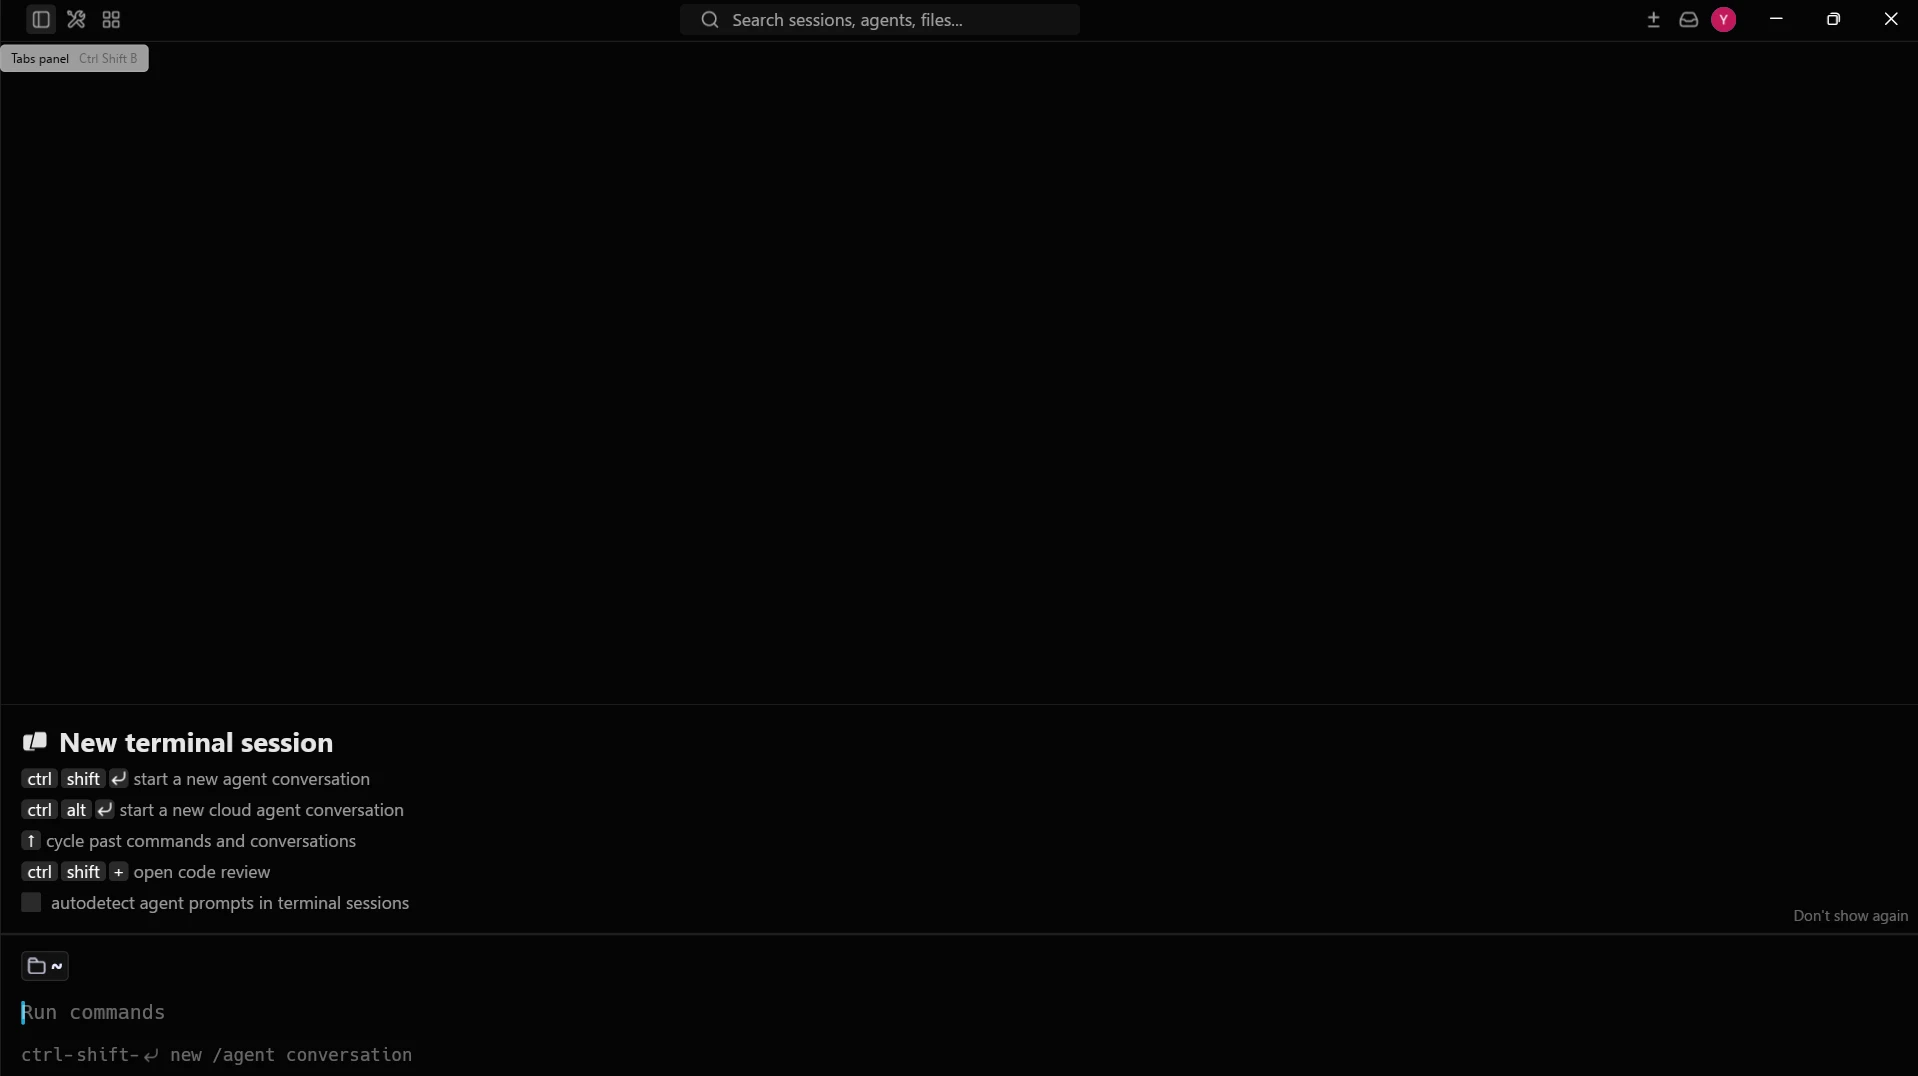
Click the Tabs panel icon at the top left of the window, or press Ctrl + Shift + B
-
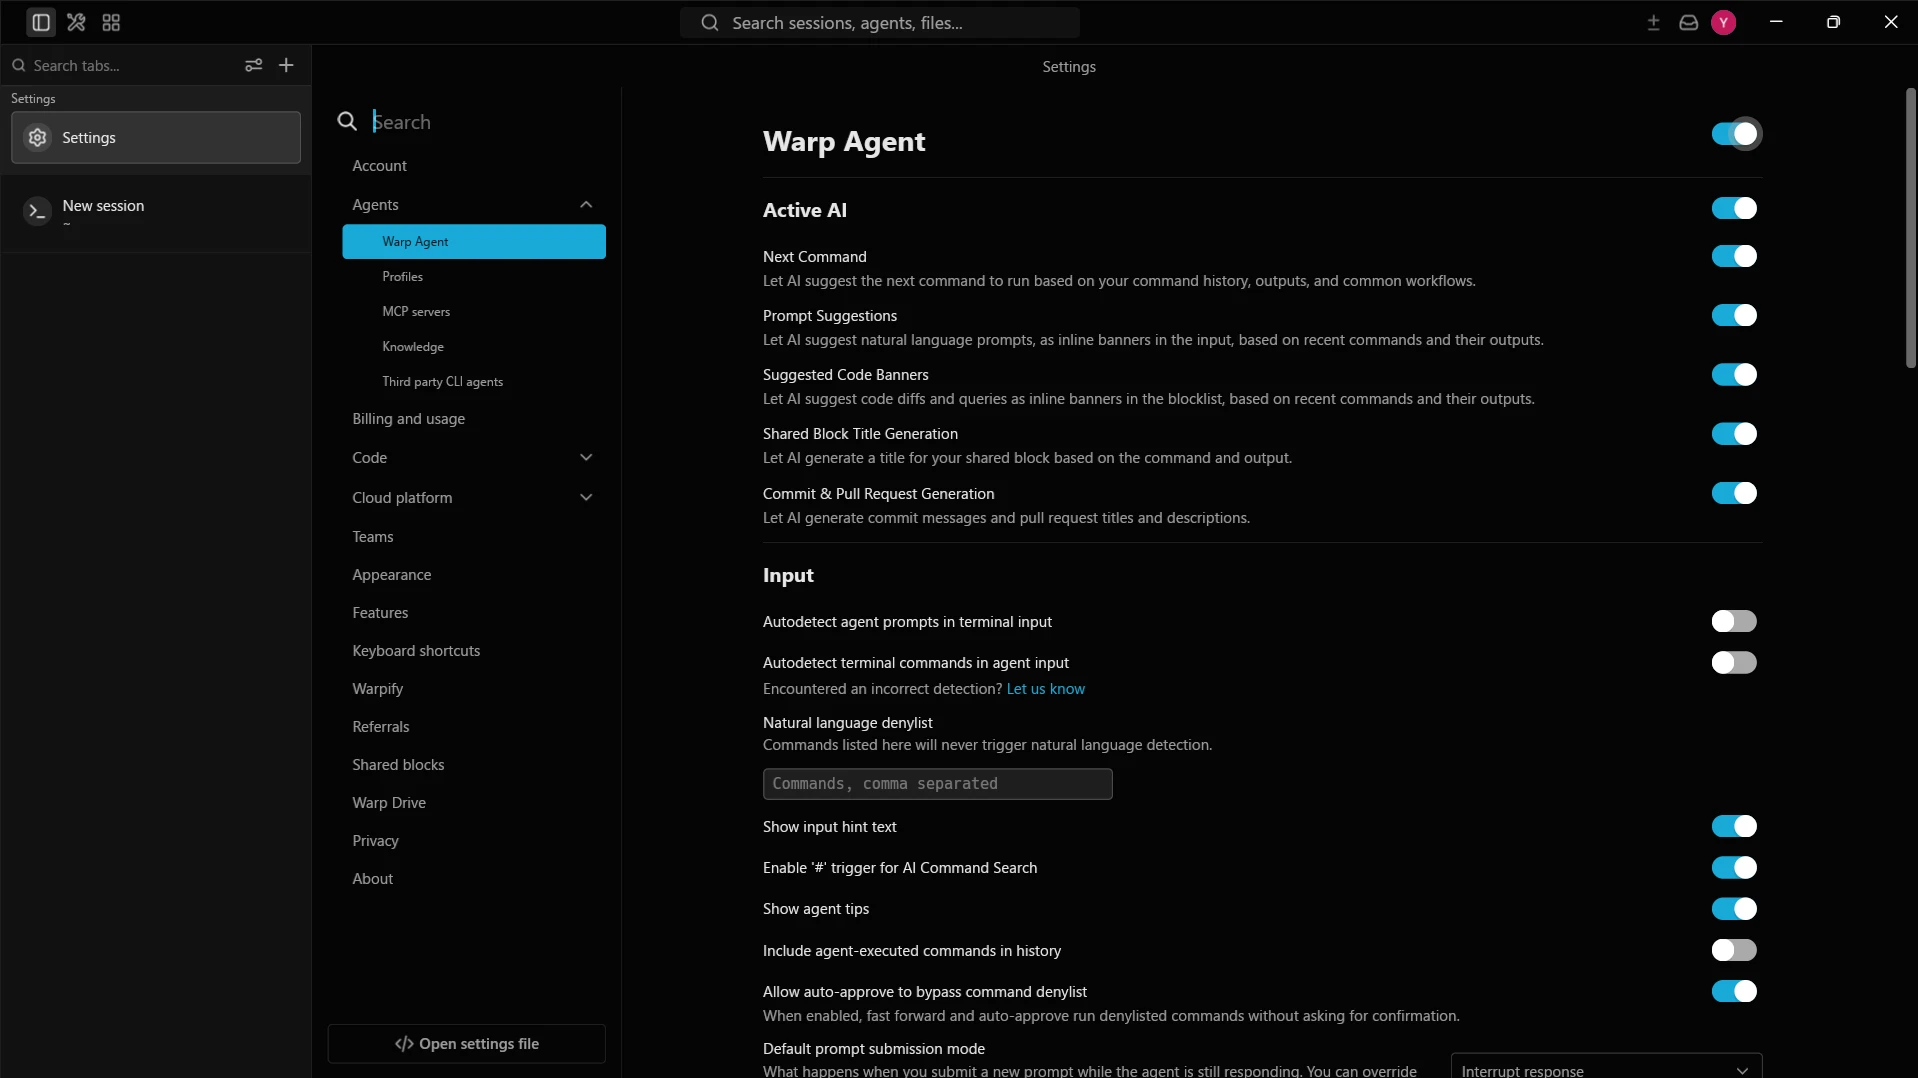
Click Settings, expand Agents, select Warp Agent, and toggle Warp Agent on
Configure an LLM provider
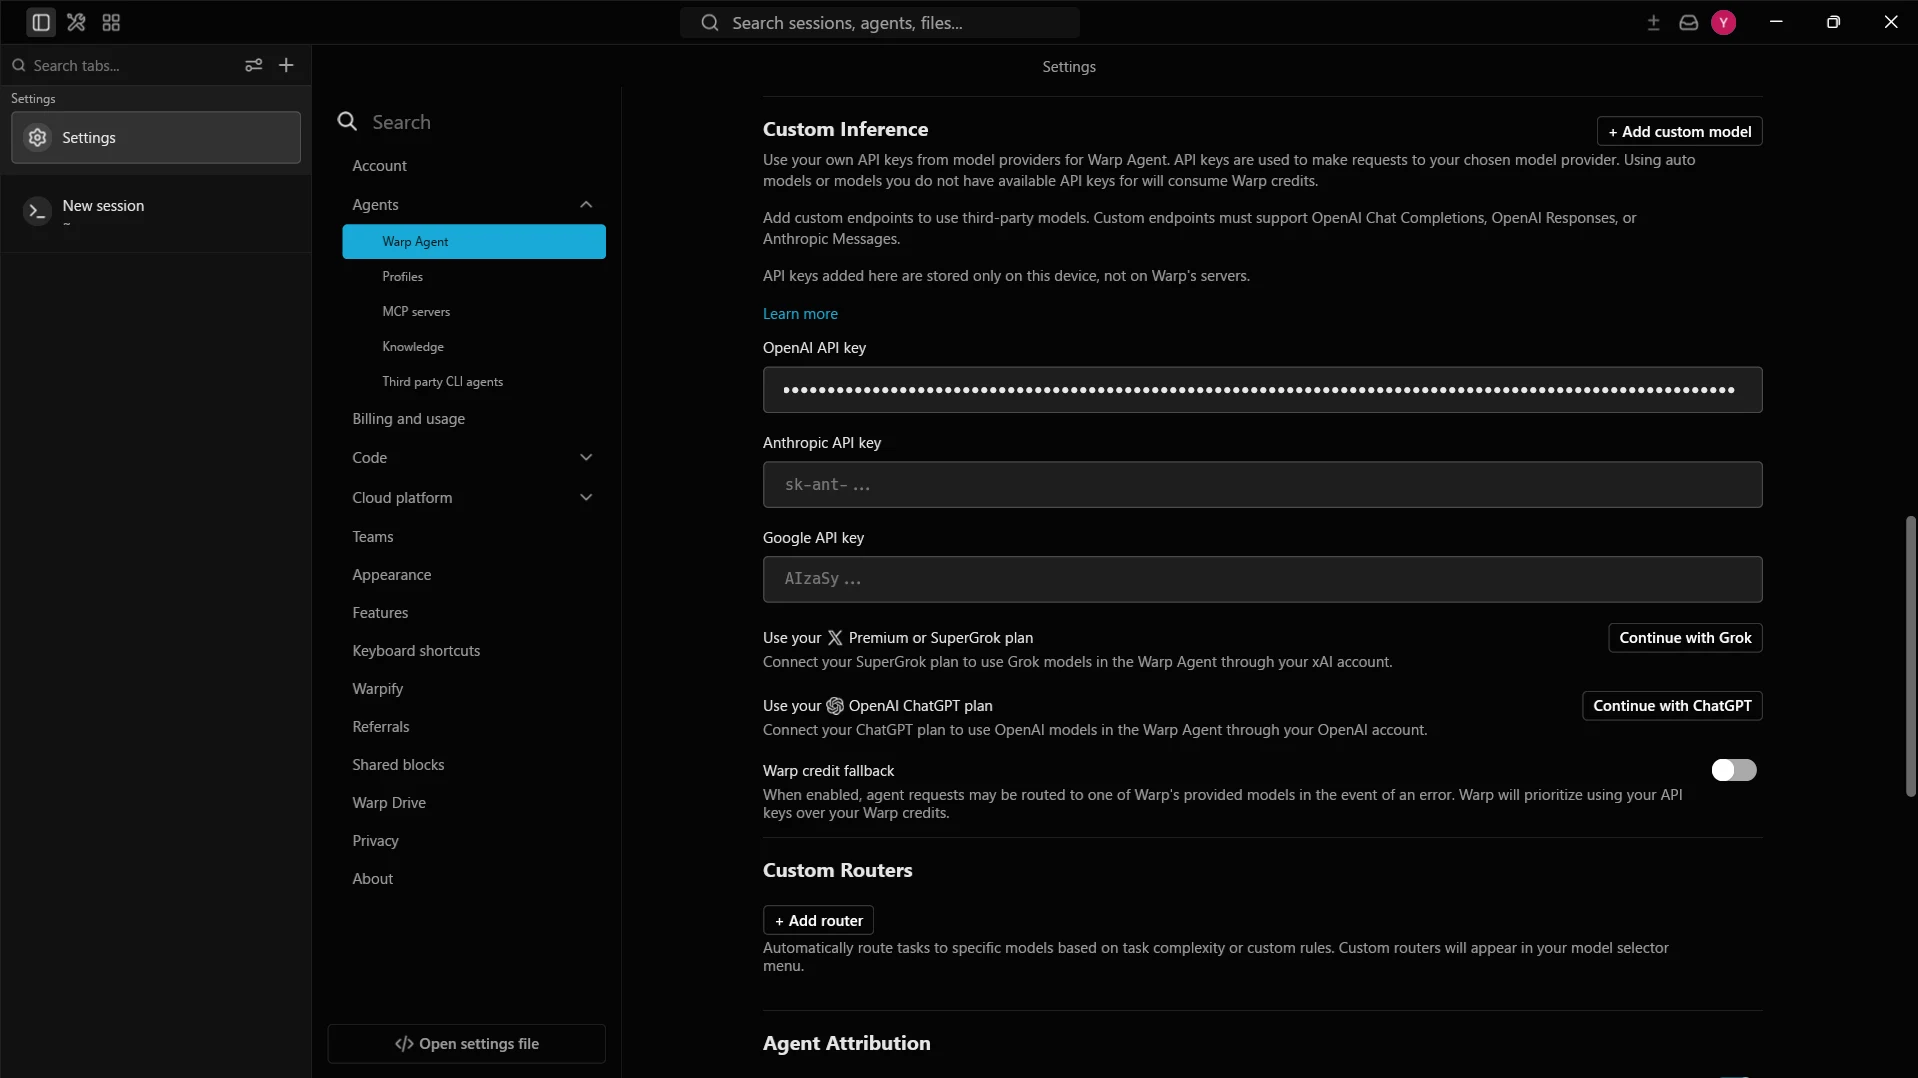
The Warp Agent needs an LLM provider to interpret your prompts and decide which MCP tools to call. Add an API key for your preferred provider.
- On the same Warp Agent page, scroll down to the Custom Inference section
-
Enter the API key for the LLM provider of your choice (e.g., OpenAI, Anthropic, or Google)
Add the Connect AI MCP Server
-
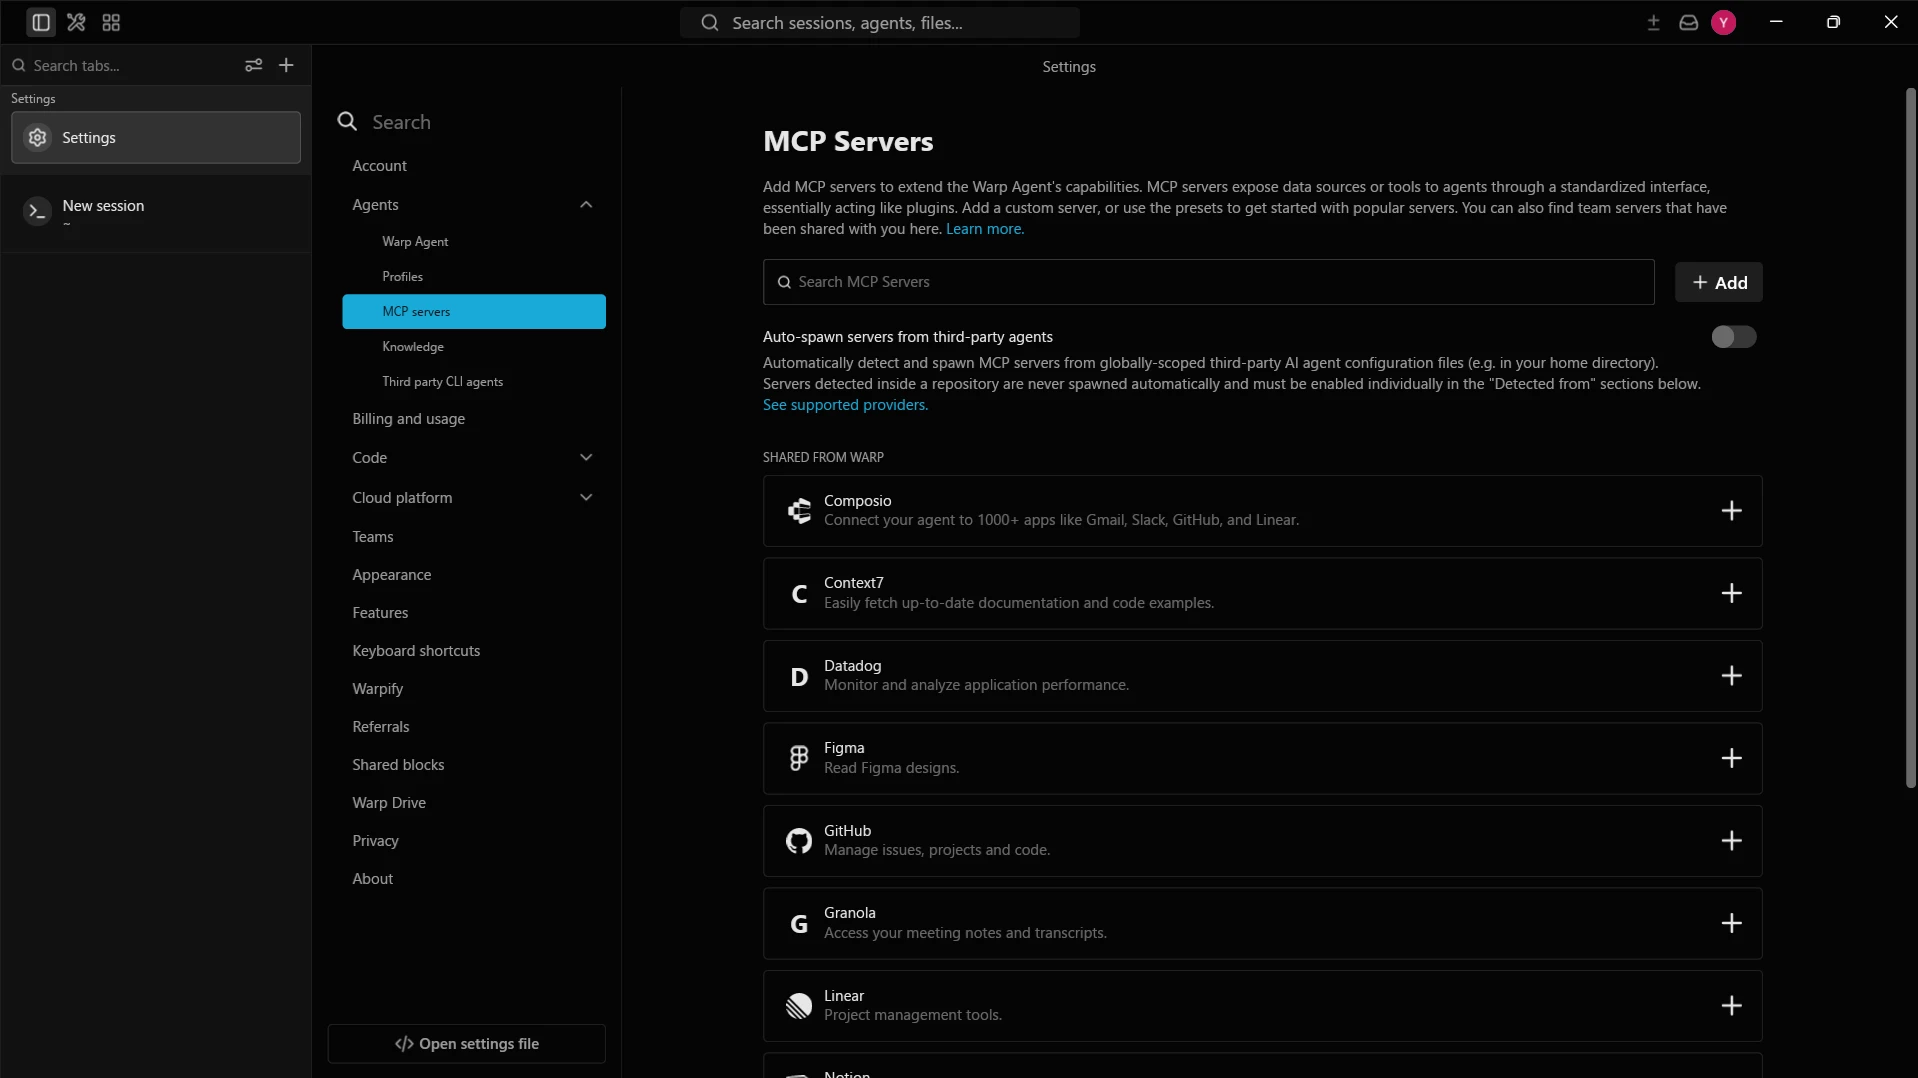
Under Agents, click MCP servers, and then click Add
-
In the Add New MCP Server editor, paste the following JSON configuration:
{
  "mcpServers": {
    "CData_Connect_AI": {
      "url": "https://mcp.cloud.cdata.com/mcp",
      "headers": {
        "Authorization": "Basic your_base64_encoded_email_PAT"
      }
    }
  }
}
Note: Combine your Connect AI email and PAT in the format email:PAT, Base64 encode the combined string, and prefix it with Basic. For example, given [email protected]:ABC123...XYZ, the header value becomes something like: Basic dXNlckBteWRvbWFpbjphSzkvbVB4Mi9Rcjd2TjQ...
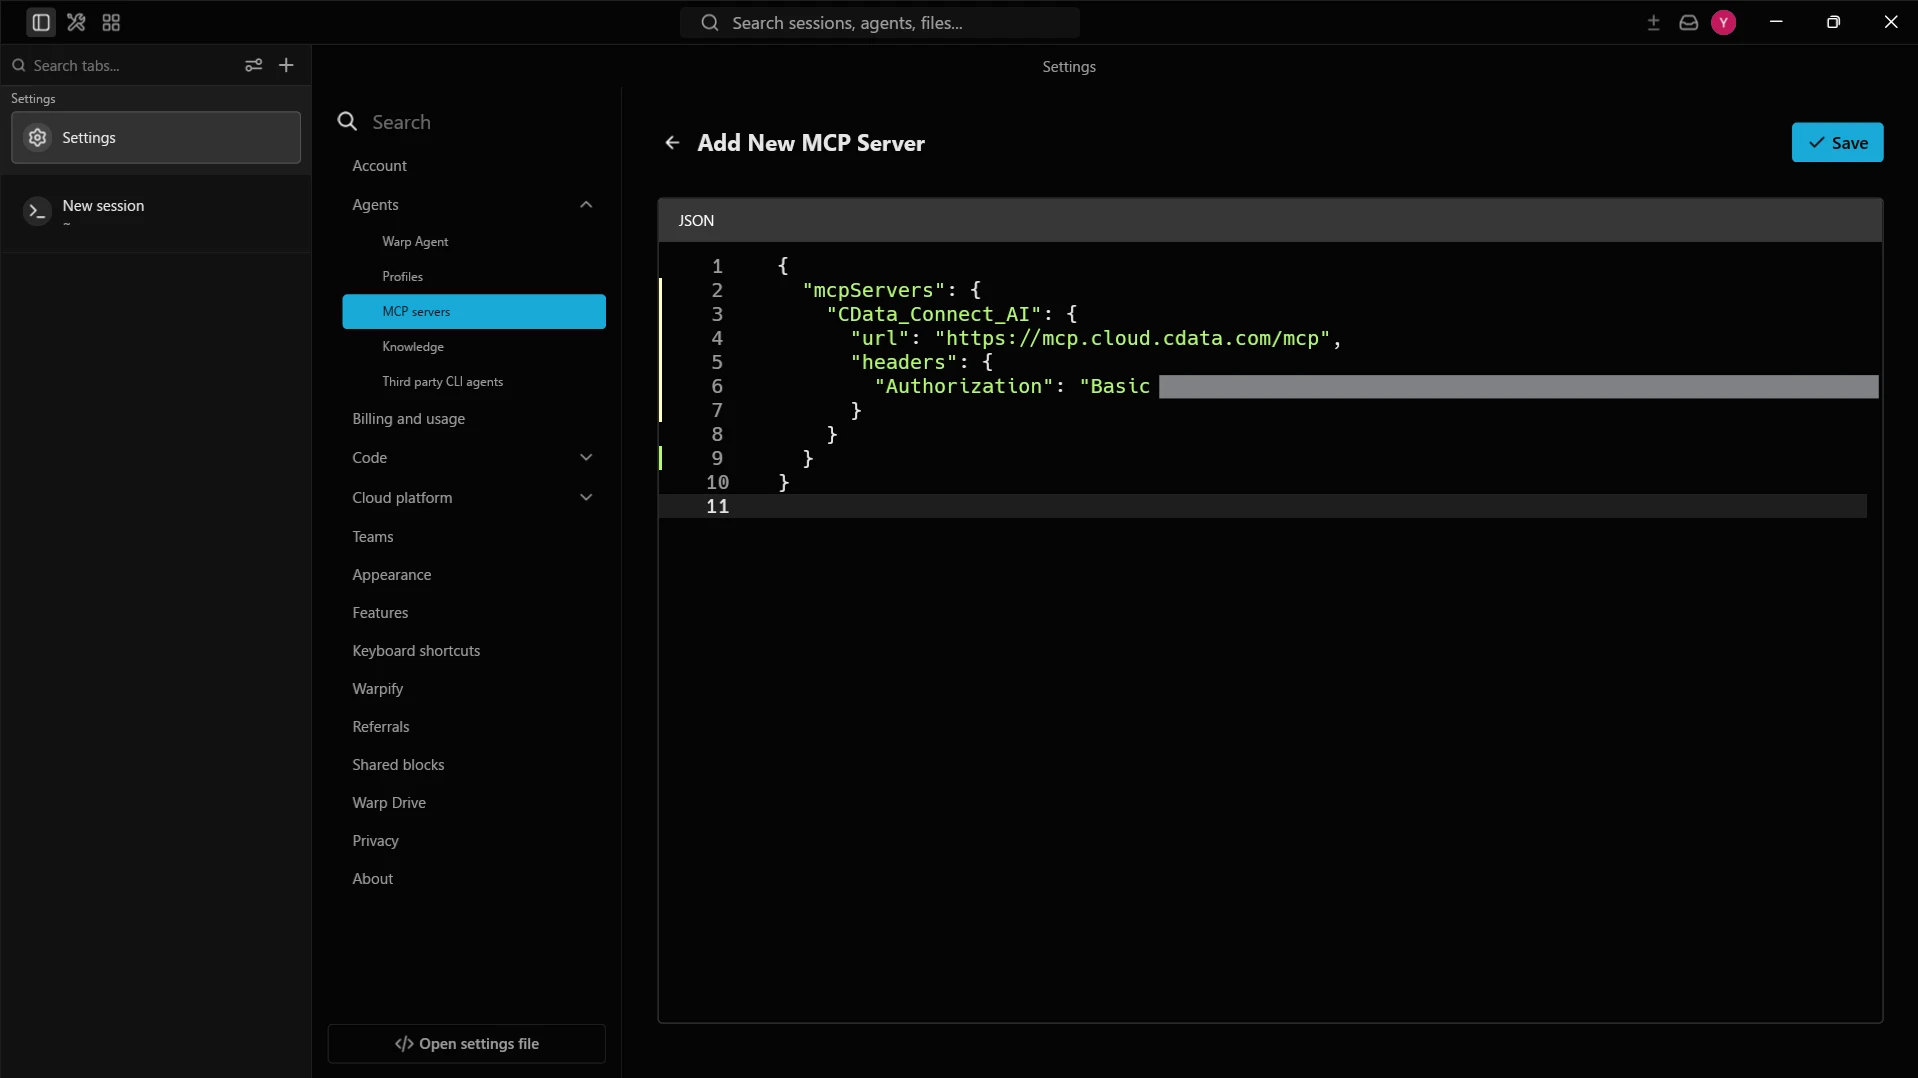
- Click Save to add the MCP server
-
Under My MCPs, confirm that CData_Connect_AI appears with the toggle enabled and the tools available
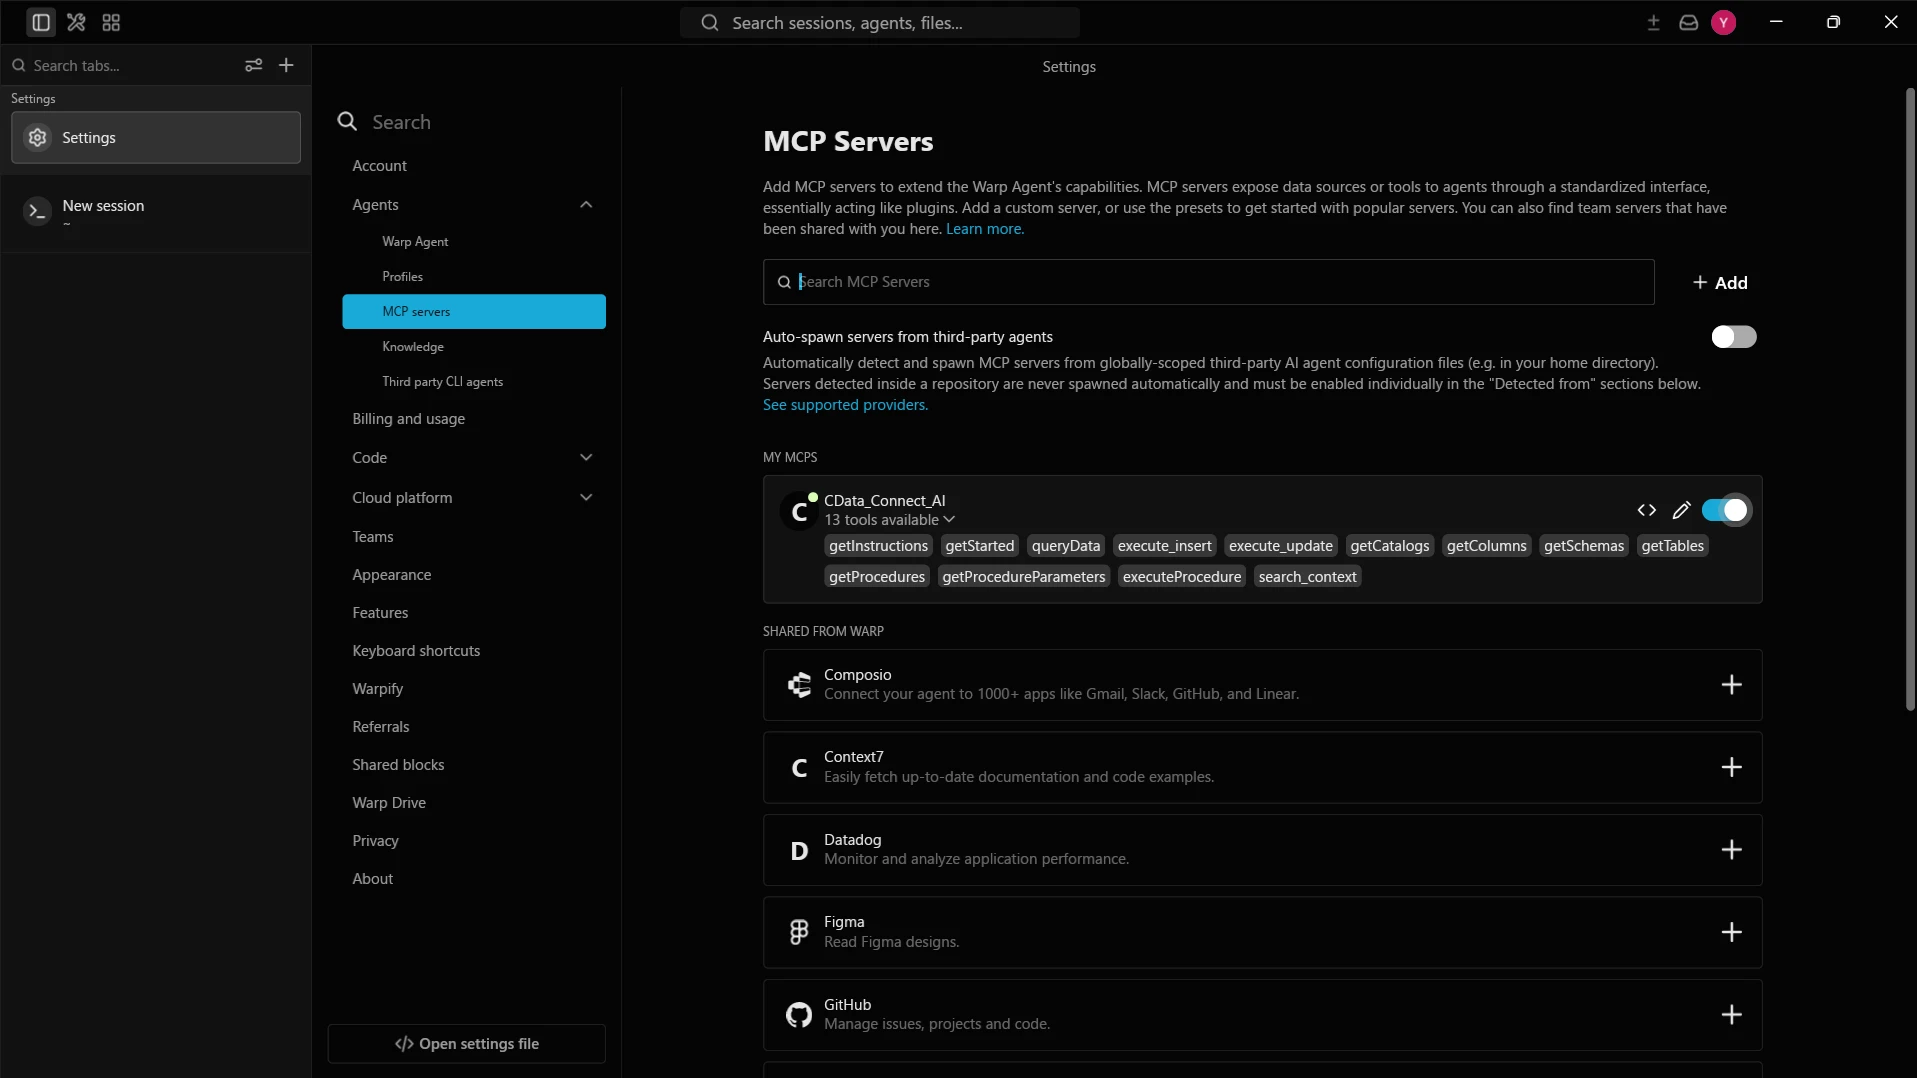
With the MCP server and an LLM provider configured, the Warp Agent is ready to interact with live PingOne data through Connect AI.
Step 3: Interact with live PingOne data from the Warp Agent
Use natural language prompts in the Warp Agent to explore live PingOne data.
-
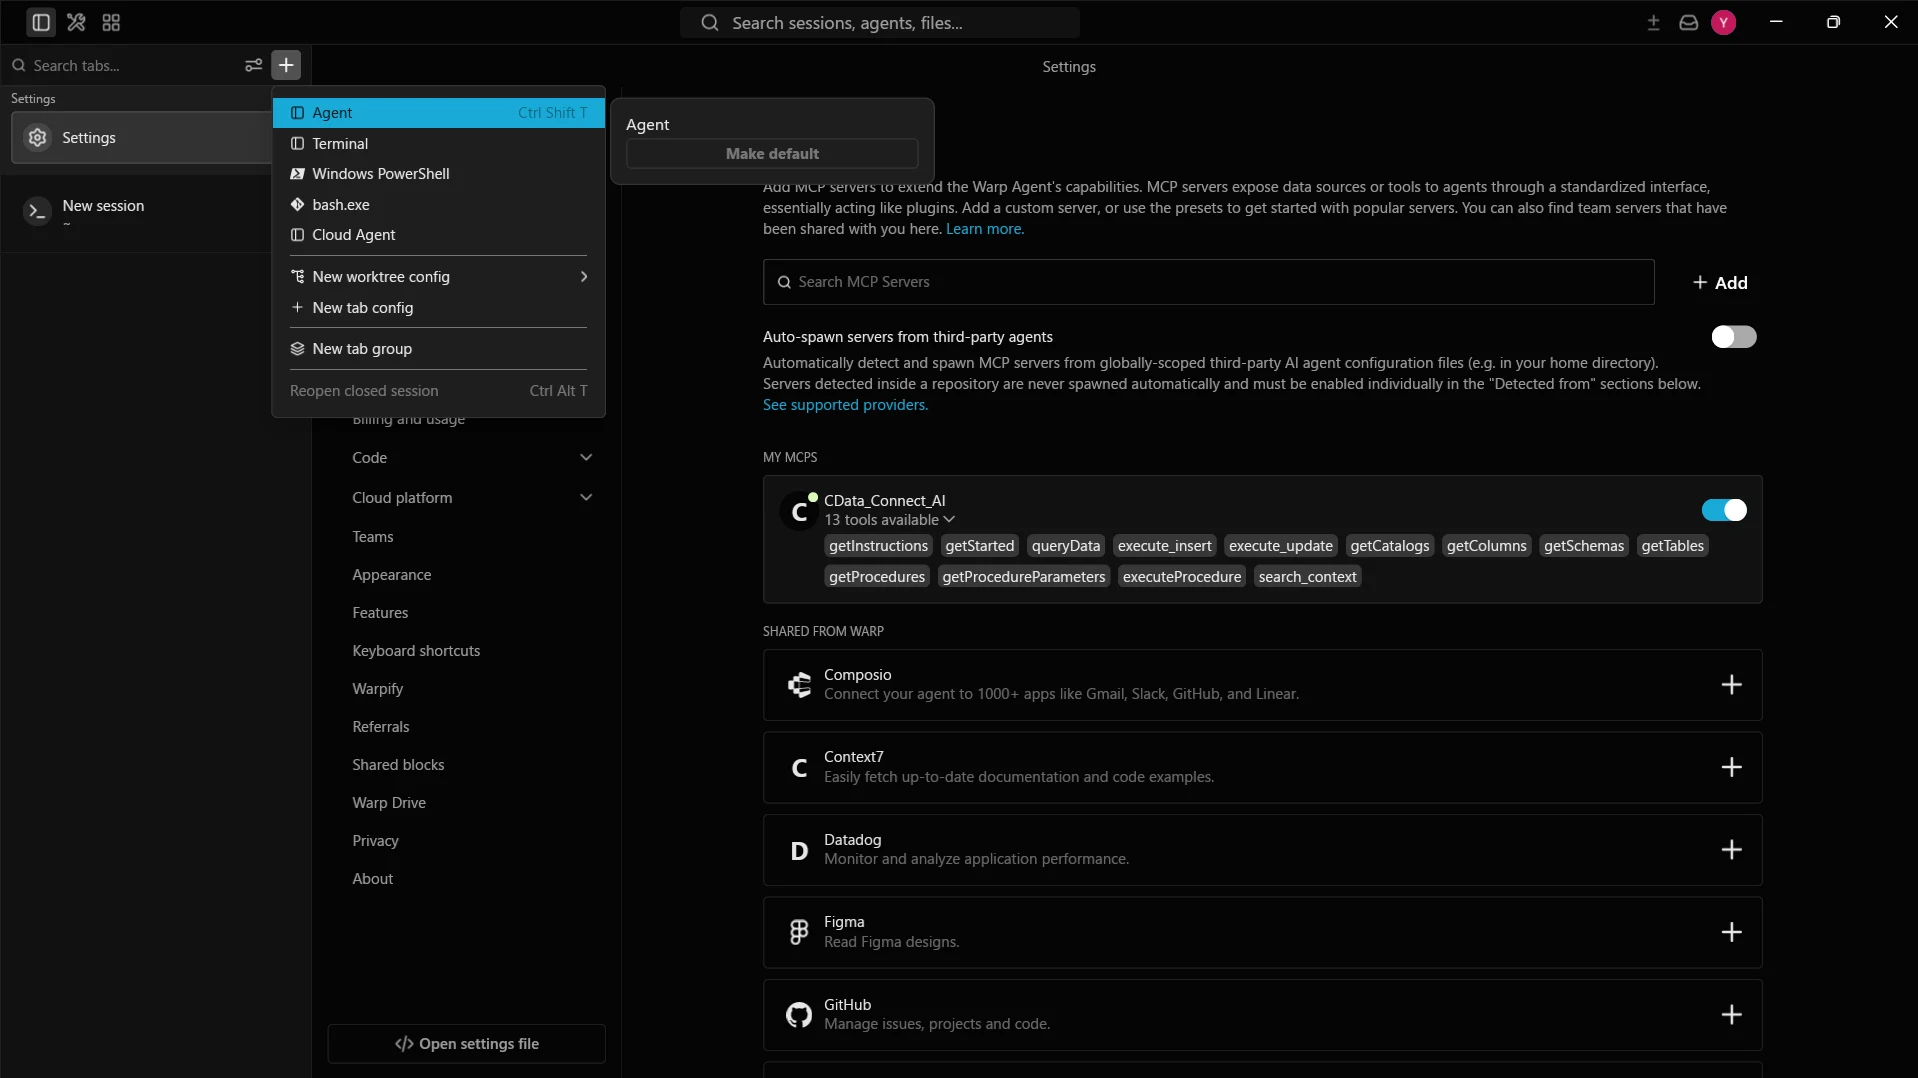
Click the icon in the left navigation bar and select Agent
-
Enter a prompt to interact with your data, for example:
- List the sources available in my CData_Connect_AI mcp connection
- Show me what I can explore in PingOne
- Fetch the five most recent records from PingOne data
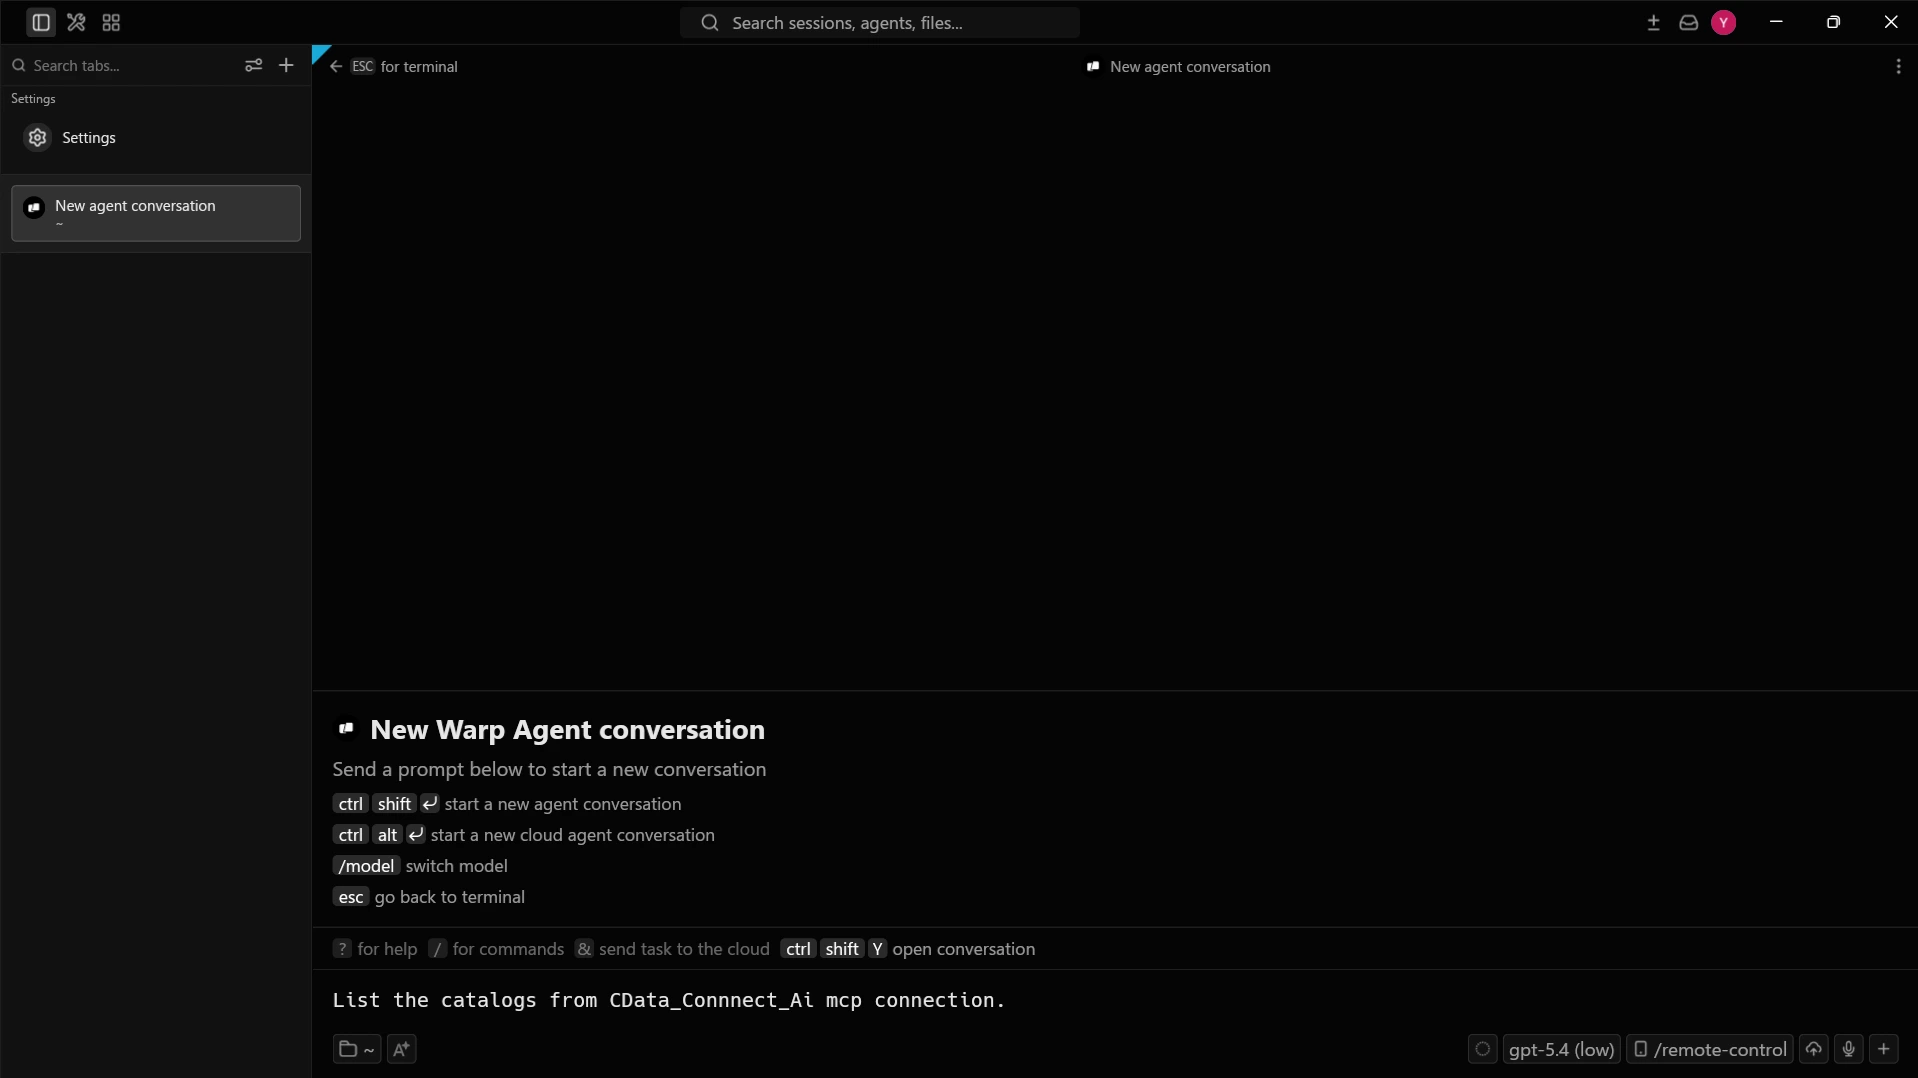
-
The agent calls the Connect AI MCP Server and returns live results from PingOne data
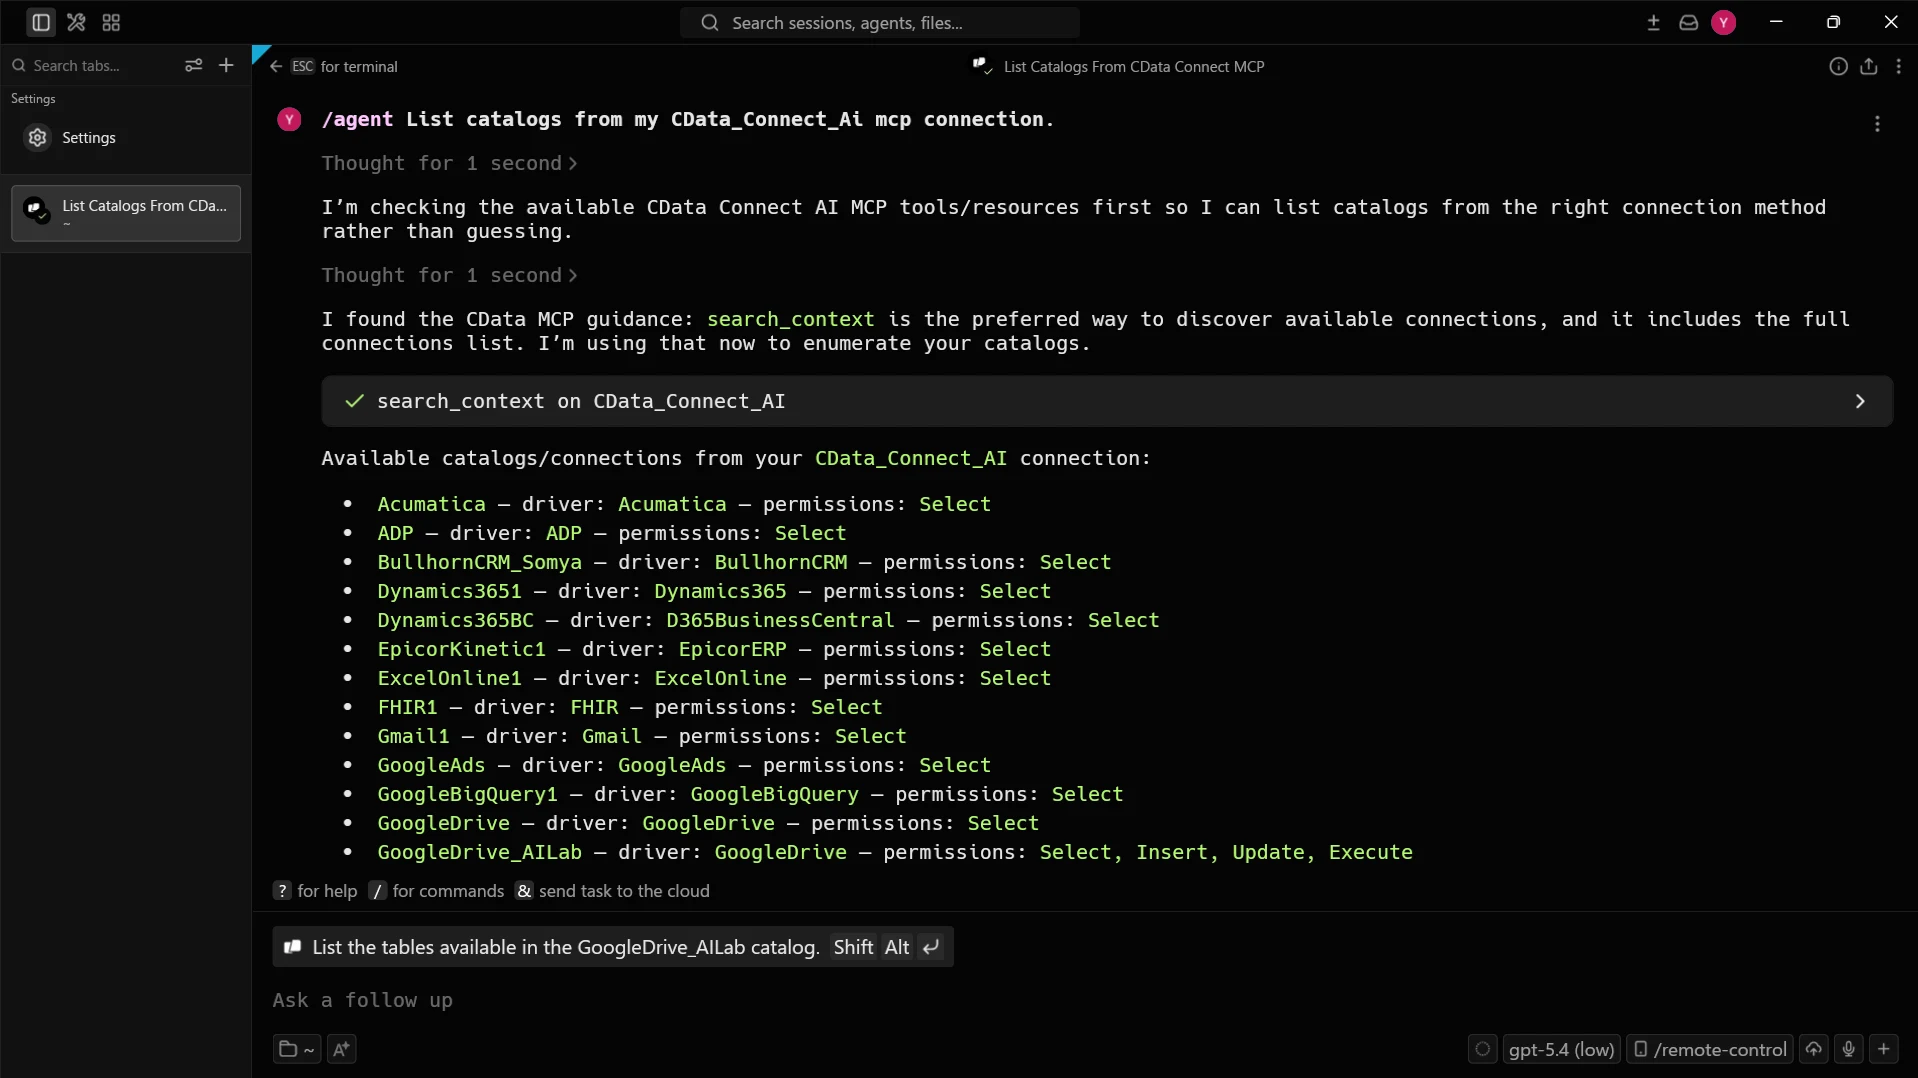
Your Warp Agent now calls the Connect AI MCP Server to interact with live PingOne data through remote MCP tools, all from the terminal.
Get CData Connect AI
To interact with hundreds of SaaS and enterprise data sources directly from your AI agents and cloud applications, try CData Connect AI. Download a free 14-day trial of CData Connect AI, and our Support Team is available to answer any questions.