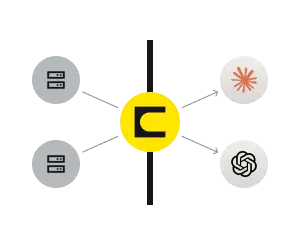
Claude and ChatGPT can connect easily to hundreds of cloud applications, but on-premises data is harder to reach. It sits behind firewalls, often in critical databases and business systems protected by strict access controls.
The challenge is controlling what data AI can access, which credentials it uses, and how that activity is audited.
This guide explains how to connect on-premises data to Claude and ChatGPT securely using the model context protocol (MCP), from the underlying architecture and setup process to the security practices needed in production.
Understanding on-premises data integration challenges
On-premises environments were built to keep data internal, so opening them to a cloud AI tool runs against their design. Three constraints come up in nearly every project.
Network boundaries: internal databases and applications are not exposed to the internet, so a cloud AI tool has no direct path to them.
Legacy systems: many on-premises applications predate modern API access, and some offer no usable interface at all.
Security and governance mandates: regulated data carries rules about where it can be processed and who can see it, which limits what can leave your network.
CData's guide to real time data access for LLM applications explores this challenge in more detail.
Introducing MCP for secure AI data access
MCP provides a standard way for AI applications to access external tools and data, so teams do not need to build a separate integration for every AI application.
For IT teams, the key benefit is control. MCP separates the connection across the host, client, server, and data source, with access managed at each stage. Claude or ChatGPT sends a request through MCP rather than connecting directly to the underlying database. The MCP server controls which tools are available, what operations can run, and what data is returned.
This gives AI applications live access to internal data without directly exposing the underlying systems.
Key components of connecting on-premises data to Claude and ChatGPT
A secure connection depends on four components, each handling part of the authentication, query translation, and access control.
Component | Role |
MCP client | Translates the AI's request into a structured call. |
MCP server | Authenticates the request and runs approved queries. |
Connectors | Expose only the operations and data each system may share. |
Secured data endpoints | The governed access point to each database or API. |
MCP client and server architecture
The client and server separate the AI application from the underlying data. The host is the AI application, the client manages the MCP connection, the server exposes and executes available tools, and the data source is the database, API, or business system being accessed. A request moves through four steps:
Host: receives the user's request.
Client: sends the request to the appropriate MCP server.
Server: calls the required tool to access the data source.
Response: returns the result through the client to the host.
This keeps the underlying system behind the MCP server rather than exposing it directly to the AI application.
Connectors for authentication and query translation
Connectors determine what the server is able to run in the first place. A connector is a specialized adapter that lets an AI assistant reach a tool or database while exposing only approved operations and data. Each one should carry its own authentication and permission scope, using open authorization (OAuth) or least privilege API credentials, so it reads what it needs and nothing more.
In practice, each system, such as a CRM, ERP, or internal API, typically has its own connector. For Claude, these connections follow the MCP specification, and custom connectors using remote MCP are available on paid plans.
Deployment models for on-premises data exposure
The deployment model determines how much of your internal network the AI workflow can reach, so the right approach depends on your security and compliance requirements.
Exposure model | Best suited for |
Secured reverse proxy | Exposing one internal service with tight request filtering. |
Private network link | Steady, high trust connections between your network and a cloud provider. |
VPN tunneling | Encrypted access without a permanent private link. |
Hybrid hosting | Keeping sensitive processing on-premises, with cloud AI for the rest. |
The model endpoint matters as well. Claude is available through the Anthropic API, Amazon Bedrock, and Google Vertex AI, so inference can run inside a controlled cloud environment when a public endpoint is not acceptable.
Step-by-step process to connect on-premises data
1. Inventory and classify data sources and sensitivities
Start by listing the on-premises systems AI may need to access, along with the sensitivity and compliance requirements of each. Then document the expected request patterns, so you know exactly what data and operations each connector should expose.
Data source | Classification | Intended AI use |
Customer database | Personally identifiable information (PII) | Look up account status. |
Financial ledger | Financial, regulated | Summarize approved reports. |
Support tickets | Operational | Answer ticket status questions. |
2. Choose the appropriate access and hosting model
Once the data is classified, choose where the model and connectors will run based on its sensitivity. A fully on premises deployment provides the most control but requires more infrastructure to manage. Hybrid deployments or private connections to cloud AI services are easier to operate and may suit less sensitive workloads. For highly sensitive or regulated data, a local or private cloud endpoint may be required.
3. Build and configure MCP server connectors
With the hosting model decided, the connector becomes the protocol translation layer between the model and your data. It receives requests, enforces authentication, and maps them to approved queries against the source. Keep each connector small and auditable, exposing the minimum data required. See how to connect SQL Server to Claude for a database example.
4. Harden authentication and network security
Connectors need strong controls because they sit between the AI application and your internal systems. Two risks are especially relevant: prompt injection, where malicious instructions are hidden in content the model reads, and MCP tool poisoning, where a compromised tool definition can influence how the model behaves. Reduce the risk by:
Using short lived credentials: use scoped, expiring tokens instead of shared service accounts.
Applying role-based access control: give users and connectors only the permissions required for their tasks and review access regularly.
Protecting network traffic: encrypt connections and use private networking where possible to limit public exposure.
5. Implement monitoring, data loss prevention, and auditing
Security controls reduce known risks, but monitoring helps catch unexpected behavior. Data loss prevention (DLP) can stop sensitive information from leaving approved boundaries, while user and entity behavior analytics (UEBA) can flag unusual access patterns.
Log every AI query: record who made the request, what data was accessed, and what was returned.
Protect sensitive data: apply DLP rules to prevent restricted information from appearing in unauthorized responses or exports.
Watch for unusual activity: use UEBA to identify unexpected access patterns and alert security teams early.
6. Test retrieval accuracy and secure data handling
Before the connection goes live, confirm it behaves the way you expect. Run staged scenarios using retrieval-augmented generation (RAG) to check retrieval against real queries. Redact sensitive or unnecessary fields and verify that the assistant cannot surface them through an indirect question. Field level logs make each retrieval traceable during an audit.
7. Establish governance, approval, and incident response policies
Policy is what keeps these controls current as systems change. Put approval flows, retention schedules, and an incident response plan for AI incidents in place, then review connector access on a schedule and run role attestations. Aligning each control to a framework makes audits simpler:
Policy area | Control | Framework |
Access review | Scheduled connector and role attestation. | SOC 2, ISO 27001 |
Data handling | Field redaction and retention limits. | GDPR |
Audit | Query level logging to a monitored store. | SOC 2, ISO 27001 |
Best practices from real-world enterprise AI deployments
TELUS built its Fuel iX platform on Google Cloud and uses Claude through Vertex AI, with 57,000 team members building more than 13,000 custom AI solutions. Bridgewater uses Claude through Amazon Bedrock for its Investment Analyst Assistant, which generates Python, works through errors, and produces charts and tables for investment research.
Both show how enterprises can use Claude through managed cloud platforms while maintaining control over how AI is deployed and governed.
Keep connectors focused and auditable: smaller, well-scoped connectors are easier to review, secure, and monitor.
Expose only what is needed: limit data, fields, and operations to what each use case requires.
Match the deployment to the risk: use private or local model endpoints when sensitive or regulated workloads require tighter control.
Frequently asked questions
How do I connect on-premises data to Claude or ChatGPT?
Set up a secure MCP server or connector that mediates requests between the AI tool and your internal sources, so only approved queries and data are accessible.
Is connecting on-premises data secure?
Yes, with strong authentication, least privilege access, encrypted network connections, and active monitoring. The model reaches data only through layers your team controls.
What types of data sources can I connect?
Databases, file stores, REST APIs, GraphQL endpoints, SaaS platforms, and other internal services, through connectors or an MCP server.
Do I need to write code to set up integration?
Some platforms offer low code setups, but a secure on-premises integration usually requires a small server or connector to enforce your controls.
How can I control what data AI assistants access?
Expose only selected fields, set strict permissions, require approvals for sensitive operations, and use connectors that restrict which actions and data are reachable.
Connecting on-premises data with CData Connect AI
Building and maintaining this architecture yourself means owning the client, the server, every connector, and the security controls around them. A managed MCP server removes most of that work.
CData Connect AI handles authentication, query translation, and secure exposure of on-premises databases and applications to Claude, ChatGPT, and other AI tools, while enforcing the access controls already in place at the source. Each request runs under the user's identity and inherits permissions from the source system, and every action is recorded in centralized audit logs.
Deployment becomes a single managed connection per source rather than a custom build. You can read more about building custom MCP tools for on-premises data or even start a free trial to see how it works with your own data.
Explore CData Connect AI today
See how Connect AI excels at streamlining AI and business processes for real-time insights and action.