


Build Apps with Live PingOne data in Adalo using CData Connect AI

Adalo is a no-code platform used to build custom mobile and web applications without needing programming skills. It allows users to design interfaces, manage databases, and integrate functionality through simple drag-and-drop tools, making app development accessible and efficient. When combined with CData Connect AI, it provides access to PingOne data to build custom applications and more.
This article explains how to use CData Connect AI to create a live connection to PingOne and how to connect and access live PingOne data from the Adalo platform.
Configure PingOne connectivity for Adalo in CData Connect AI
To work with PingOne data in Adalo, we need to connect to PingOne from Connect AI, provide user access to the connection, and create OData endpoints for the PingOne data.
Connect to PingOne from Connect AI
CData Connect AI uses a straightforward, point-and-click interface to connect to data sources.
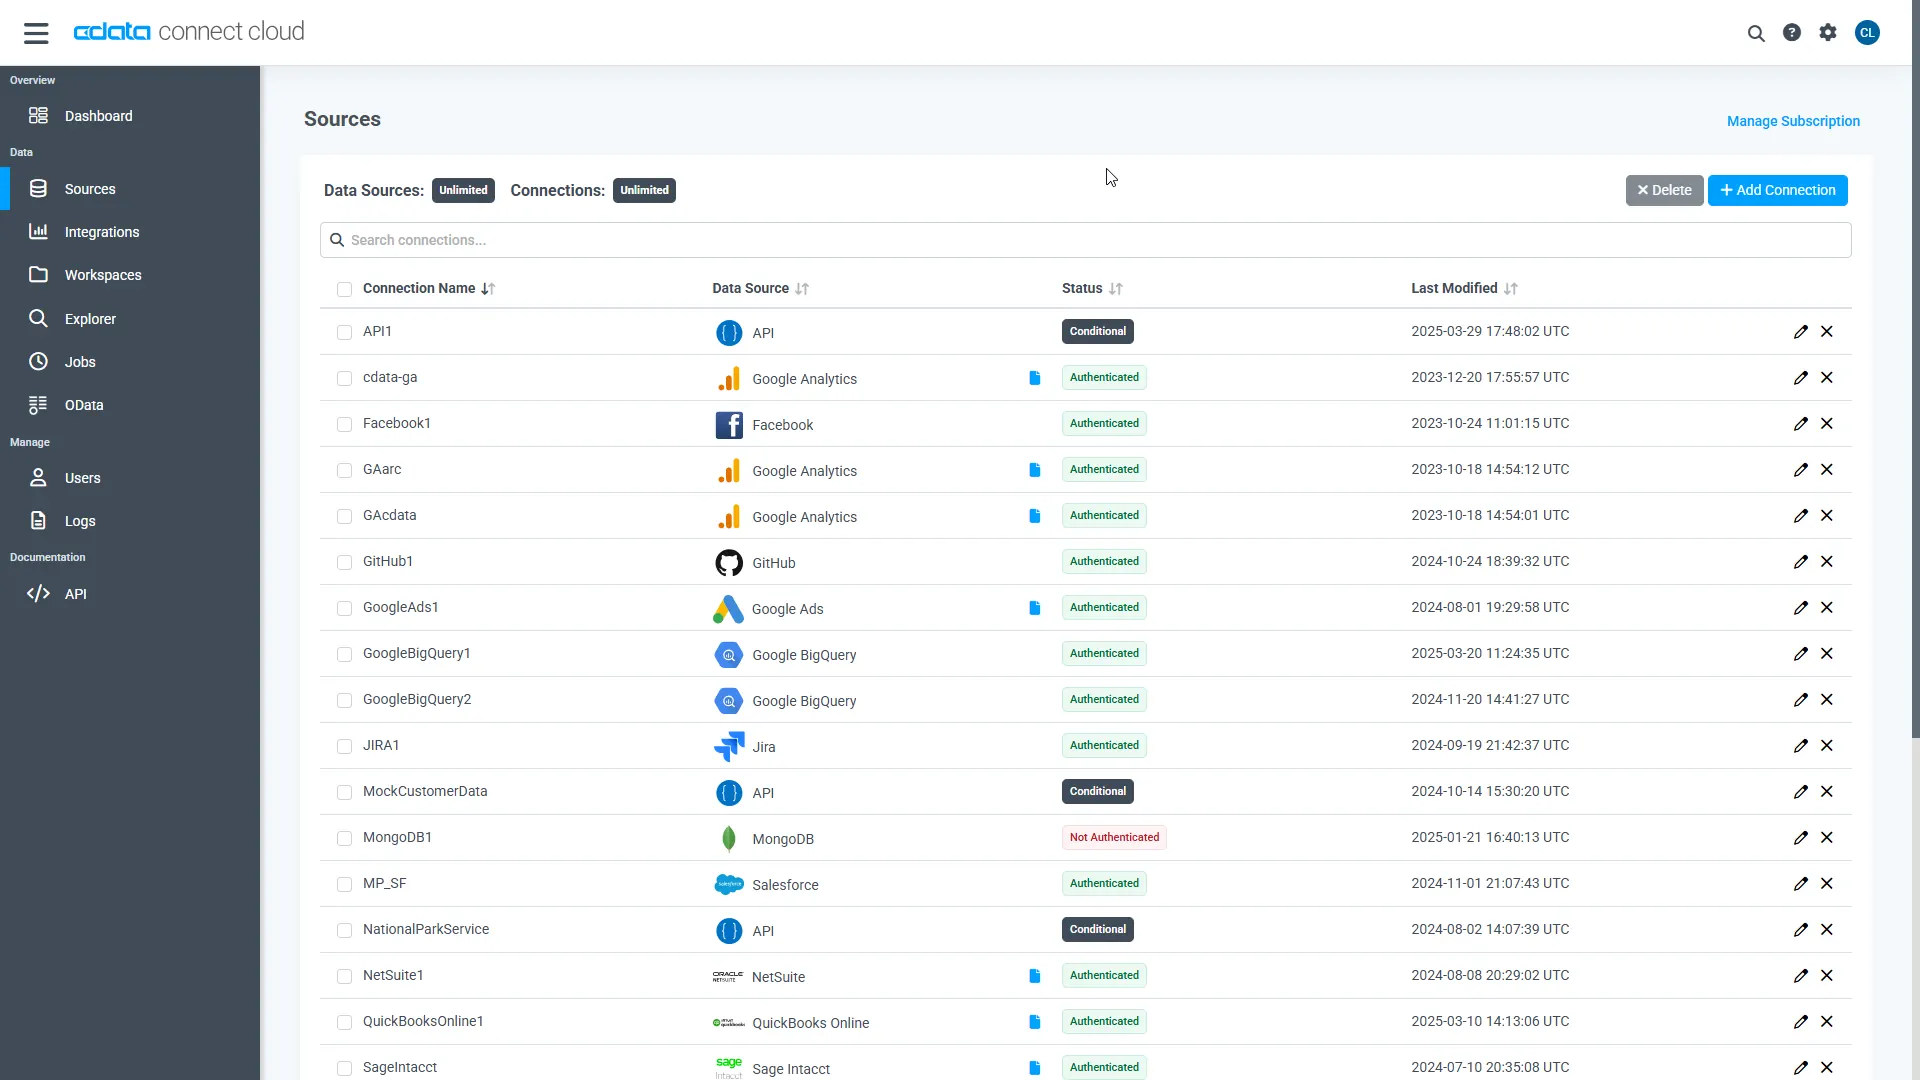
- Log into Connect AI, click Sources, and then click Add Connection
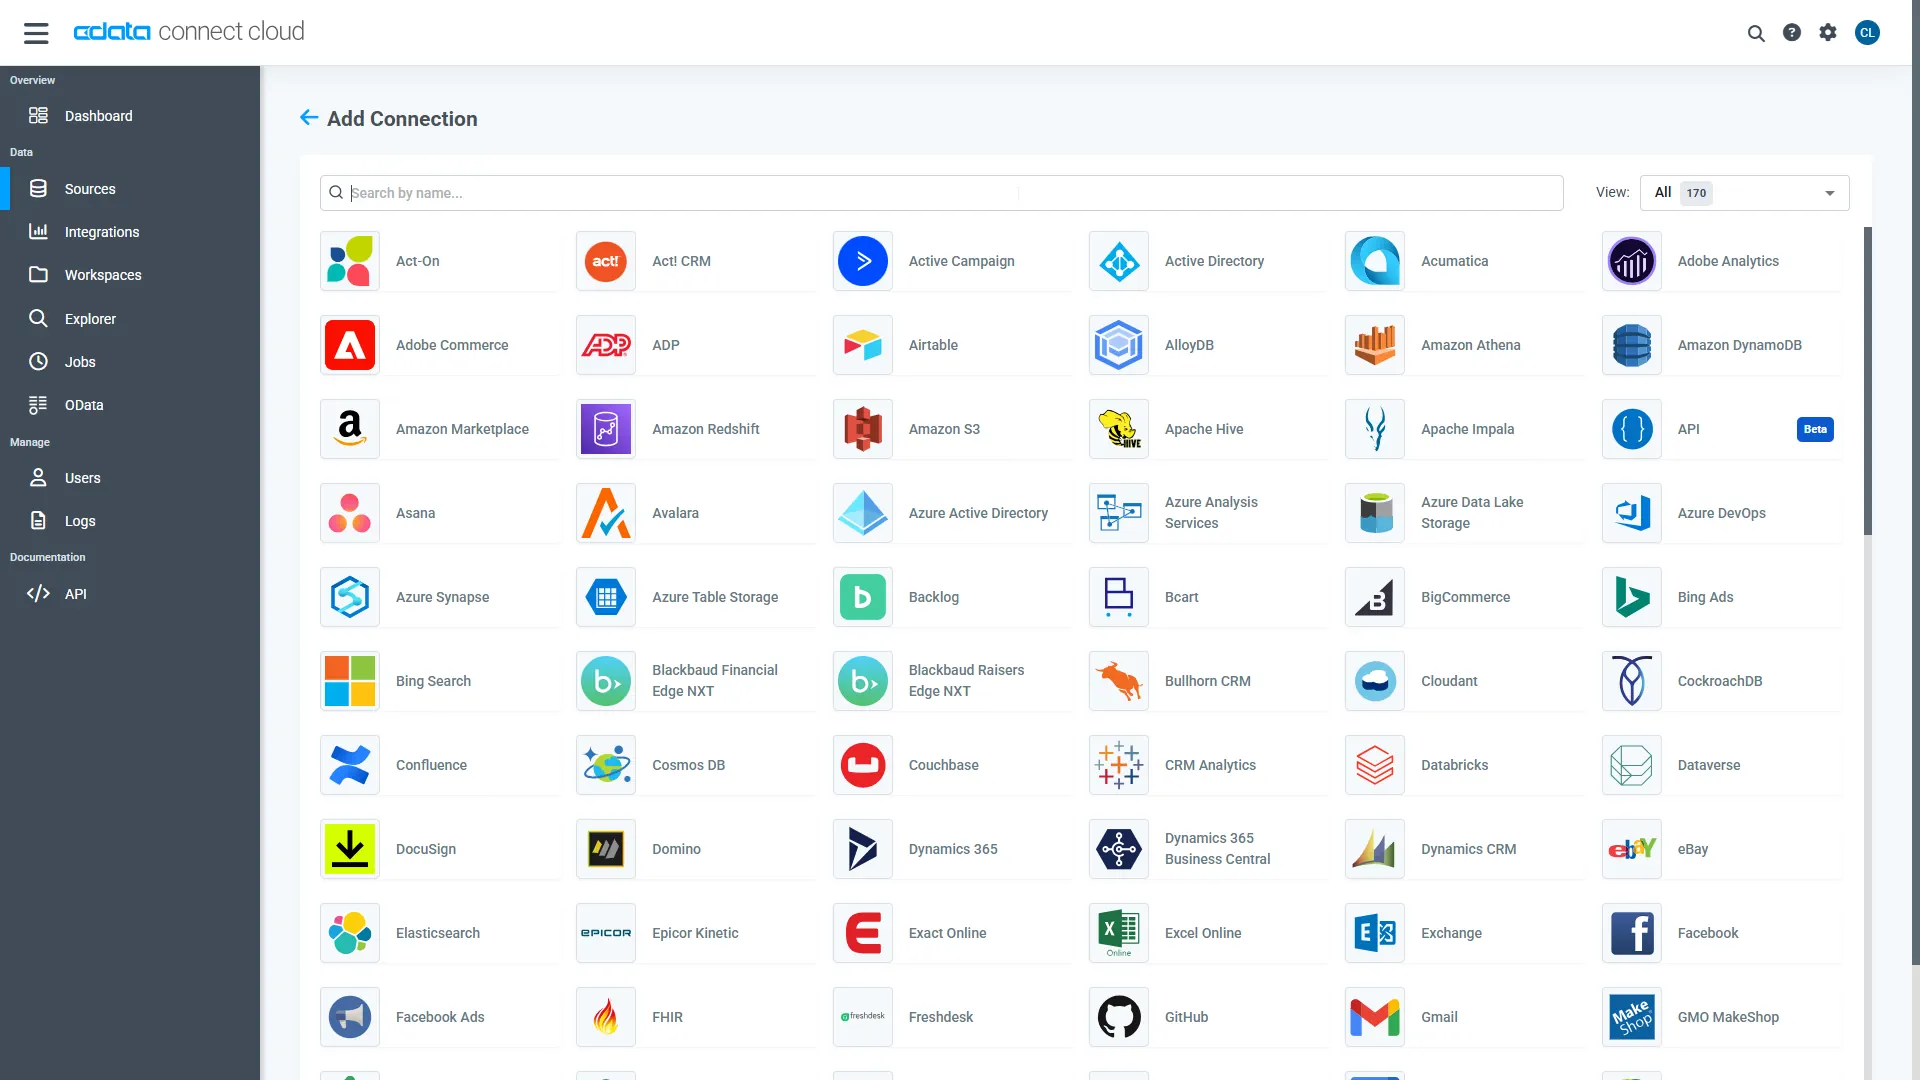
- Select "PingOne" from the Add Connection panel
-
Enter the necessary authentication properties to connect to PingOne.
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
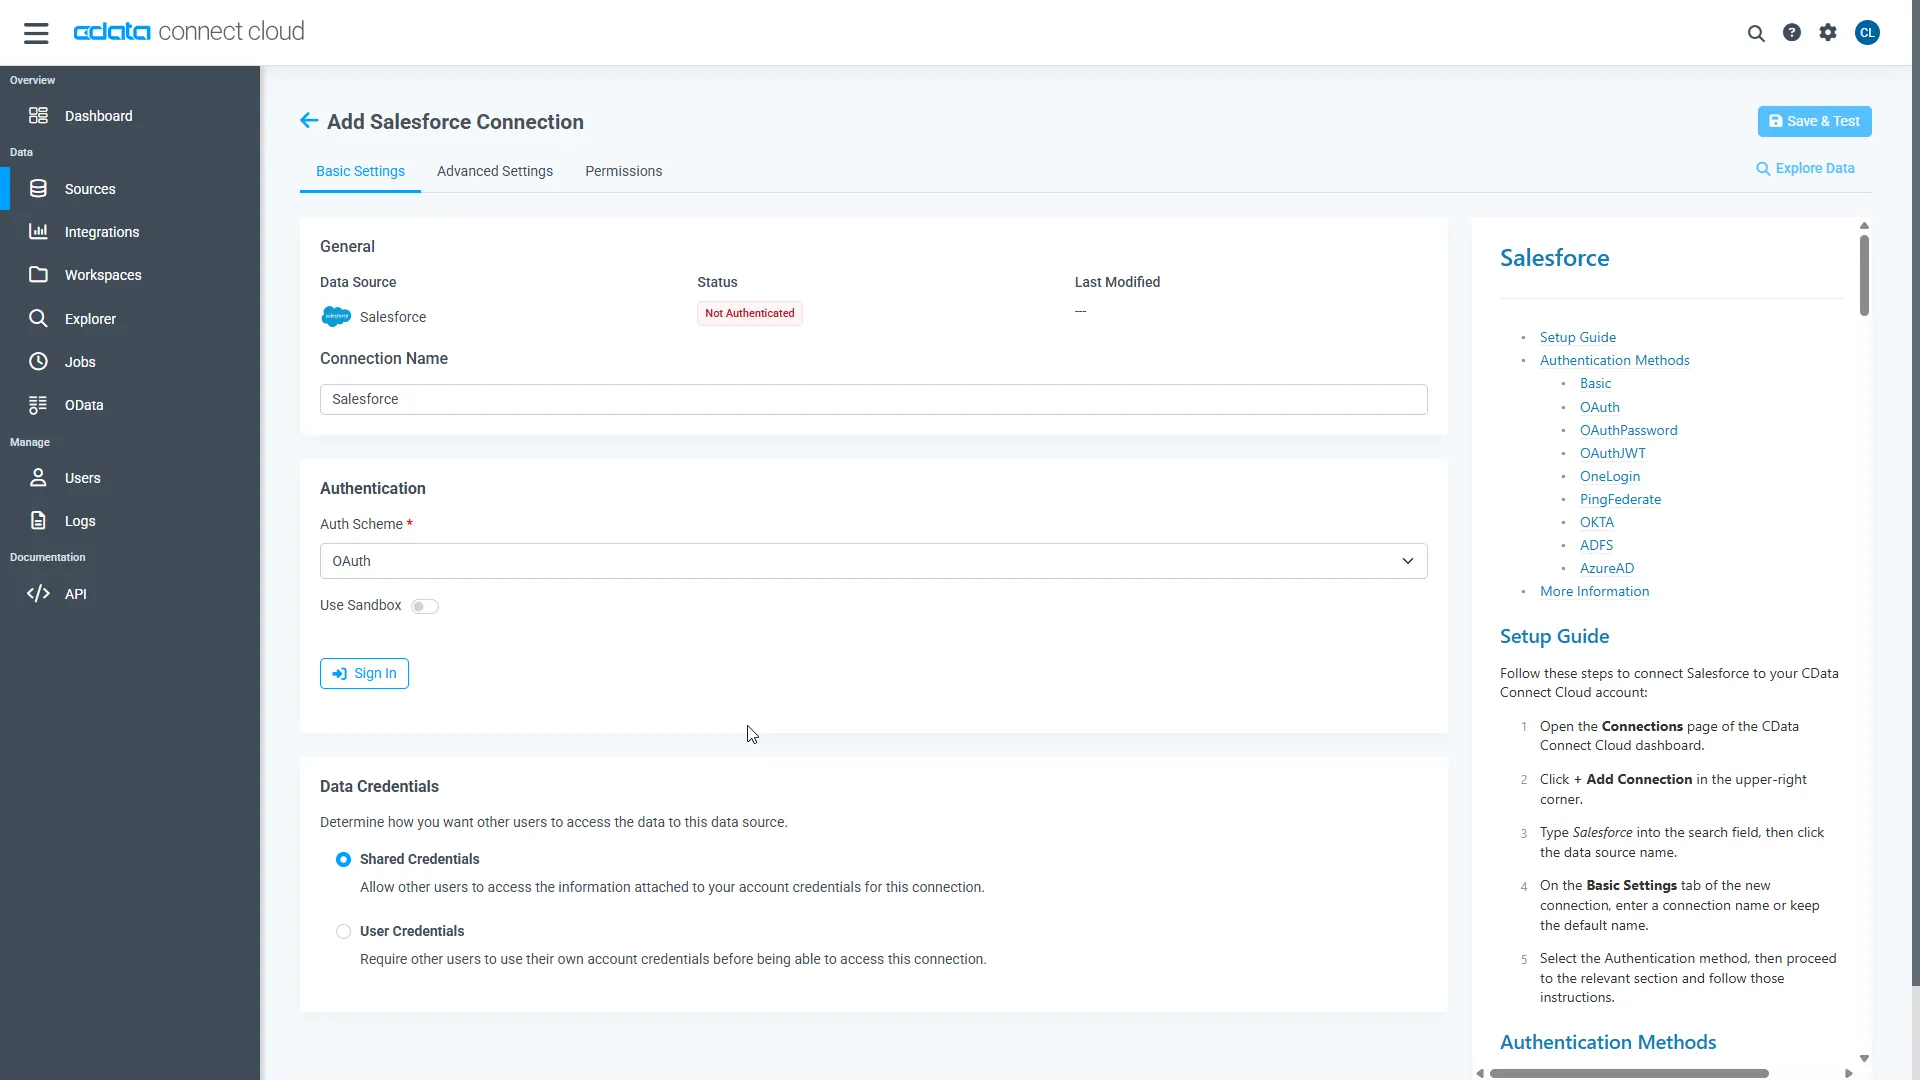
- Click Save & Test
-
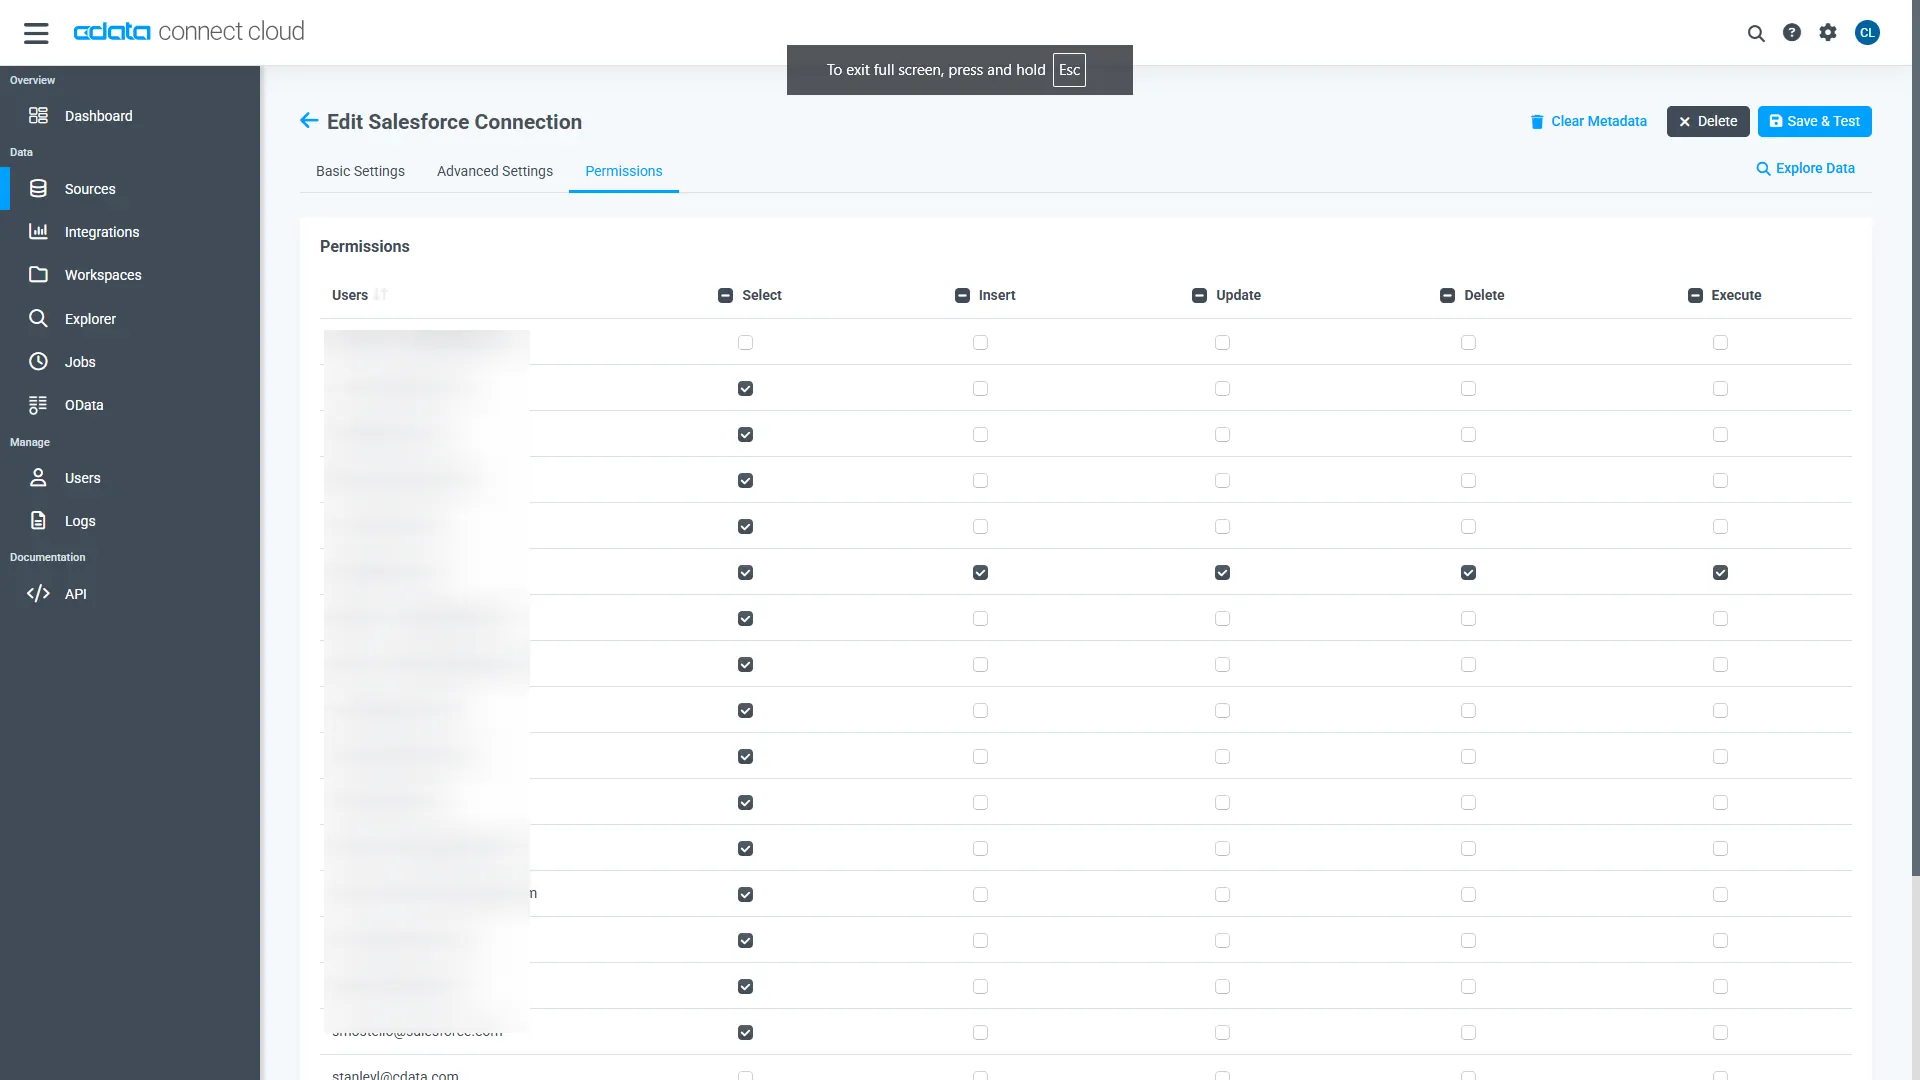
Navigate to the Permissions tab in the Add PingOne Connection page and update the User-based permissions.
Add a Personal Access Token
When connecting to Connect AI through the REST API, Workspaces, or the Virtual SQL Server, a Personal Access Token (PAT) is used to authenticate the connection to Connect AI. It is best practice to create a separate PAT for each service to maintain granularity of access.
- Click on the Gear icon () at the top right of the Connect AI app to open the settings page.
- On the Settings page, go to the Access Tokens section and click Create PAT.
-
Give the PAT a name and click Create.
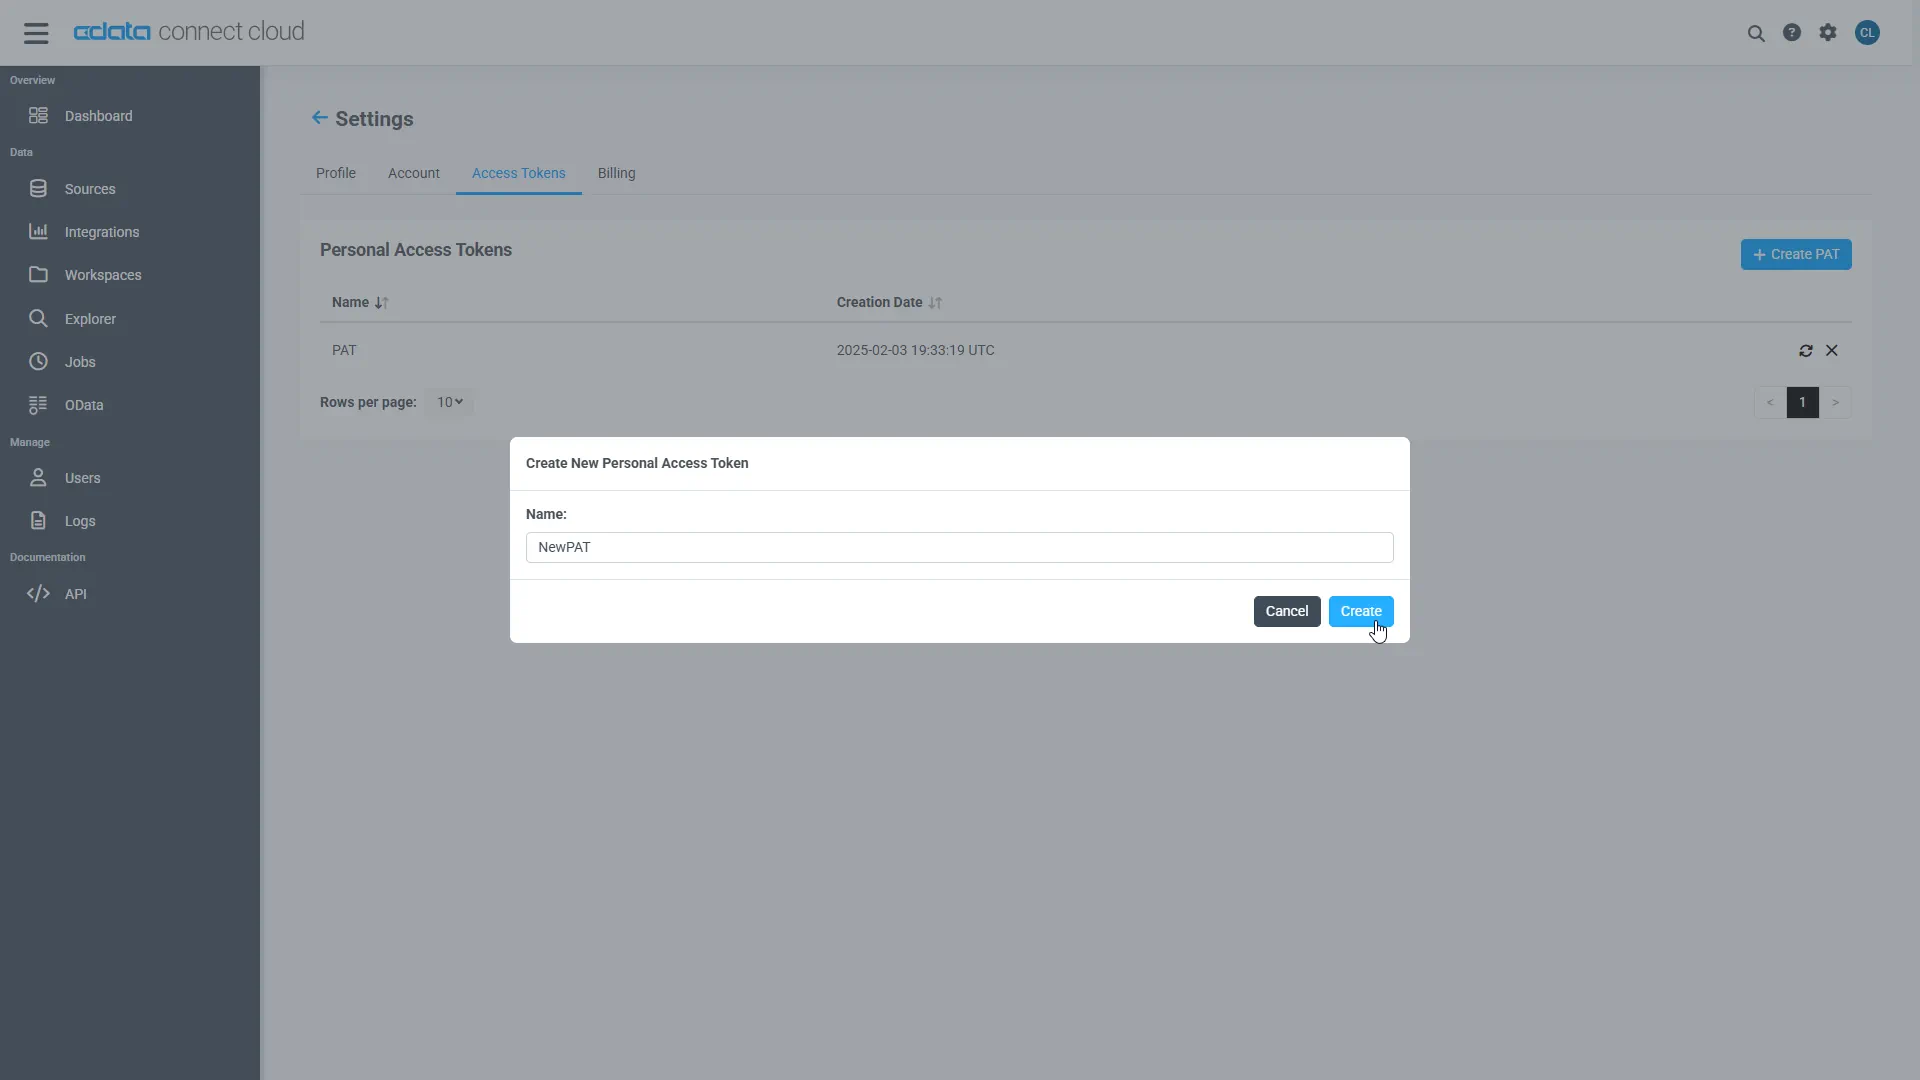
- The personal access token is only visible at creation, so be sure to copy it and store it securely for future use.
Configure PingOne Endpoints for Adalo
After connecting to PingOne, create a workspace for your desired table(s).
-
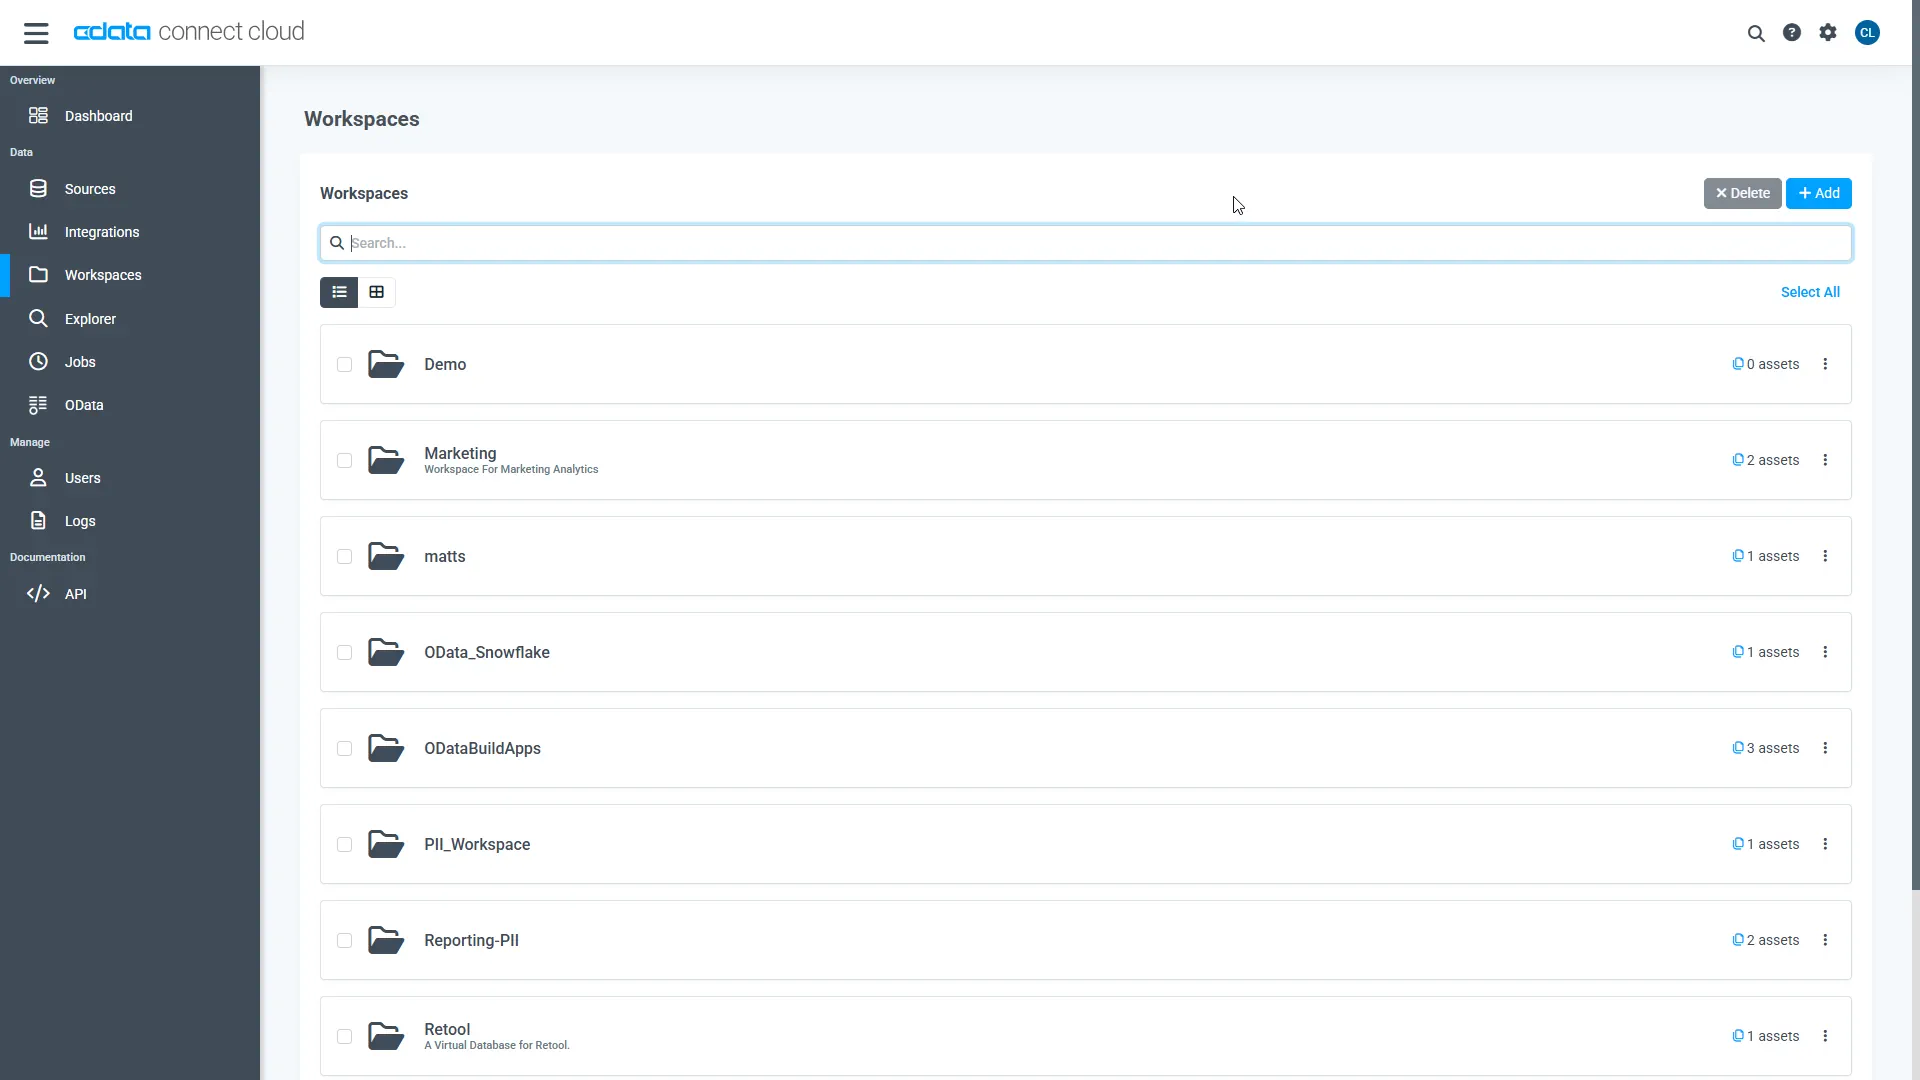
Navigate to the Workspaces page and click Add to create a new Workspace (or select an existing workspace).
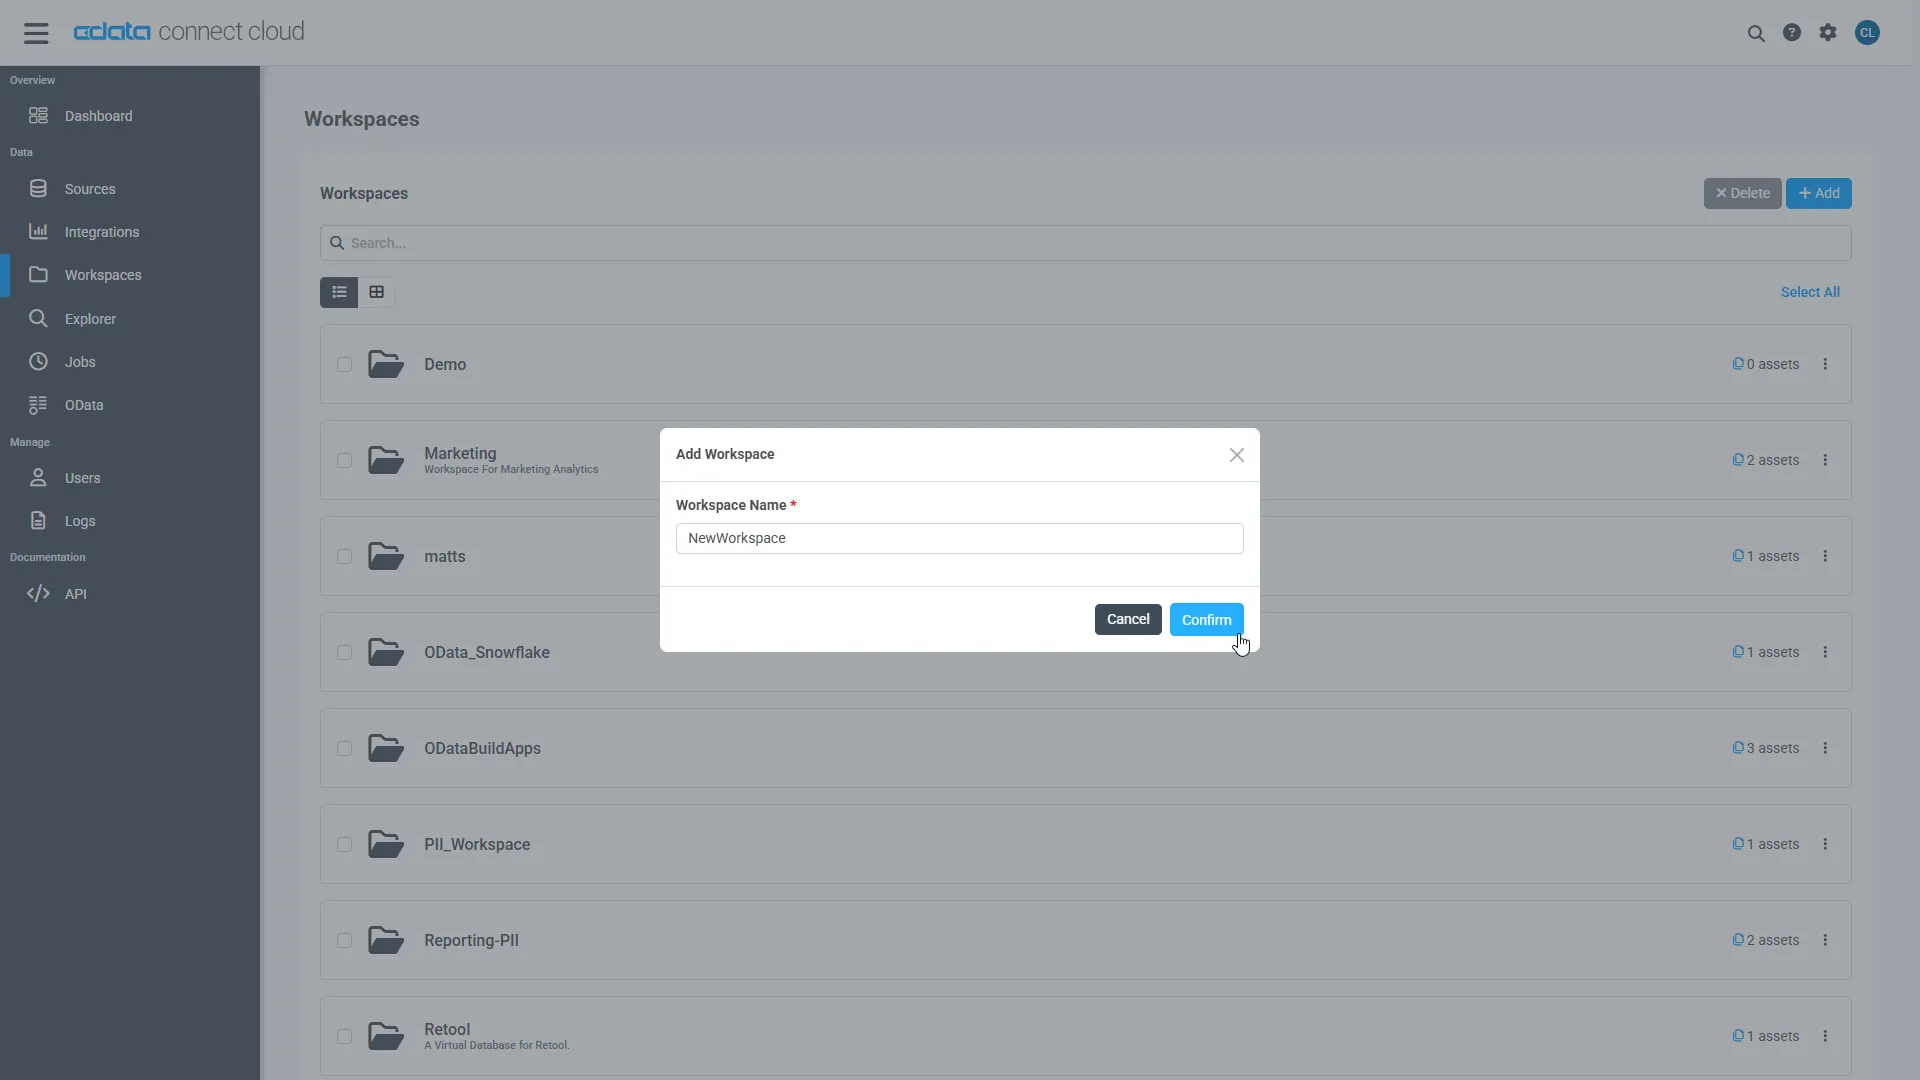
- Click Add to add new assets to the Workspace.
-
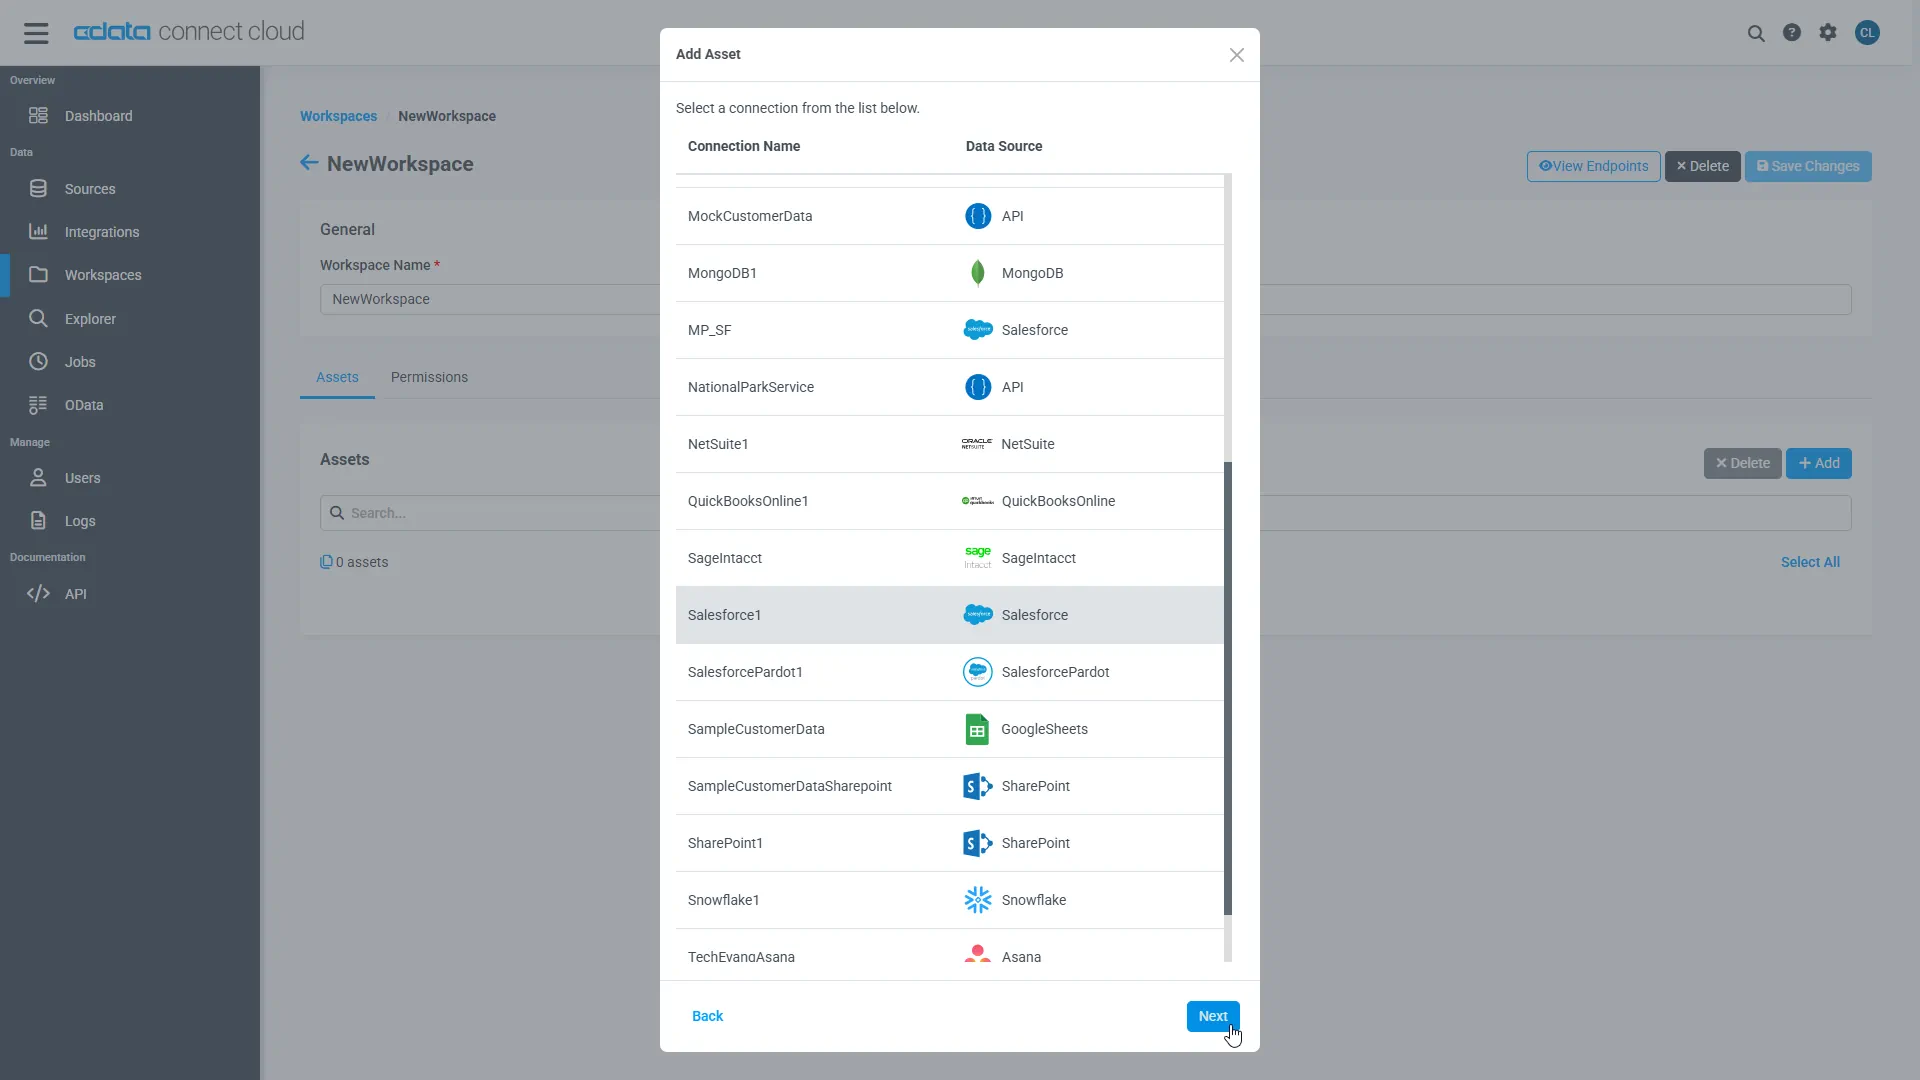
Select the PingOne connection (e.g. PingOne1) and click Next.
-
Select the table(s) you wish to work with and click Confirm.
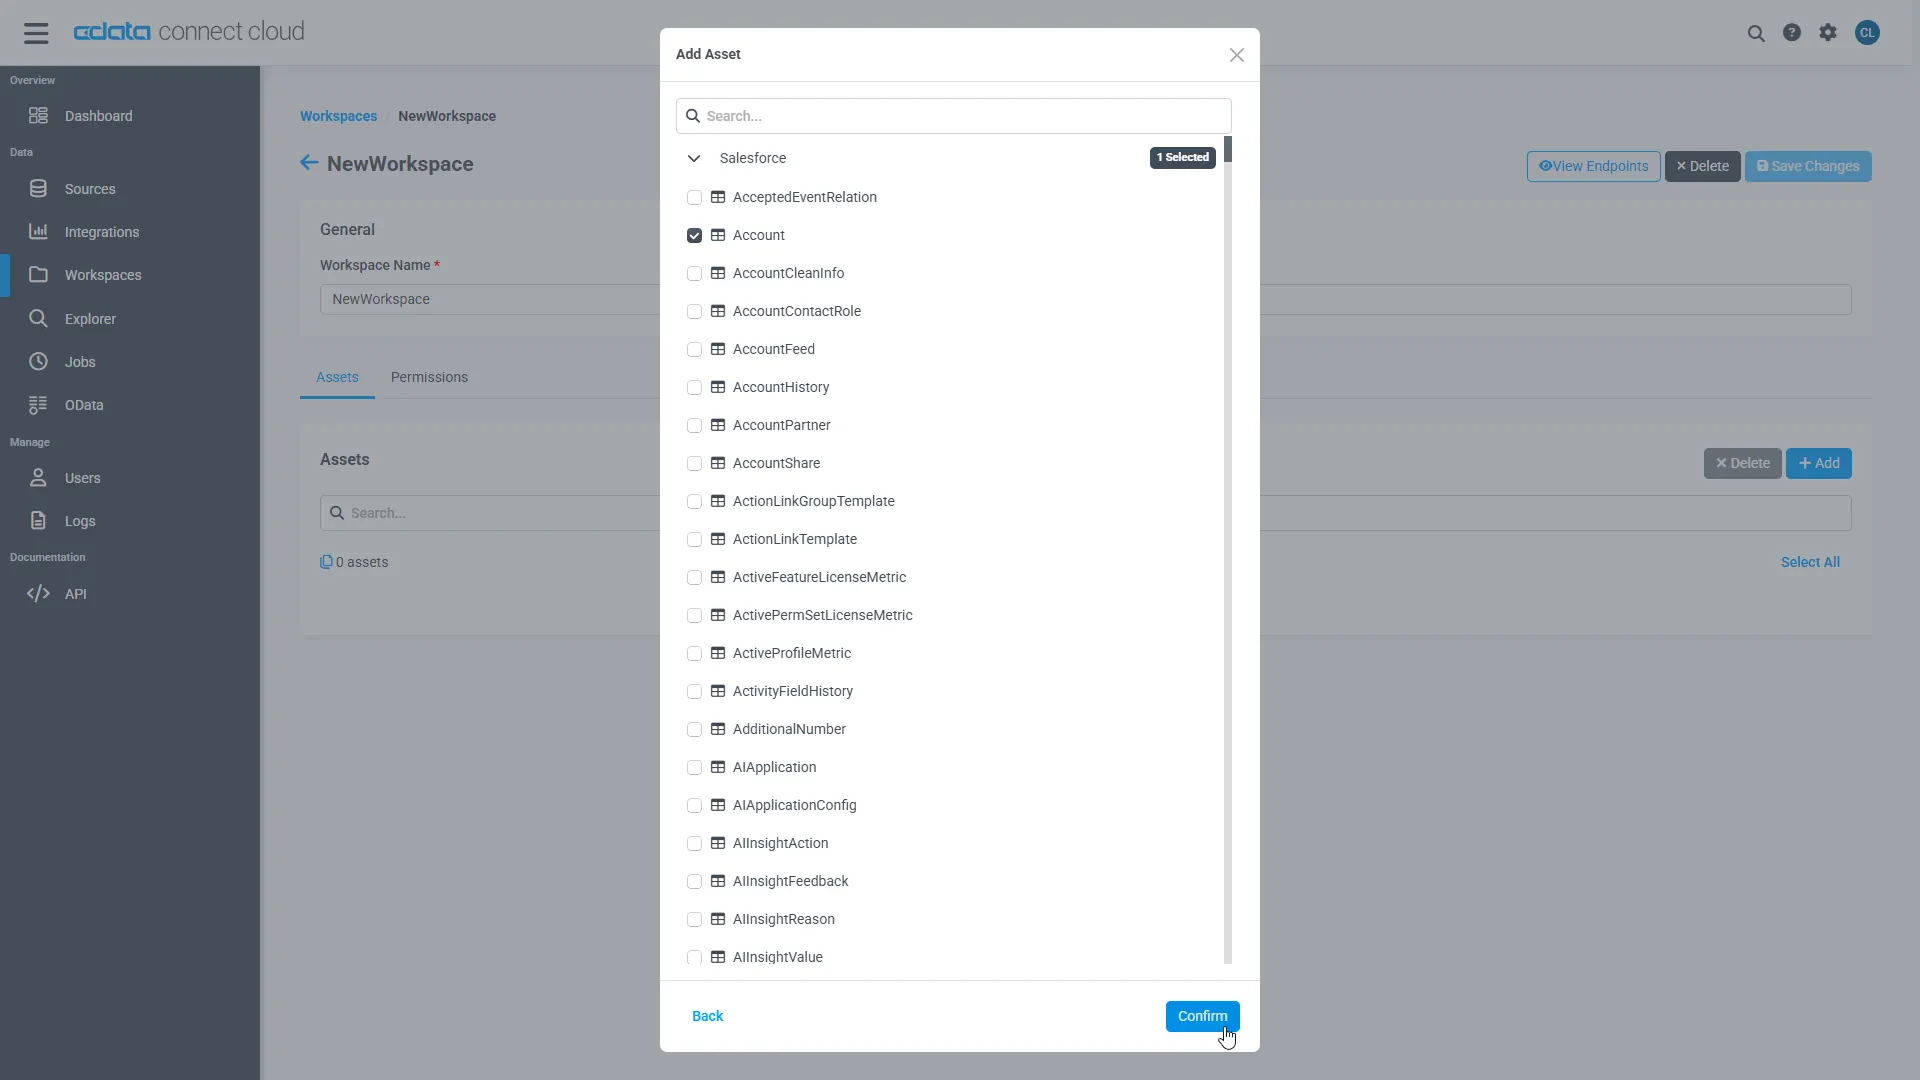
- Make note of the OData Service URL for your workspace, e.g. https://cloud.cdata.com/api/odata/{workspace_name}
With the connection, PAT, and Workspace configured, you are ready to connect to PingOne data from Adalo.
Build a custom app with Adalo
After configuring CData Connect AI, you can begin developing the Adalo app using PingOne data.
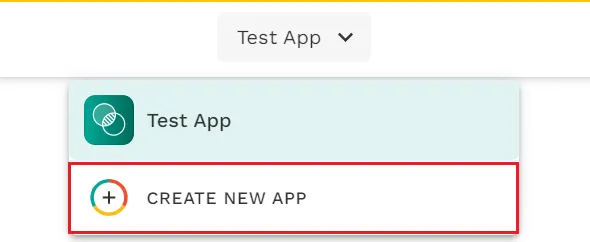
- Click on CREATE NEW APP.
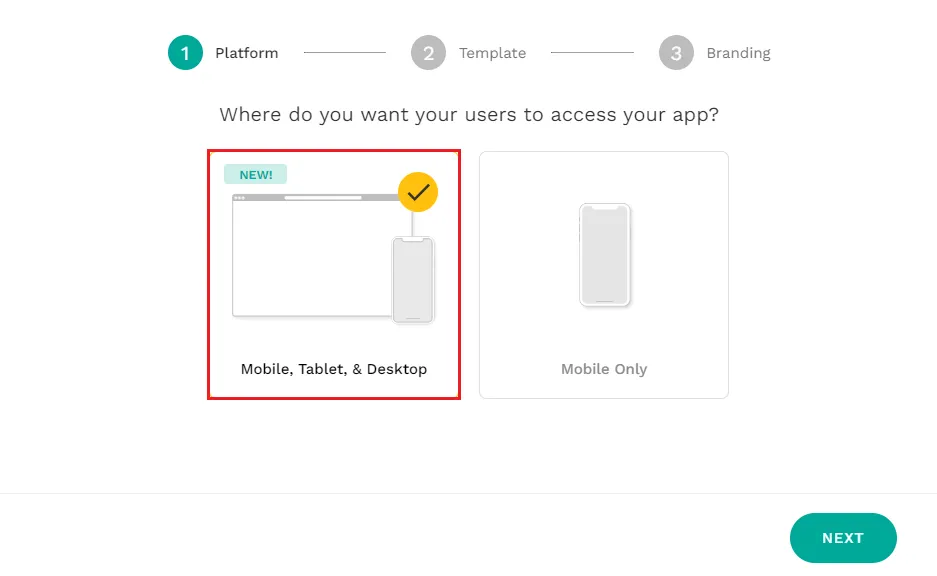
- Select Desktop Web App and click on Next.
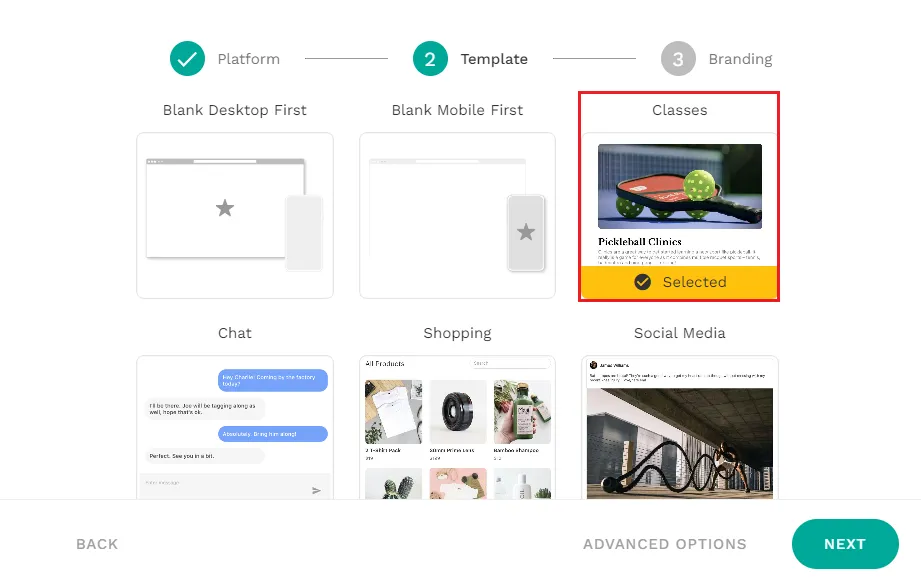
- You can choose any template, but for testing purposes, we've chosen a Blank template.
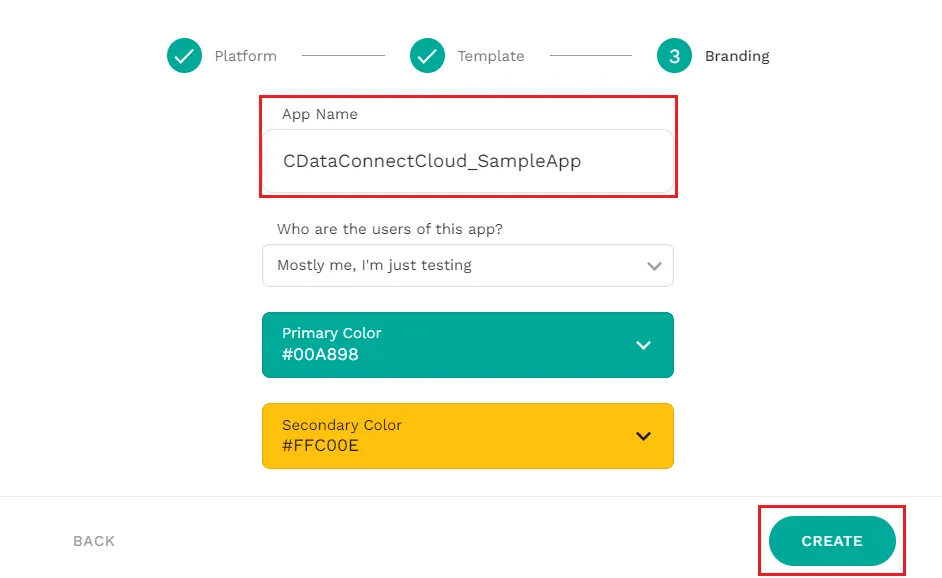
- Finally, add an app name and choose a color scheme, and your app is ready to go!
Registering external collections
Adalo uses a data structure called Collection to manage app data and offers a feature called External Collections with APIs, which lets you seamlessly integrate Collection with external APIs. Use this feature to connect to Connect AI.
- After creating an app, you first need to register a Collection, which is a definition for handling data within the Adalo app. There are two types of Collections: Database Collections, which are like Adalo's own internal database, and External Collections, which allow access to external APIs. In this case, we will access an external API, registering it as an External Collection.
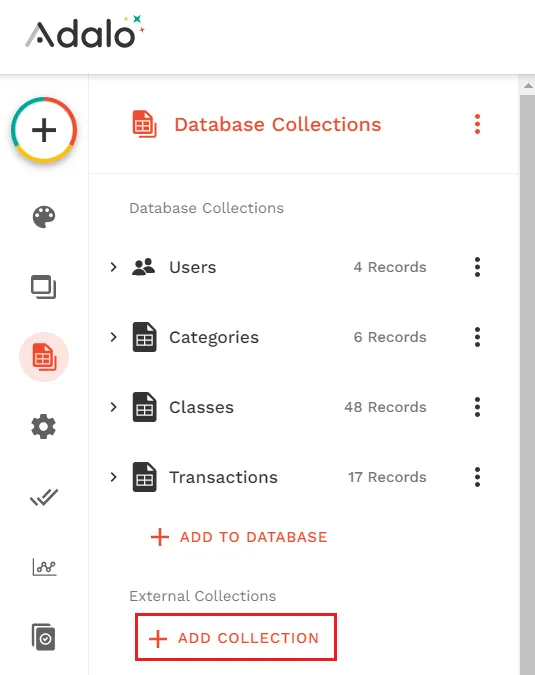
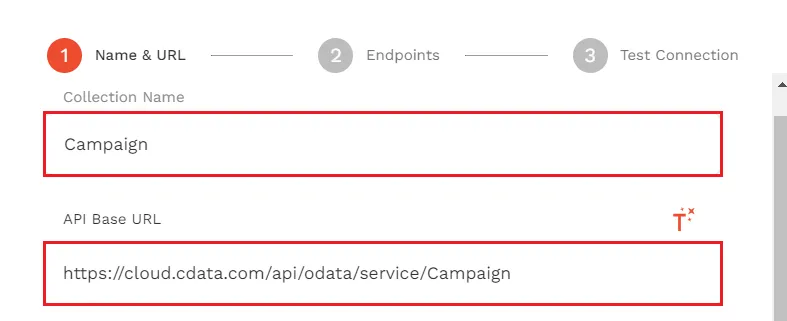
- On the External Collections registration screen, click on ADD COLLECTION to enter the collection name (any name of your choice), and provide the API base URL endpoint (OData endpoint registered on Connect AI). Make sure to add "/(table)" to the OData URL to access the specific endpoint. (Refer to the image given for reference)
- In order to authenticate, you need a base64 authorization header comprising your username and PAT, joined by a colon. For example, [email protected]:MY_PAT. You can use a scripting tool, web tool, or other application to create this header.
Using Postman to generate the Authorization header
- Open the Postman application. Enter the OData URL mentioned in the previous step for a GET request on Postman. Click on the Authorization tab and select Auth Type as "Basic Auth". Enter the Username and Password as follows and click on Send:
- Username: Connect AI Username
- Password: PAT generated on Connect AI
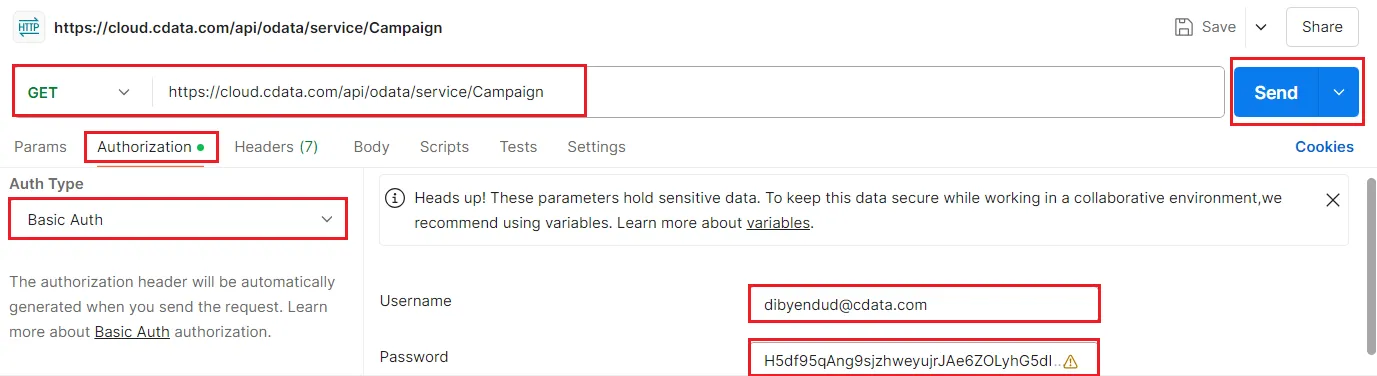
- Go to the Headers tab and copy/save the value of the Authorization key.
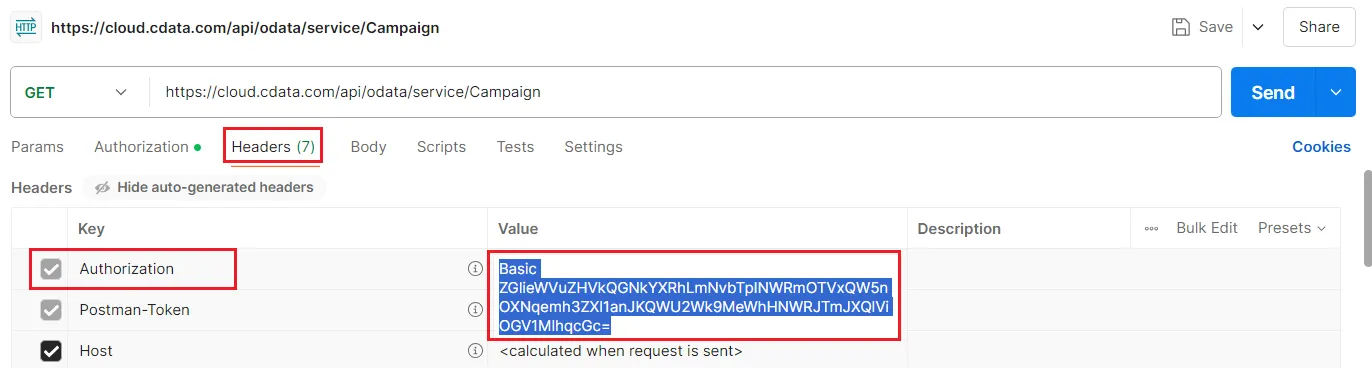
- Open the Postman application. Enter the OData URL mentioned in the previous step for a GET request on Postman. Click on the Authorization tab and select Auth Type as "Basic Auth". Enter the Username and Password as follows and click on Send:
- Back in Adalo, click on ADD ITEM and select Header.
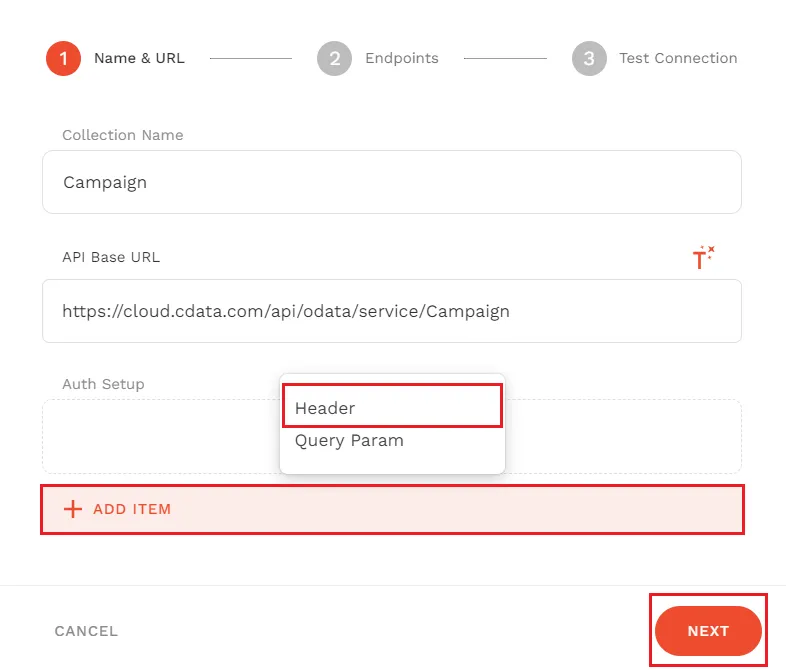
- Enter the details in the Header section as follows:
- Name: "Authorization"
- Value: Authorization key value copied in the previous step
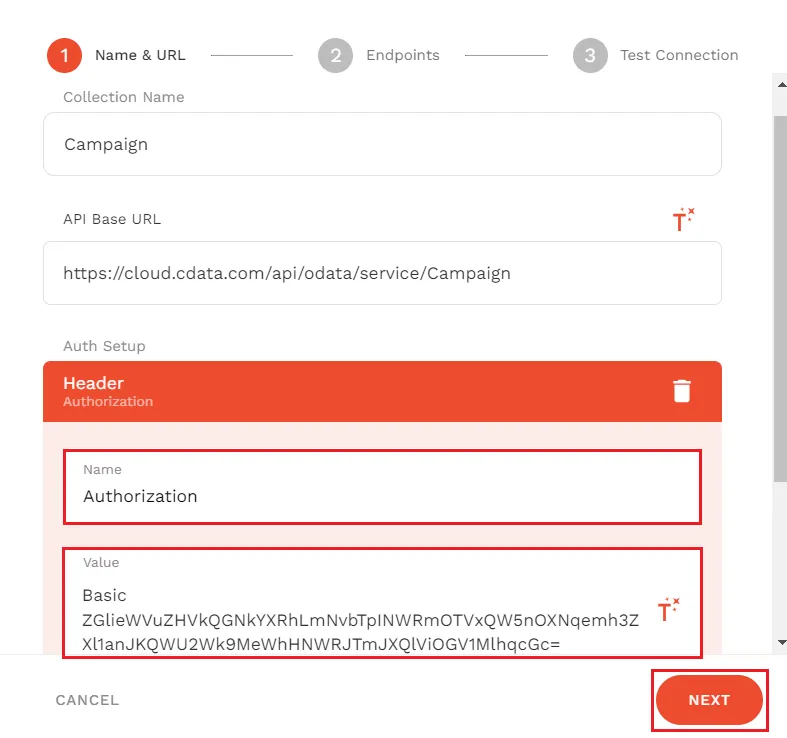
- Select Done and click on Next.
- Select Get All and enter "value" in the Results Key section. Click on Done and Next.
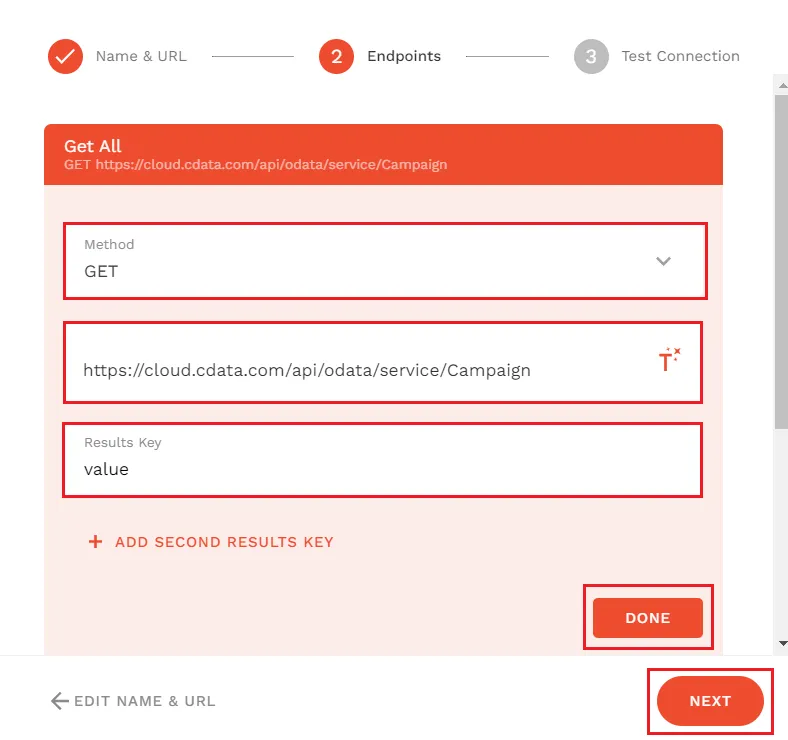
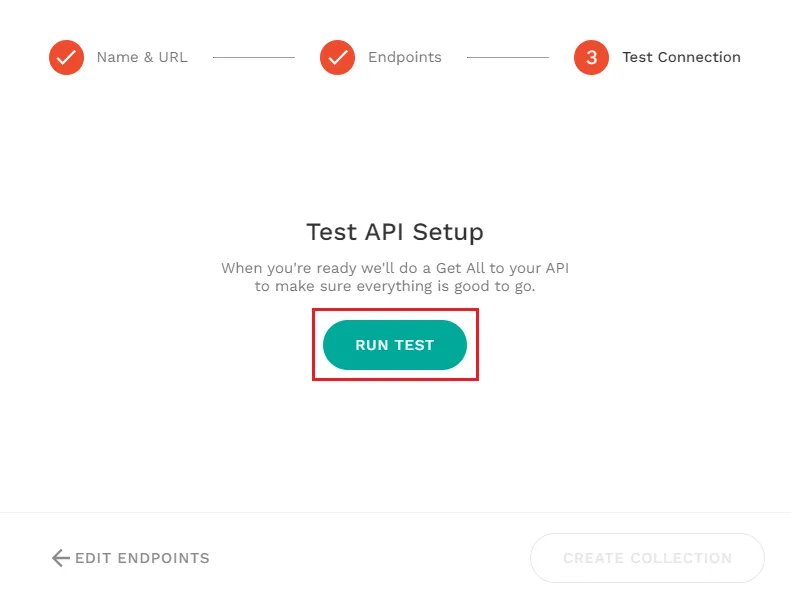
- Now, to test the API setup, click on RUN TEST. If you finally see the message and response shown below, the creation of External Collections is complete.
Creating a list screen
After configuring CData Connect AI, you can now begin developing the app on Adalo using PingOne data.
- First, click the + button in the upper right corner of the Adalo screen to display the list screen, then drag and drop "Simple List" onto the screen.
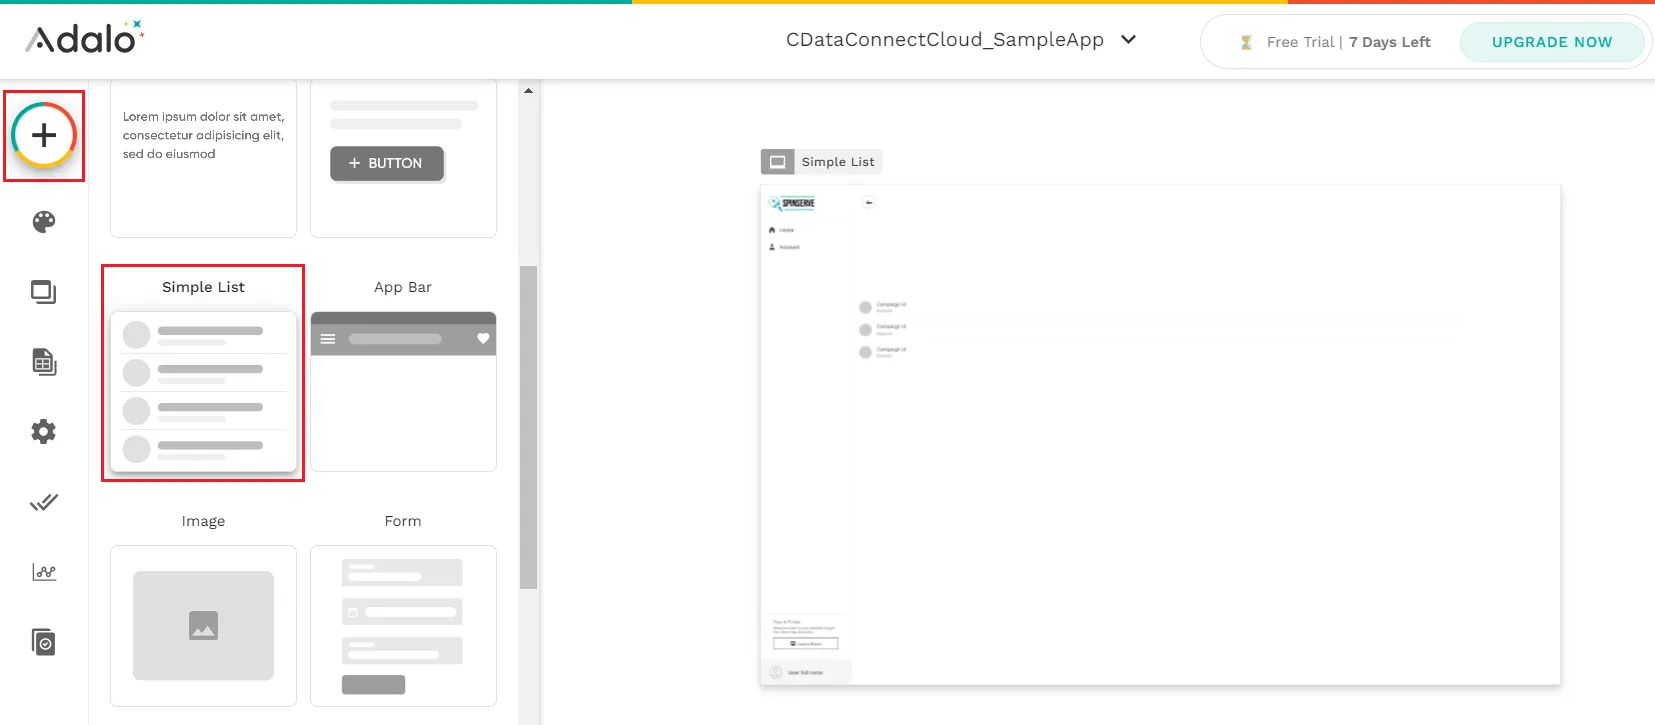
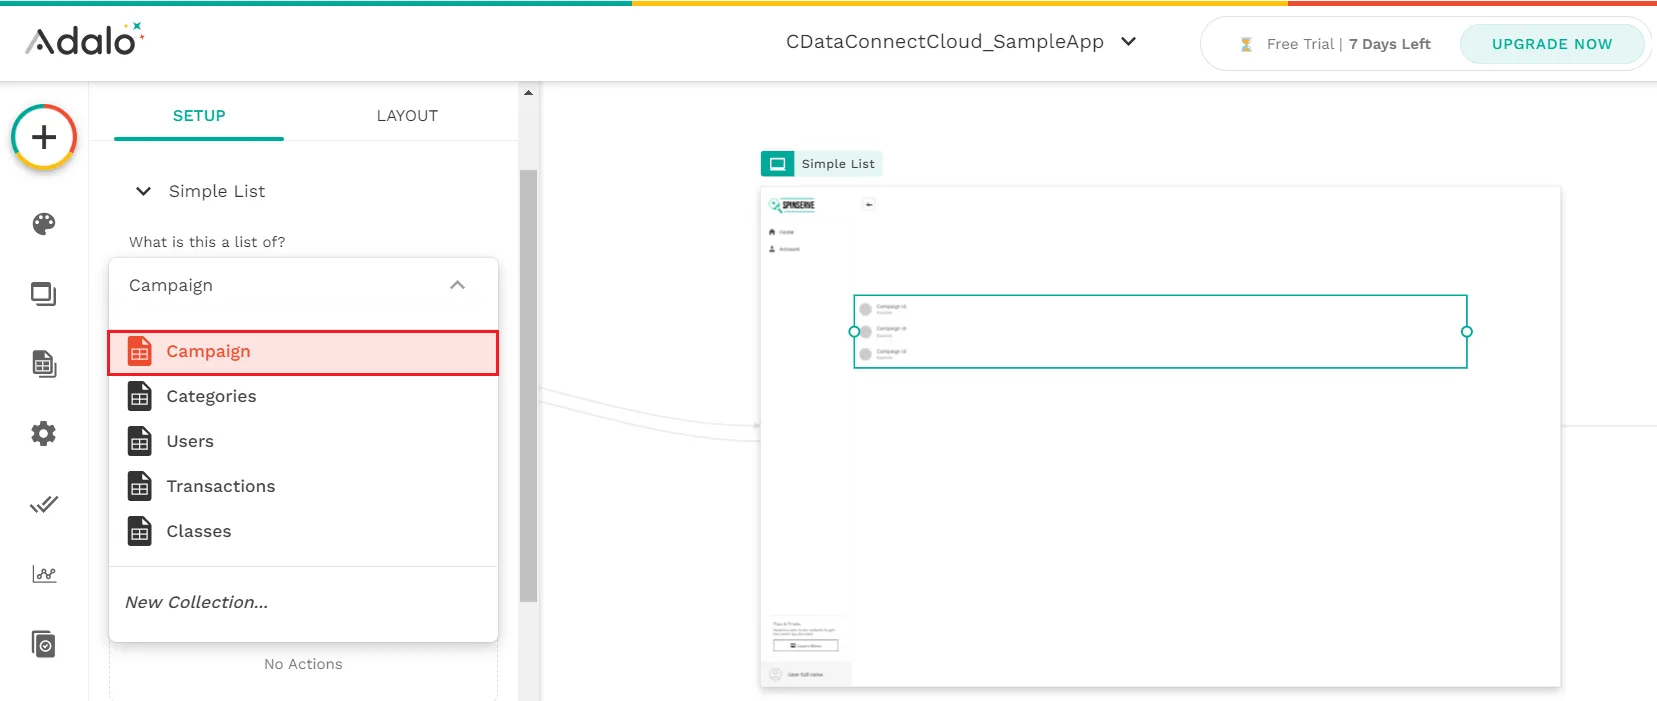
- Once the layout is complete as shown below, link the External Collections definition you created earlier to What is this a list of?
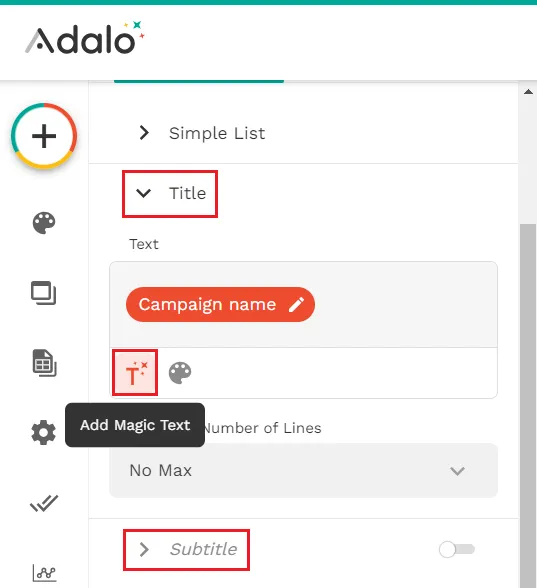
- Click on "Add Magic Text" button (as shown) to add the "Title" and "Subtitle" to the data items you want to obtain.
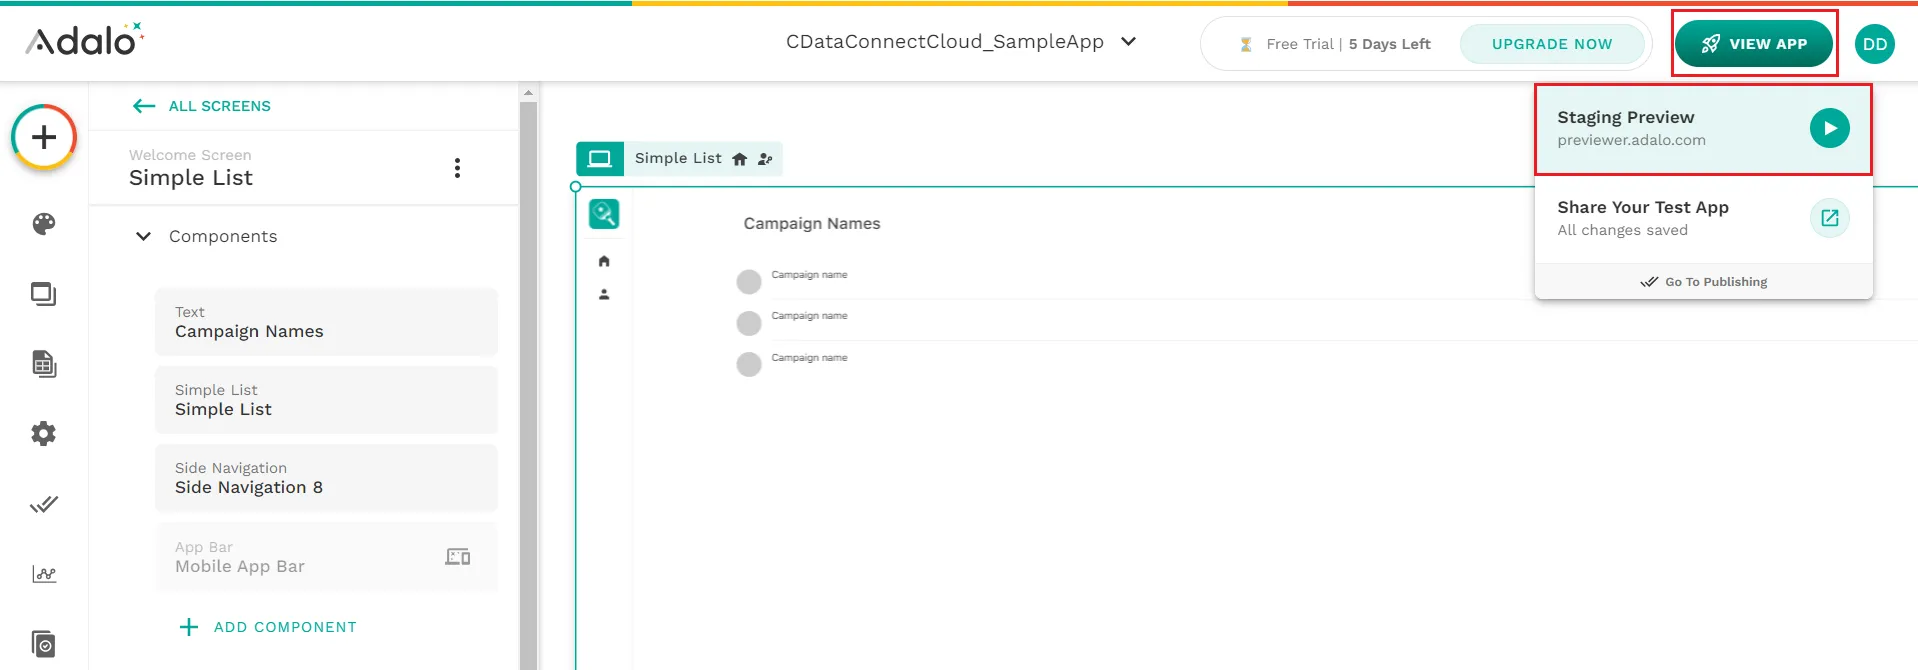
- Now, click on View App in the top right corner of the screen and select Staging Preview.
-
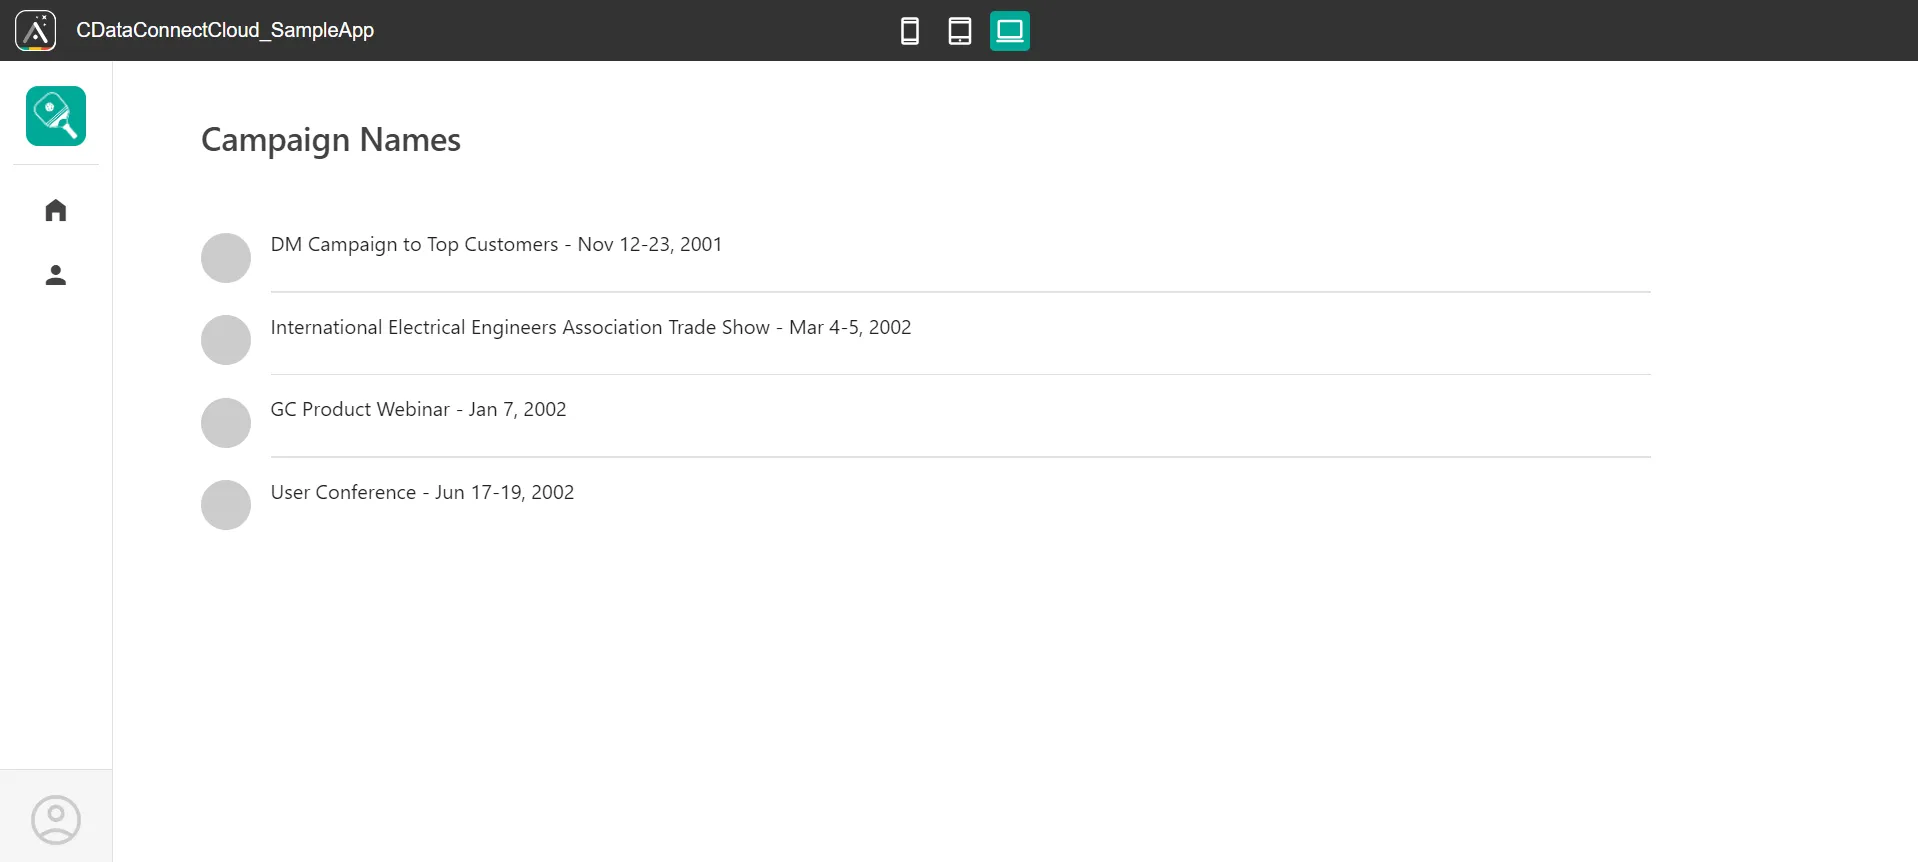
You can now view the PingOne data in the app created on Adalo.
Live connections to PingOne data from cloud applications
Adalo now allows you to connect to live PingOne data directly, allowing you to create more connections and apps without duplicating PingOne data.
To get real-time data access to over 100 SaaS, big data, and NoSQL sources directly from your cloud applications, visit CData Connect AI.