


Use Agno to Talk to Your PingOne Data via CData Connect AI
Agno is a developer-first Python framework for building AI agents that reason, plan, and take actions using tools. Agno emphasizes a clean, code-driven architecture where the agent runtime remains fully under developer control.
CData Connect AI provides a secure cloud-to-cloud interface for integrating hundreds of enterprise data sources with AI systems. Using Connect AI, live PingOne data data can be exposed through a remote MCP endpoint without replication.
In this guide, we build a production-ready Agno agent using the Agno Python SDK. The agent connects to CData Connect AI via MCP using streamable HTTP, dynamically discovers available tools, and invokes them to query live PingOne data.
Prerequisites
- Python 3.9+.
- A CData Connect AI account – Sign up or log in here.
- An active PingOne account with valid credentials.
- An LLM API key (for example, OpenAI).
Overview
Here is a high-level overview of the process:
- Connect: Configure a PingOne connection in CData Connect AI.
- Discover: Use MCP to dynamically retrieve tools exposed by CData Connect AI.
- Query: Wrap MCP tools as Agno functions and query live PingOne data.
Step 1: Configure PingOne in CData Connect AI
To enable Agno to query live PingOne data, first create a PingOne connection in CData Connect AI. This connection is exposed through the CData Remote MCP Server.
-
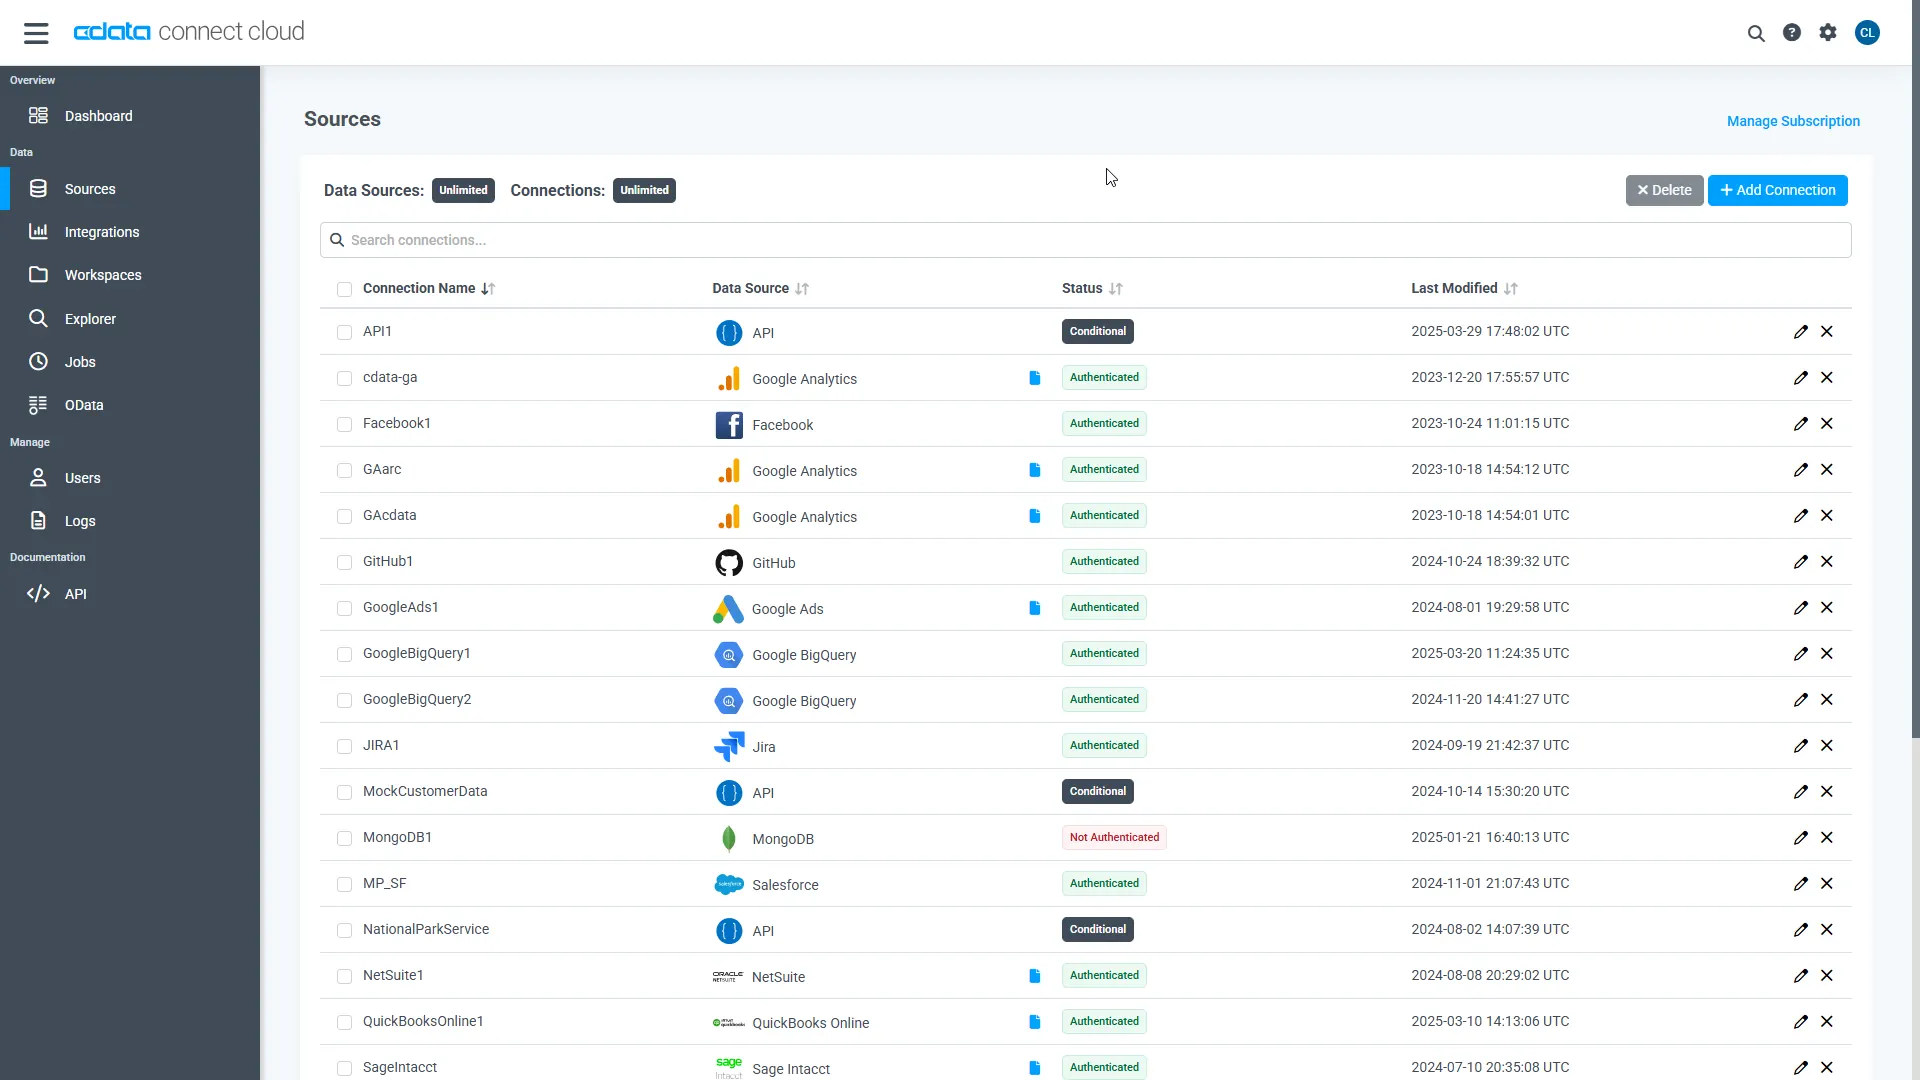
Log into Connect AI, click Sources, and then click
Add Connection.
-
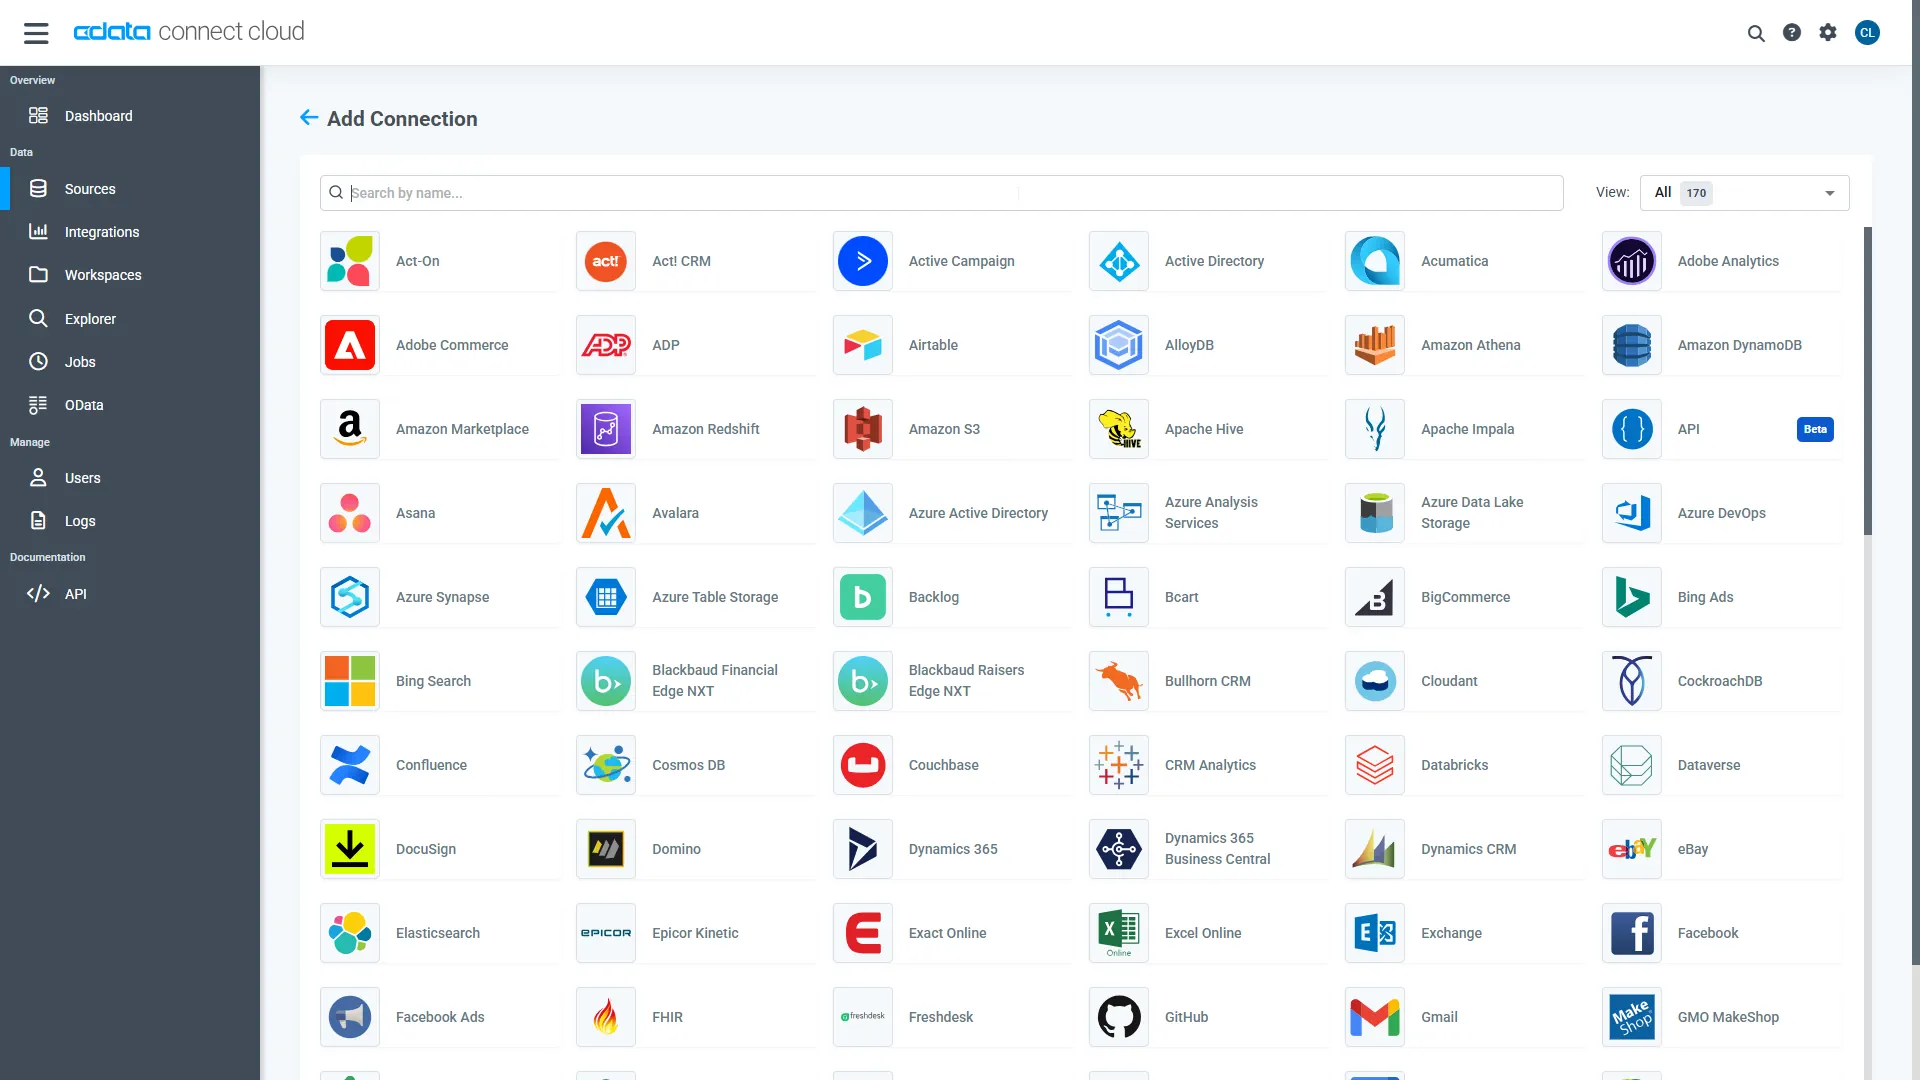
Select "PingOne" from the Add Connection panel.
-
Enter the required authentication properties.
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
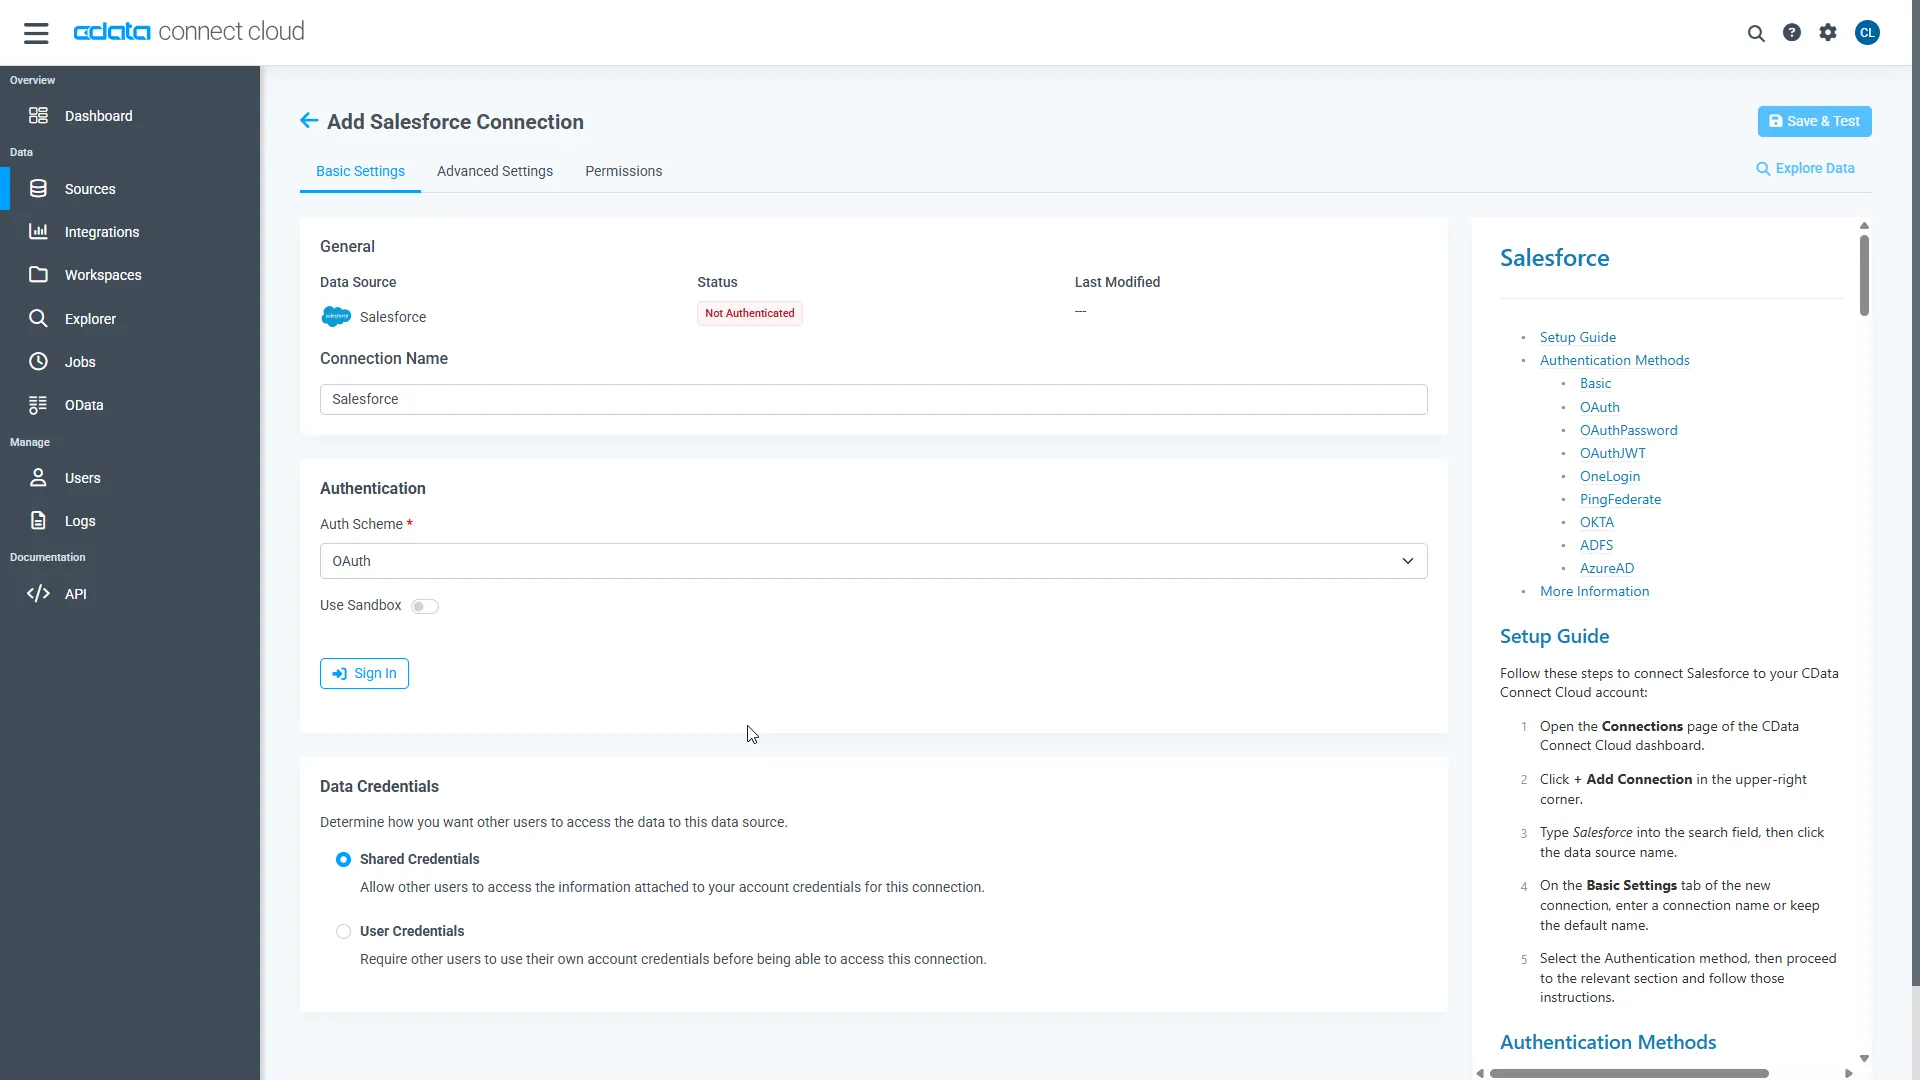 Click Create & Test.
-
Open the Permissions tab and configure user access.
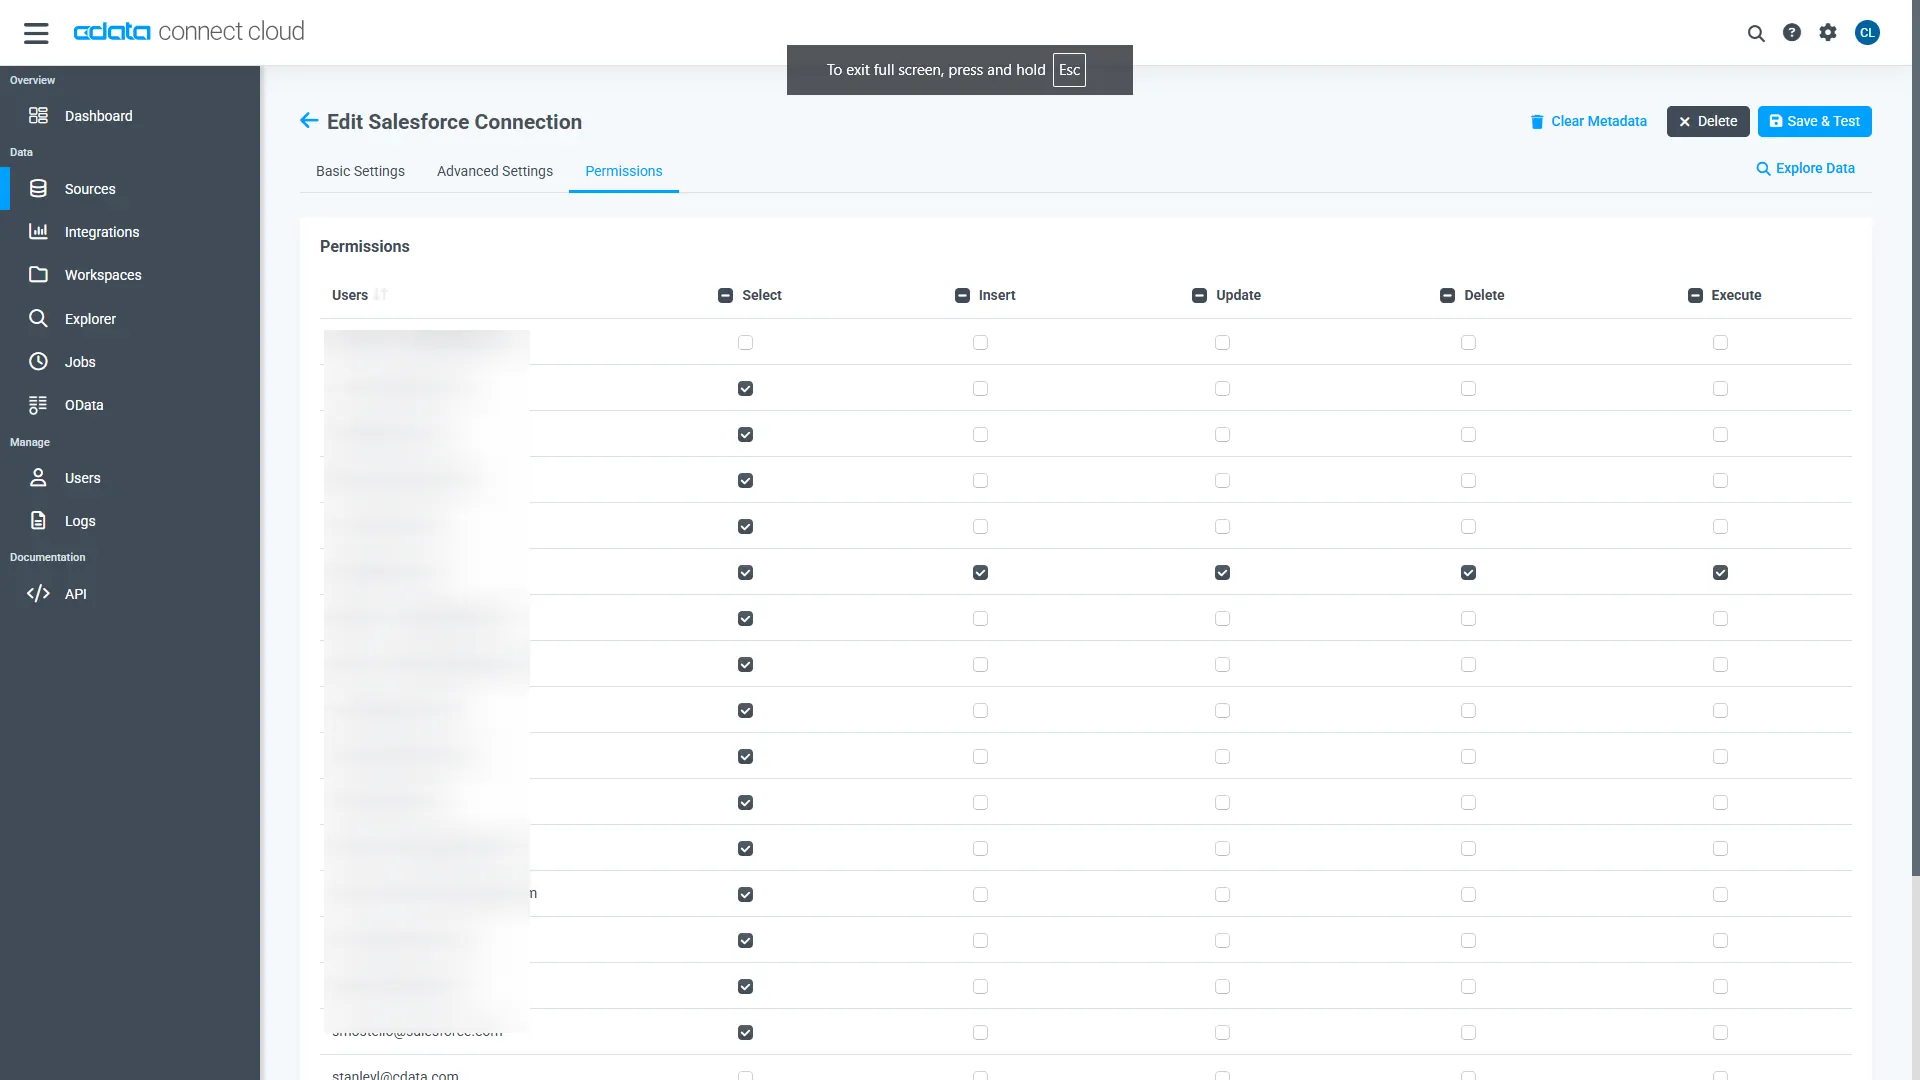
Add a Personal Access Token
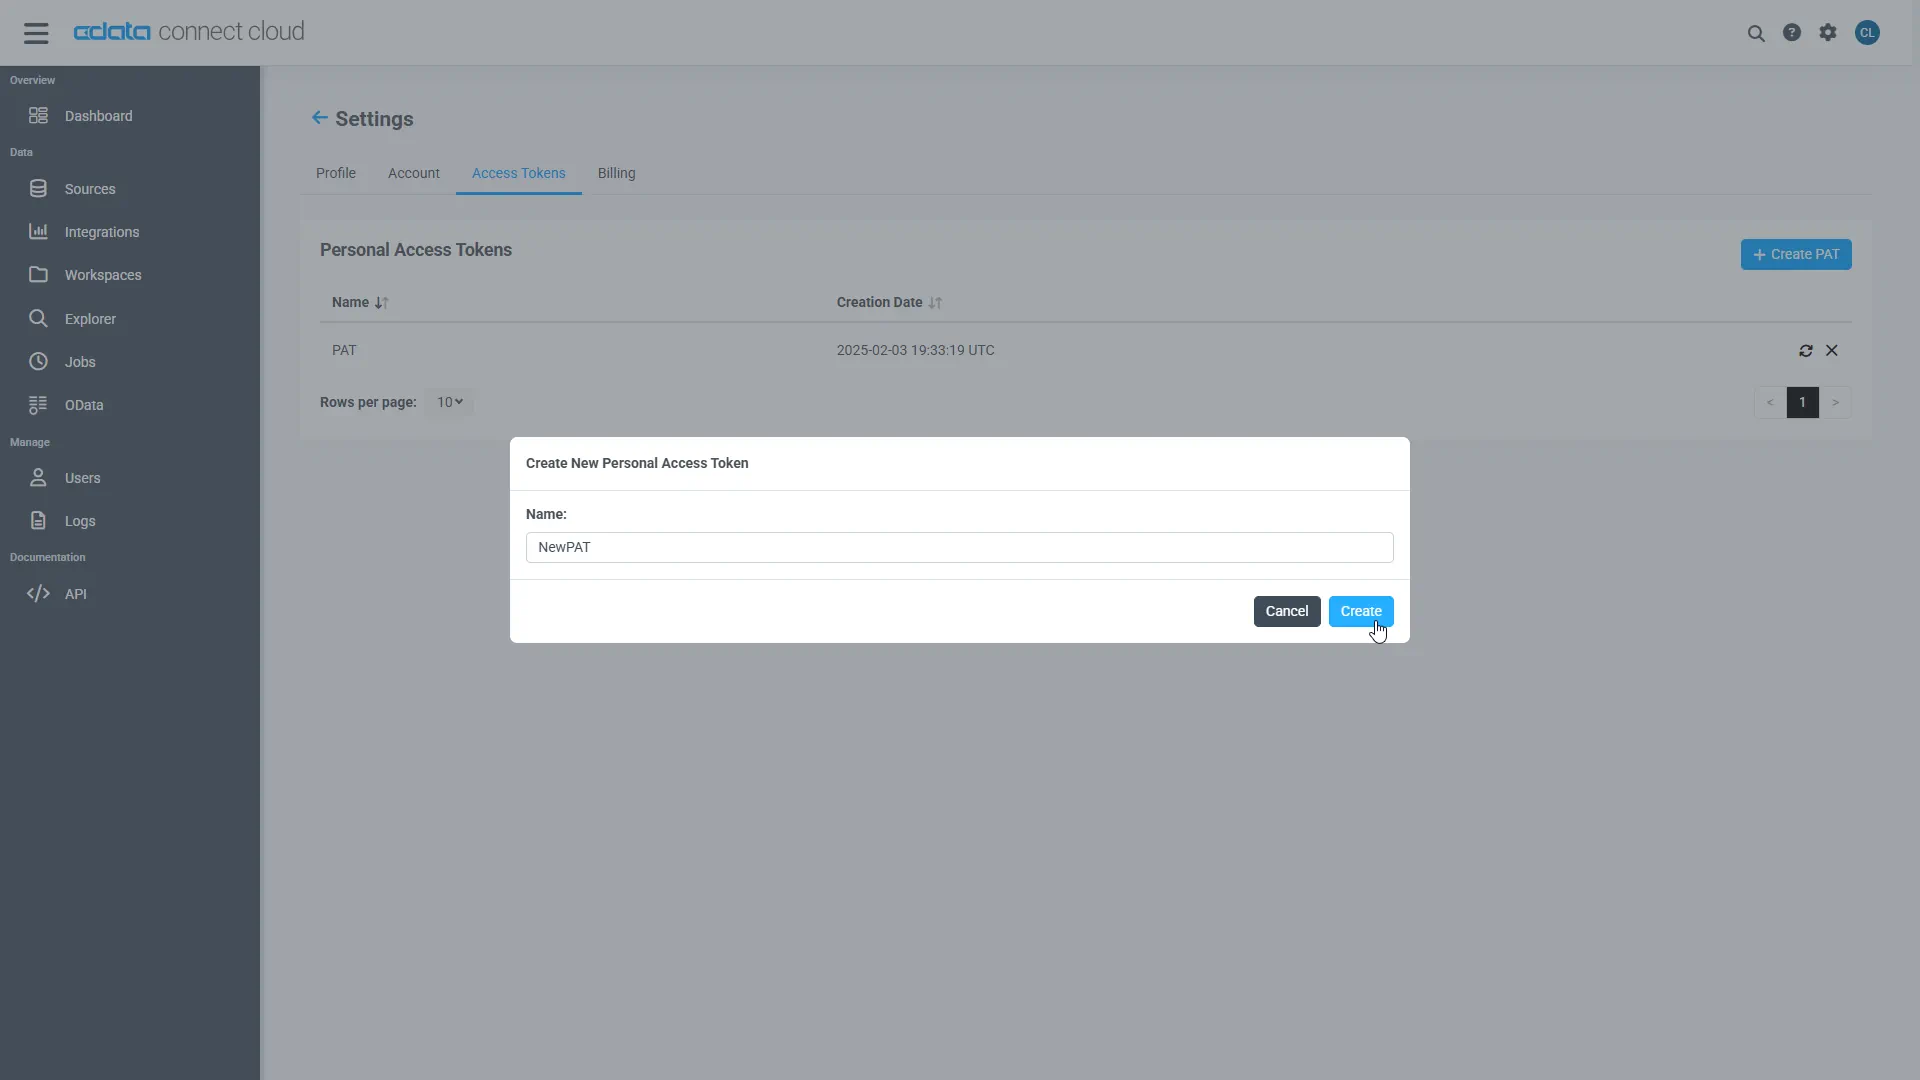
A Personal Access Token (PAT) authenticates MCP requests from Agno to CData Connect AI.
- Open Settings and navigate to Access Tokens.
- Click Create PAT.
-
Save the generated token securely.
Step 2: Install dependencies and configure environment variables
Install Agno and the MCP adapter dependencies. LangChain is included strictly for MCP tool compatibility.
pip install agno agno-mcp langchain-mcp-adapters
Configure environment variables:
export CDATA_MCP_URL="https://mcp.cloud.cdata.com/mcp"
export CDATA_MCP_AUTH="Base64EncodedCredentials"
export OPENAI_API_KEY="your-openai-key"
Where "Base64EncodedCredentials" is your Connect AI user email and your Personal Access Token joined by a colon (":") and Base64 Encoded: Base64([email protected]:MY_CONNECT_AI_PAT)
Step 3: Connect to CData Connect AI via MCP
Create an MCP client using streamable HTTP. This establishes a secure connection to CData Connect AI.
import os
from langchain_mcp_adapters.client import MultiServerMCPClient

mcp_client = MultiServerMCPClient(
  connections={
    "default": {
      "transport": "streamable_http",
      "url": os.environ["CDATA_MCP_URL"],
      "headers": {
        "Authorization": f"Basic {os.environ['CDATA_MCP_AUTH']}"
      }
    }
  }
)
Step 4: Discover MCP tools
CData Connect AI exposes operations as MCP tools. These are retrieved dynamically at runtime.
langchain_tools = await mcp_client.get_tools()
for tool in langchain_tools:
  print(tool.name)
Step 5: Convert MCP tools to Agno functions
Each MCP tool is wrapped as an Agno function so it can be used by the agent.
NOTE: Agno performs all reasoning, planning, and tool selection.LangChain is used only as a lightweight MCP compatibility layer to consume tools exposed by CData Connect AI.
from agno.tools import Function

def make_tool_caller(lc_tool):
  async def call_tool(**kwargs):
    return await lc_tool.ainvoke(kwargs)
  return call_tool
Step 6: Create an Agno agent and query live PingOne data
Agno performs all reasoning, planning, and tool invocation. LangChain plays no role beyond MCP compatibility.
from agno.agent import Agent
from agno.models.openai import OpenAIChat

agent = Agent(
  model=OpenAIChat(
    id="gpt-4o",
    temperature=0.2,
    api_key=os.environ["OPENAI_API_KEY"]
  ),
  tools=agno_tools,
  markdown=True
)

await agent.aprint_response(
  "Show me the top 5 records from the available data source"
)

if __name__ == "__main__":
    asyncio.run(main())
The results below show an Agno agent invoking MCP tools through CData Connect AI and returning live PingOne data data.
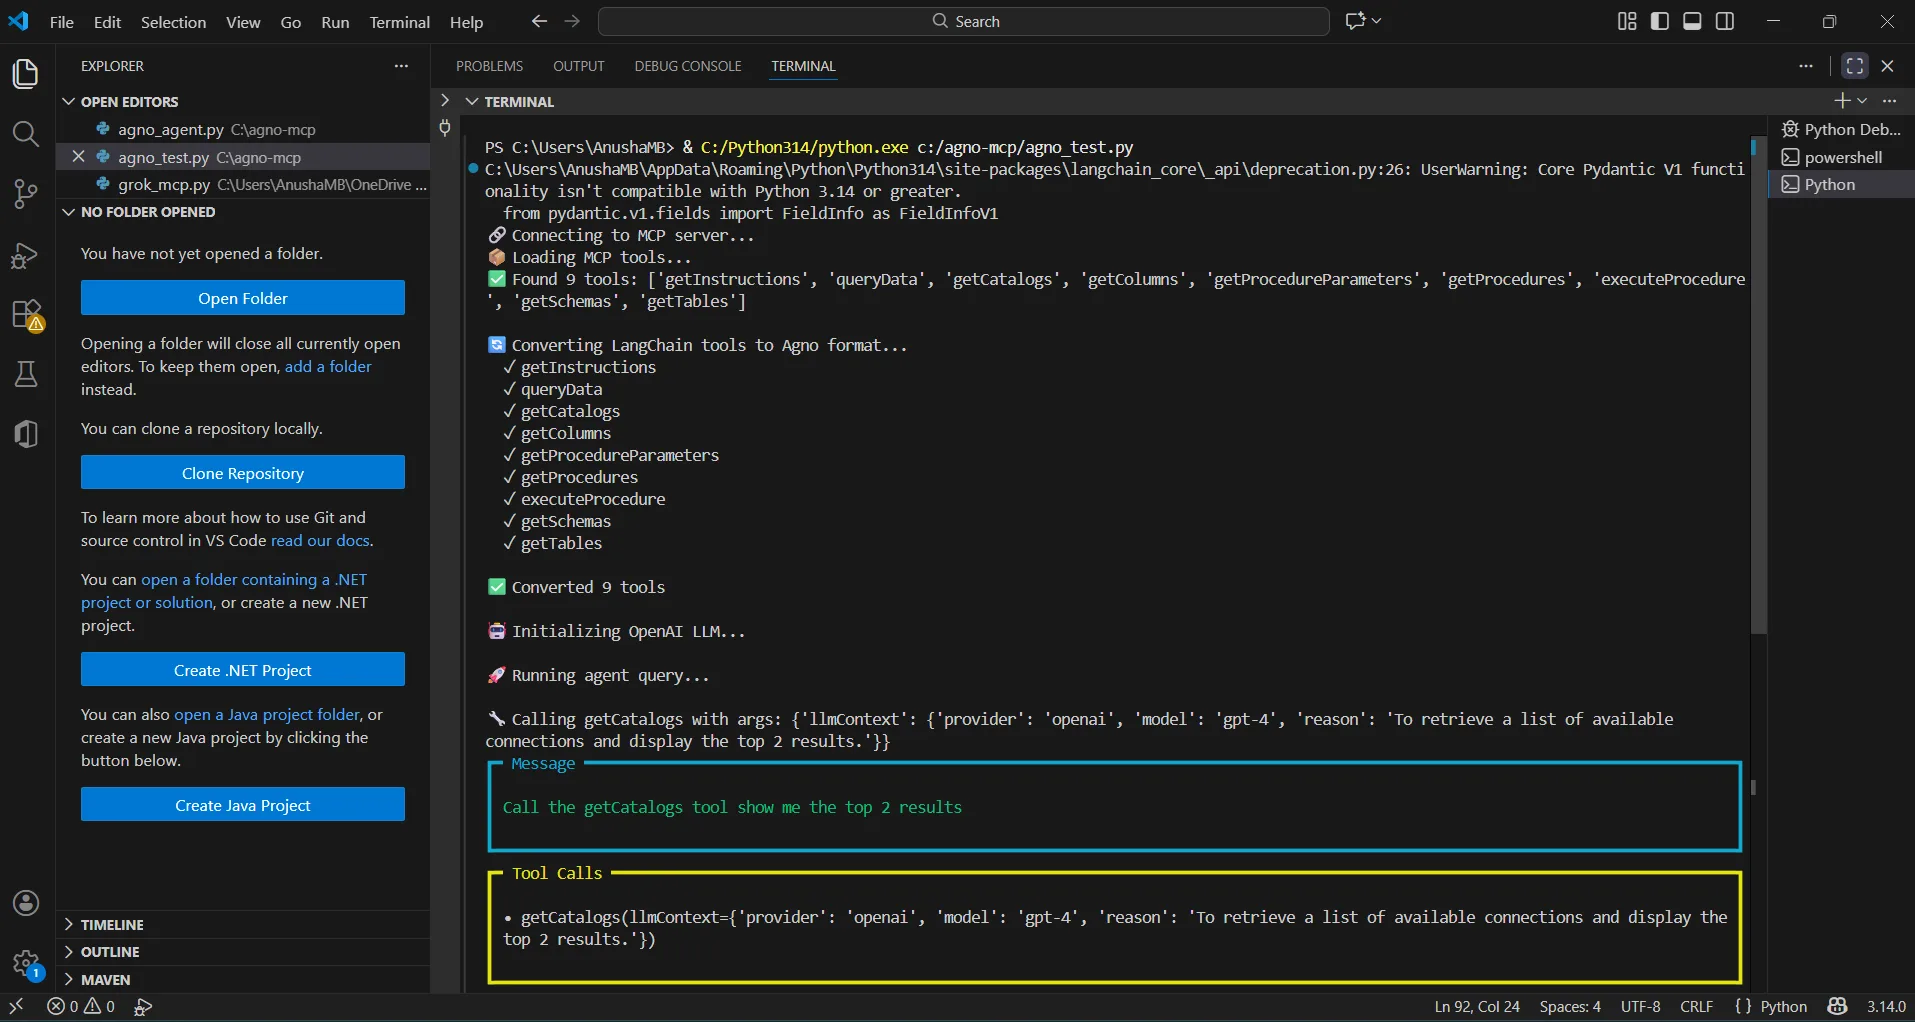
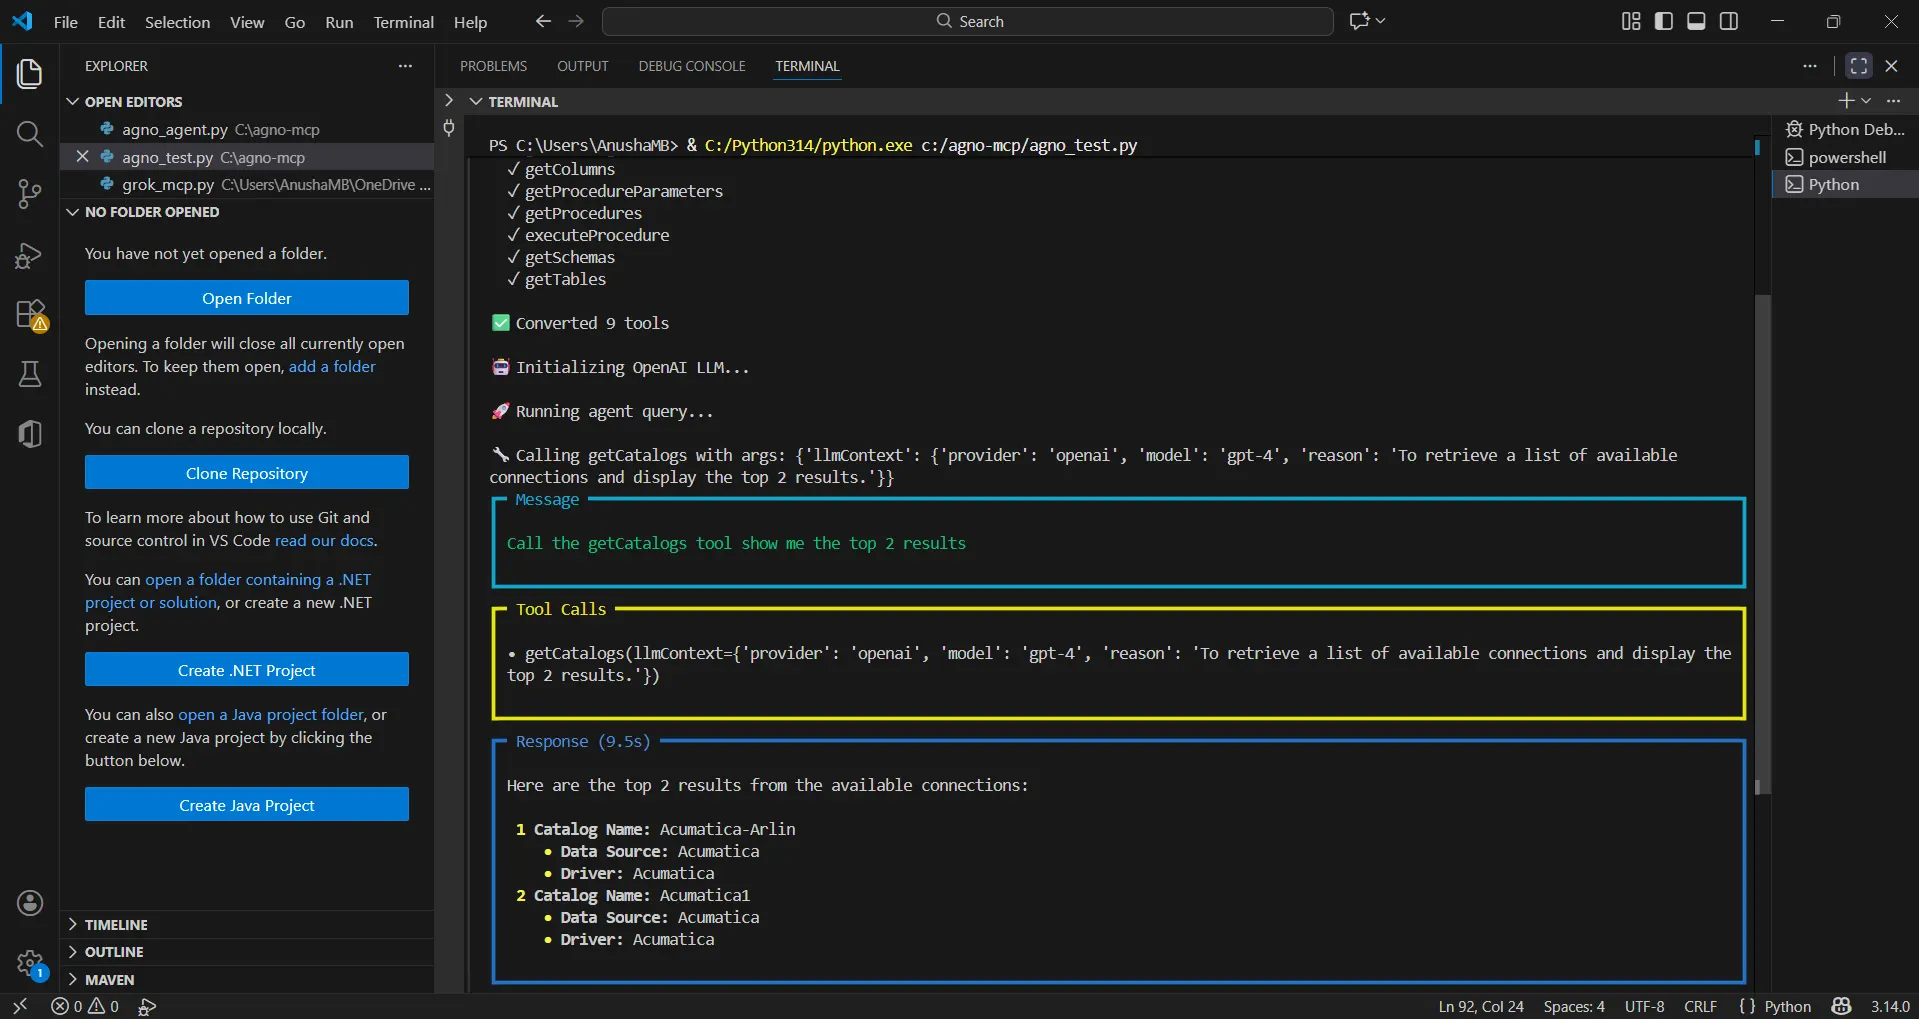
You can now query live PingOne data using natural language through your Agno agent.
Get CData Connect AI
To get live data access to hundreds of SaaS, Big Data, and NoSQL sources directly from your cloud applications, try CData Connect AI today!