


How to Connect to Live PingOne Data from Google ADK Agents (via CData Connect AI)
Google ADK (Agent Development Kit) is a powerful, model-agnostic framework for building AI agents that can interact with various data sources and services. When combined with CData Connect AI Remote MCP, you can leverage Google ADK to build intelligent agents that interact with your PingOne data in real-time through natural language queries. This article outlines the process of connecting to PingOne using Connect AI Remote MCP and configuring a Google ADK agent to interact with your PingOne data through ADK Web.
CData Connect AI offers a dedicated cloud-to-cloud interface for connecting to PingOne data. The CData Connect AI Remote MCP Server enables secure communication between Google ADK agents and PingOne. This allows your agents to read from and take actions on your PingOne data, all without the need for data replication to a natively supported database. With its inherent optimized data processing capabilities, CData Connect AI efficiently channels all supported SQL operations, including filters and JOINs, directly to PingOne. This leverages server-side processing to swiftly deliver the requested PingOne data.
In this article, we show how to configure a Google ADK agent to conversationally explore (or Vibe Query) your data using natural language. With Connect AI you can build agents with access to live PingOne data, plus hundreds of other sources.
Step 1: Configure PingOne Connectivity for Google ADK
Connectivity to PingOne from Google ADK agents is made possible through CData Connect AI Remote MCP. To interact with PingOne data from your ADK agent, we start by creating and configuring a PingOne connection in CData Connect AI.
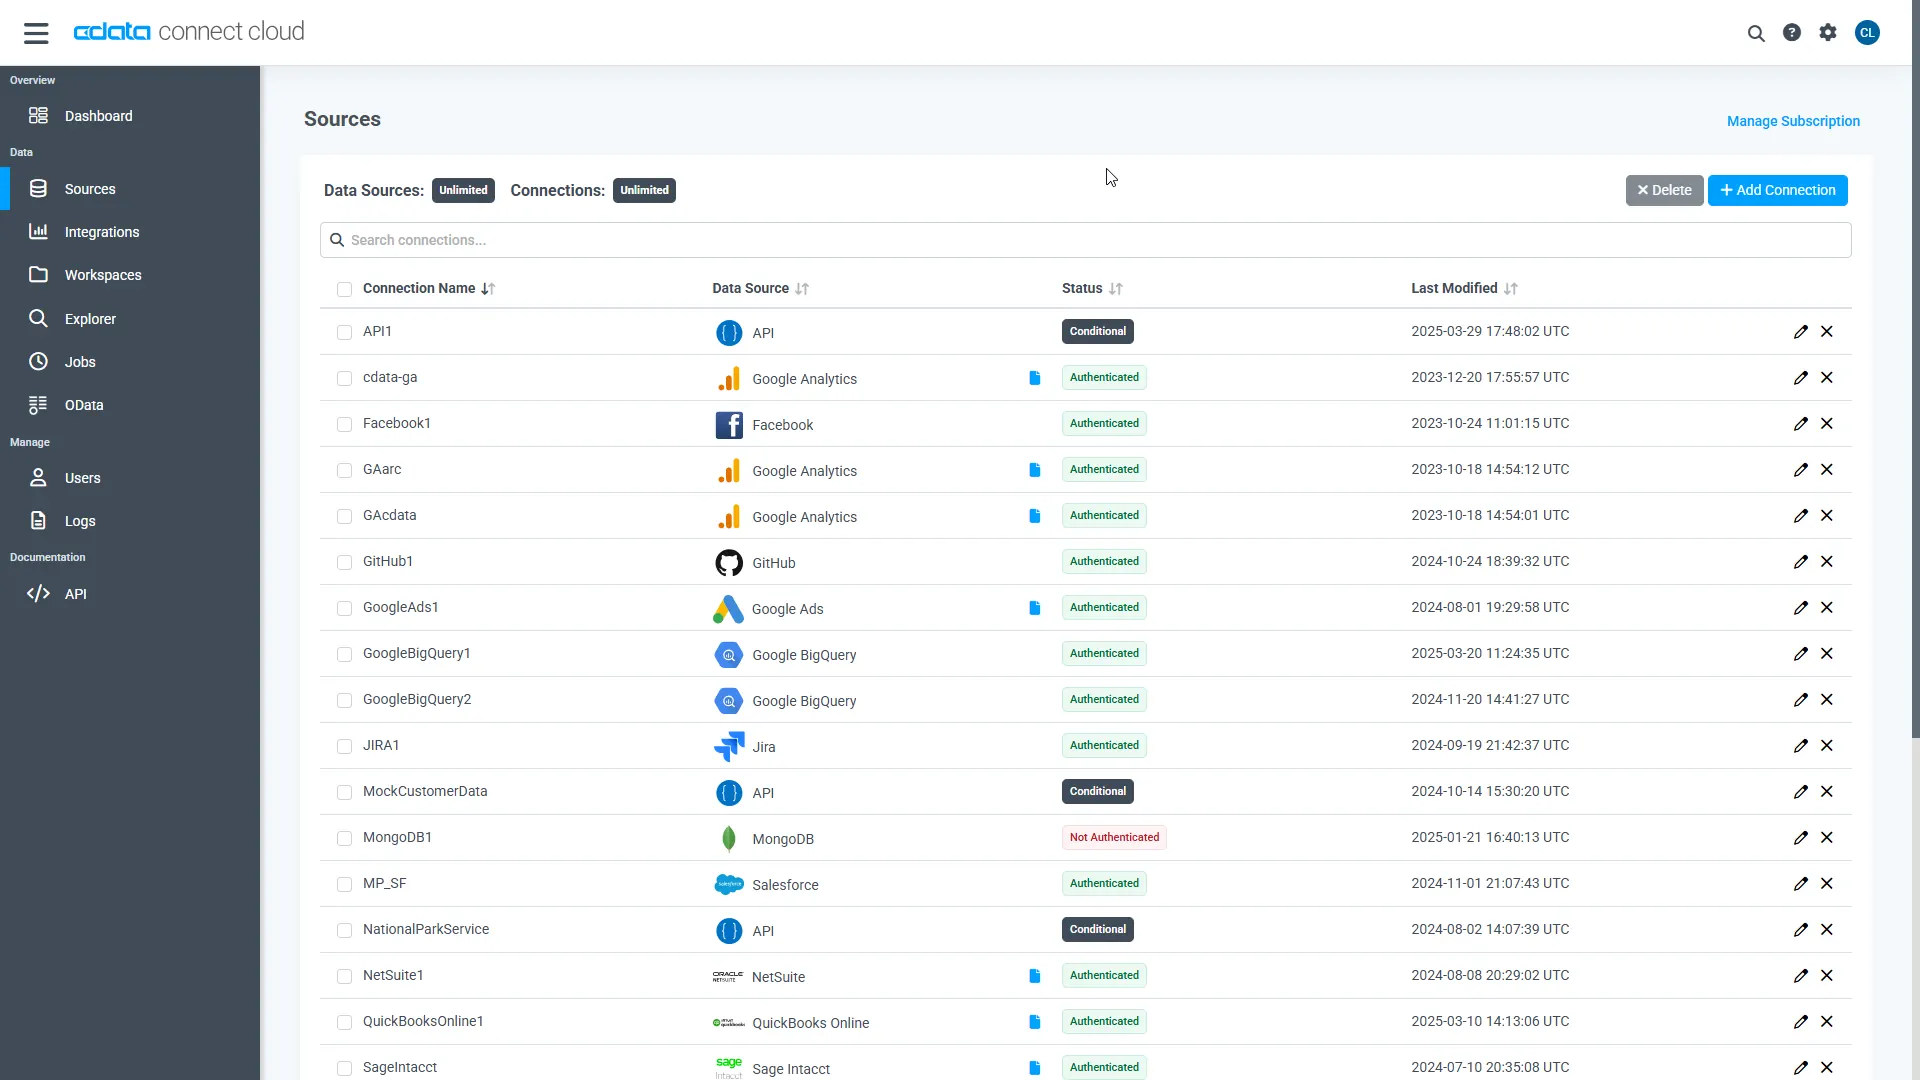
- Log into Connect AI, click Sources, and then click Add Connection
- Select "PingOne" from the Add Connection panel
-
Enter the necessary authentication properties to connect to PingOne.
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
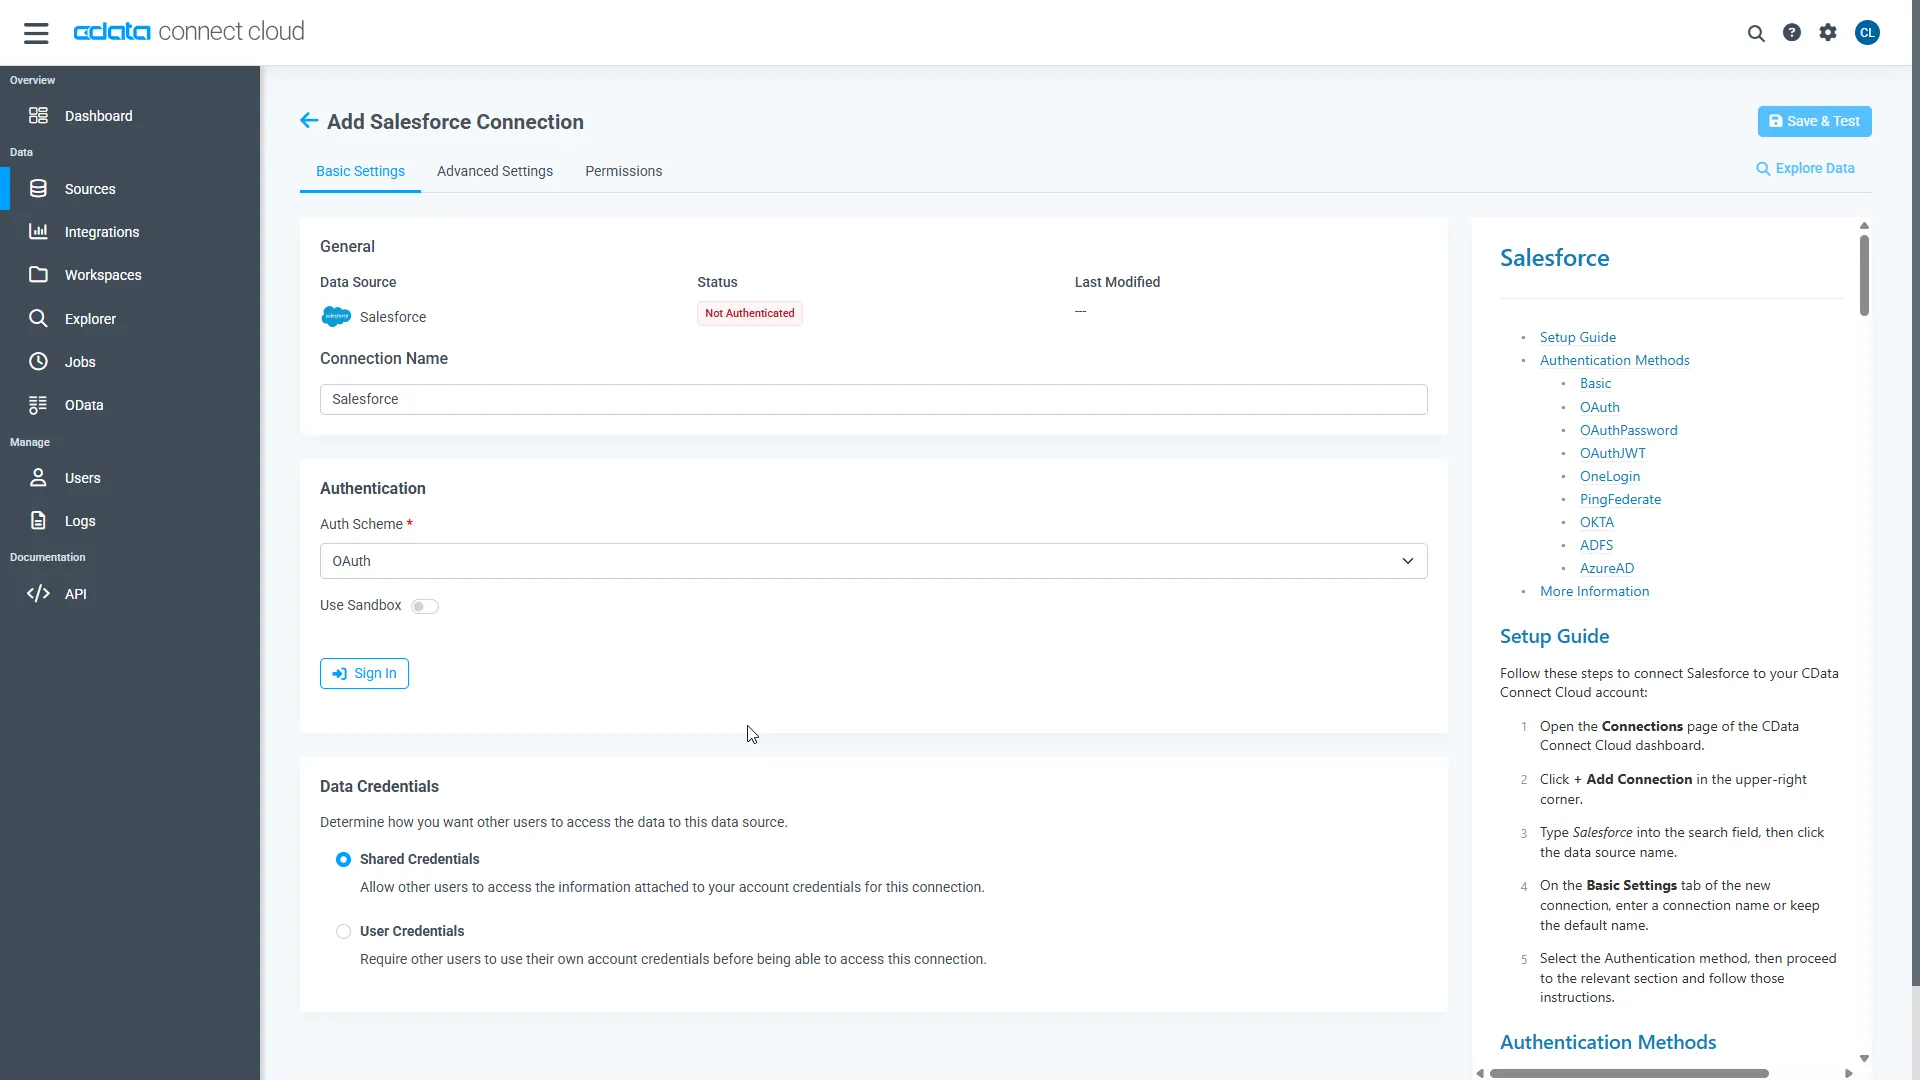
- Click Save & Test
-
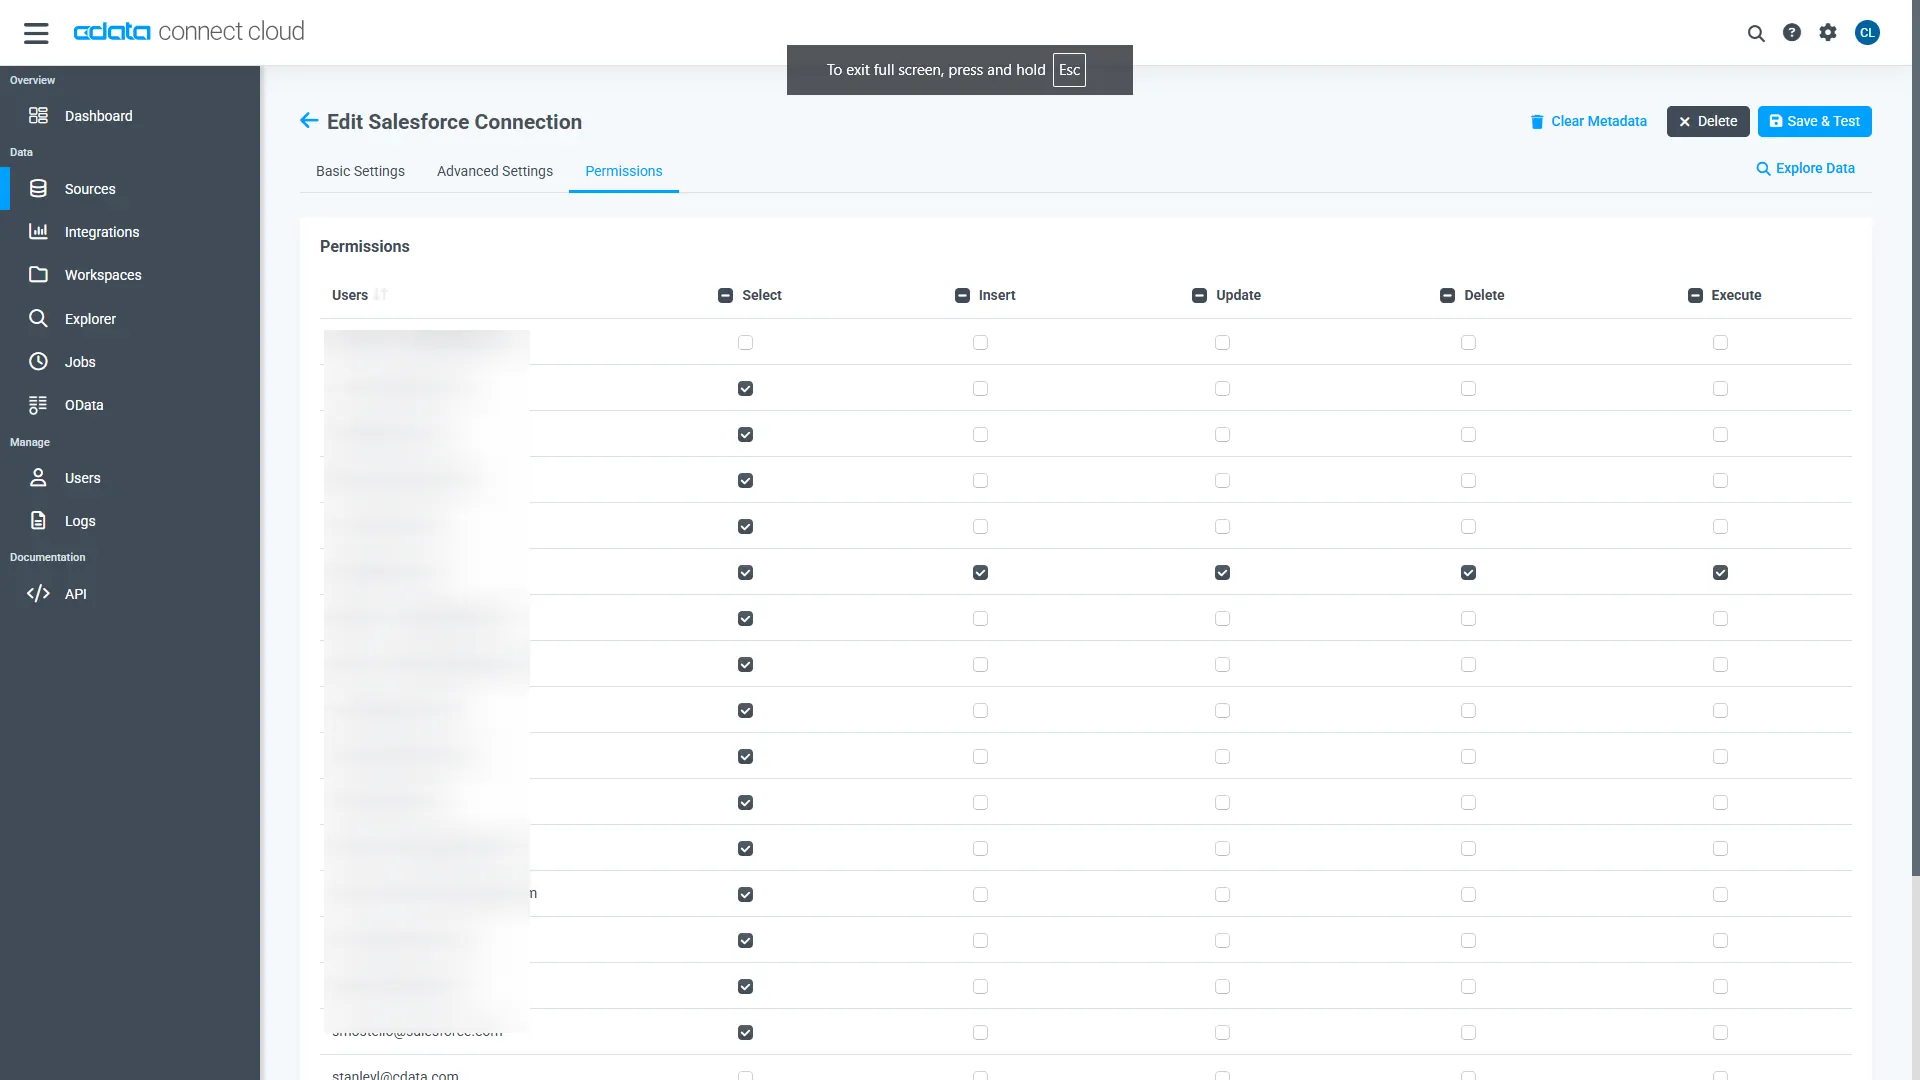
Navigate to the Permissions tab in the Add PingOne Connection page and update the User-based permissions.
Add a Personal Access Token
A Personal Access Token (PAT) is used to authenticate the connection to Connect AI from your Google ADK agent. It is best practice to create a separate PAT for each service to maintain granularity of access.
- Click on the Gear icon () at the top right of the Connect AI app to open the settings page.
- On the Settings page, go to the Access Tokens section and click Create PAT.
-
Give the PAT a name and click Create.
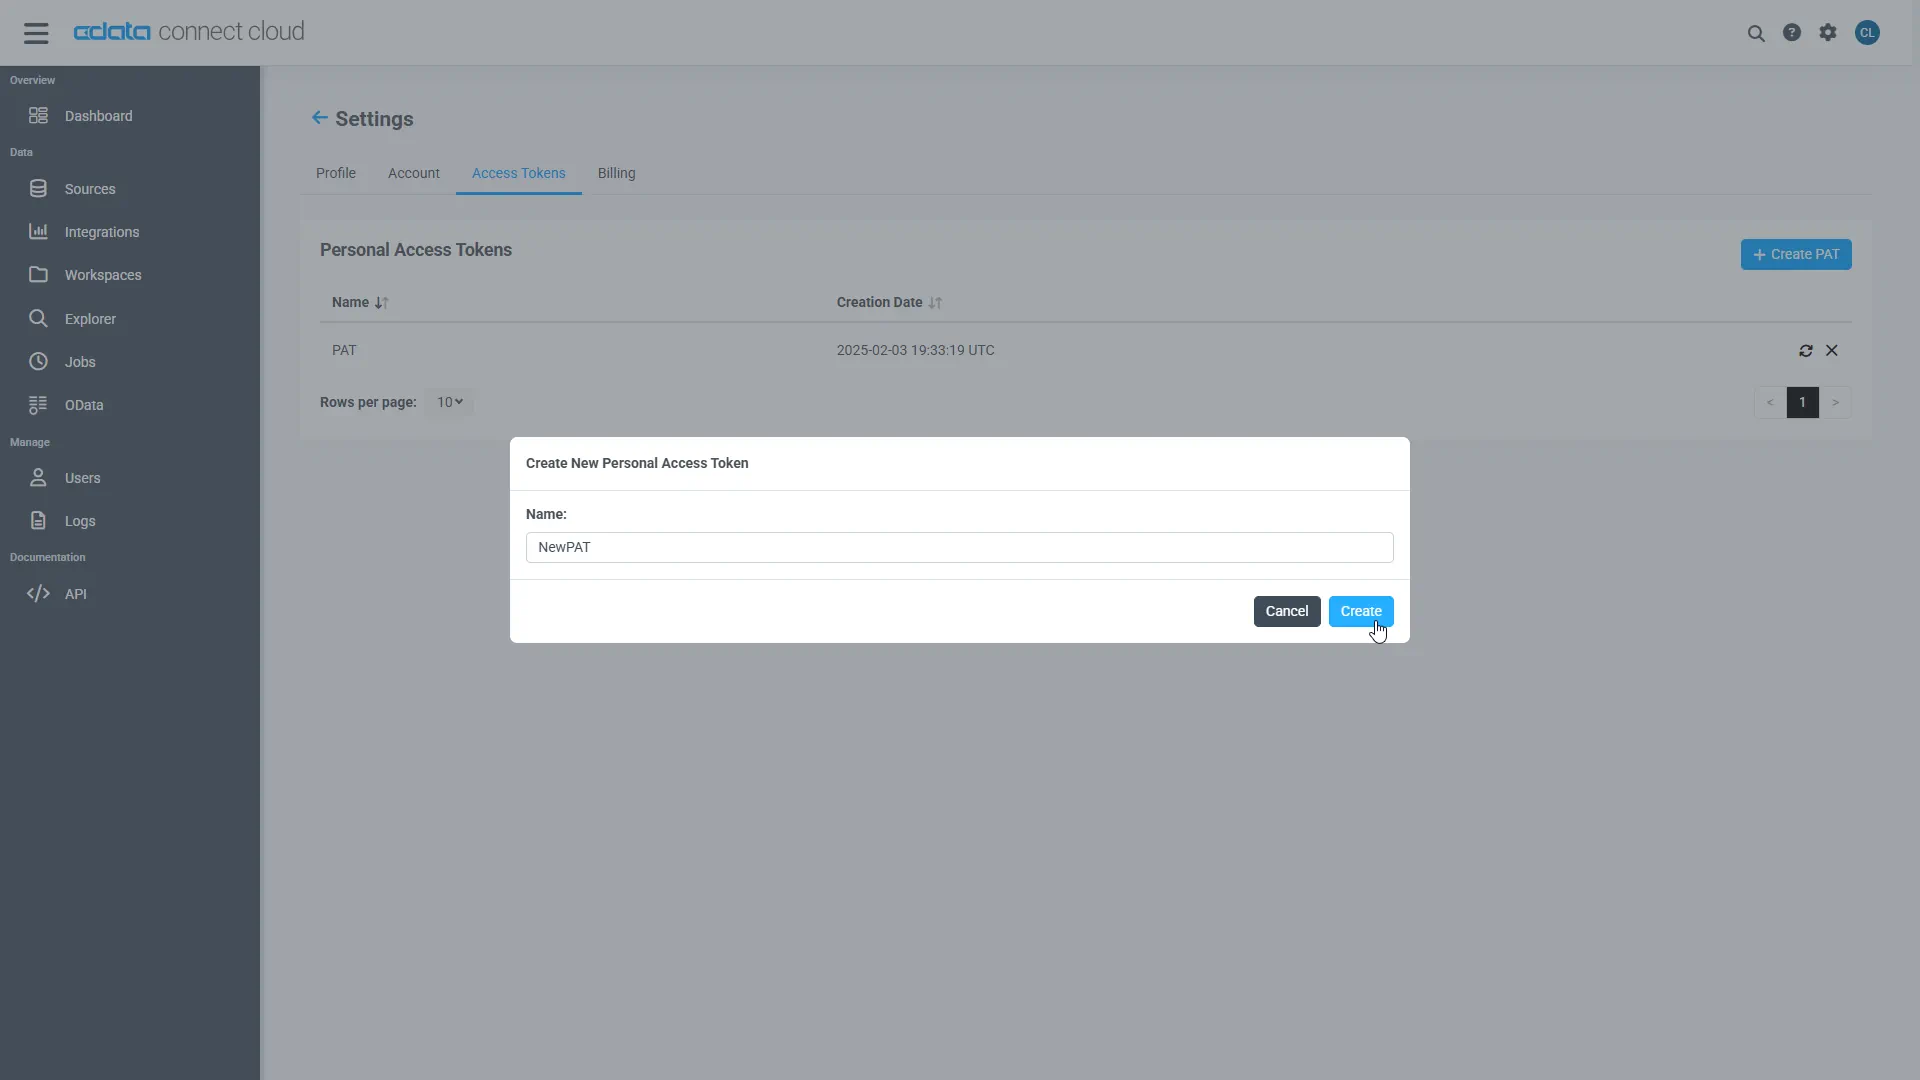
- The personal access token is only visible at creation, so be sure to copy it and store it securely for future use.
With the connection configured and a PAT generated, we are ready to connect to PingOne data from your Google ADK agent.
Step 2: Configure Your Google ADK Agent for CData Connect AI
Follow these steps to configure your Google ADK agent to connect to CData Connect AI. You can use our pre-built agent as a starting point, available at https://github.com/CDataSoftware/adk-mcp-client, or follow the instructions below to create your own.
-
Ensure you have the Google ADK Python SDK installed. If not, install it using pip:
pip install google-genkit google-adk - Create or update your agent's configuration file (typically agent.py) to include the CData Connect AI MCP connection. You'll need to configure the MCP toolset with your Connect AI credentials.
-
Set up your environment variables or configuration for the MCP server connection. Create a .env file in your project root with the following variables:
Replace YOUR_EMAIL with your Connect AI email address and YOUR_PAT with the Personal Access Token created in Step 1.MCP_SERVER_URL=https://mcp.cloud.cdata.com/mcp MCP_USERNAME=YOUR_EMAIL MCP_PASSWORD=YOUR_PAT -
Configure your agent.py file to use the CData Connect AI MCP Server. Here's an example configuration:
import os import base64 from google.adk.agents import LlmAgent from google.adk.tools.mcp_tool.mcp_toolset import MCPToolset from google.adk.tools.mcp_tool.mcp_session_manager import StreamableHTTPConnectionParams from dotenv import load_dotenv # Load environment variables load_dotenv() # Get configuration from environment MCP_SERVER_URL = os.getenv('MCP_SERVER_URL', 'https://mcp.cloud.cdata.com/mcp') MCP_USERNAME = os.getenv('MCP_USERNAME', '') MCP_PASSWORD = os.getenv('MCP_PASSWORD', '') # Create auth header for MCP server auth_header = {} if MCP_USERNAME and MCP_PASSWORD: credentials = f"{MCP_USERNAME}:{MCP_PASSWORD}" auth_header = {"Authorization": f"Basic {base64.b64encode(credentials.encode()).decode()}"} # Define your agent with CData MCP tools root_agent = LlmAgent( model='gemini-2.0-flash-exp', # You can use any supported model name='data_query_assistant', instruction="""You are a data query assistant with access to PingOne data through CData Connect AI. You can help users explore and query their PingOne data in real-time. Use the available MCP tools to: - List available databases and schemas - Explore table structures - Execute SQL queries - Provide insights about the data Always explain what you're doing and format results clearly.""", tools=[ MCPToolset( connection_params=StreamableHTTPConnectionParams( url=MCP_SERVER_URL, headers=auth_header ) ) ], ) -
Run your agent with ADK Web. From your project directory, execute:
adk web --port 5000 .Note: If you installed ADK with pip install --user, the adk command may not be in your PATH. You can either:
- Use the full path: ~/Library/Python/3.x/bin/adk (on macOS)
- Add to PATH: export PATH="$HOME/Library/Python/3.x/bin:$PATH"
- Use a virtual environment where the PATH is automatically configured
- Open the ADK Web interface in your browser (typically http://localhost:5000).
- Select your agent from the dropdown menu (it will be named based on the name parameter in your agent configuration).
- Start interacting with your PingOne data through natural language queries. Your agent now has access to your PingOne data through the CData Connect AI MCP Server.
Step 3: Build Intelligent Agents with Live PingOne Data Access
With your Google ADK agent configured and connected to CData Connect AI, you can now build sophisticated agents that interact with your PingOne data using natural language. The MCP integration provides your agents with powerful data access capabilities.
Available MCP Tools for Your Agent
Your Google ADK agent has access to the following CData Connect AI MCP tools:
- queryData: Execute SQL queries against connected data sources and retrieve results
- getCatalogs: Retrieve a list of available connections from CData Connect AI
- getSchemas: Retrieve database schemas for a specific catalog
- getTables: Retrieve database tables for a specific catalog and schema
- getColumns: Retrieve column metadata for a specific table
- getProcedures: Retrieve stored procedures for a specific catalog and schema
- getProcedureParameters: Retrieve parameter metadata for stored procedures
- executeProcedure: Execute stored procedures with parameters
Example Use Cases
Here are some examples of what your Google ADK agents can do with live PingOne data access:
- Data Analysis Agent: Build an agent that analyzes trends, patterns, and anomalies in your PingOne data
- Report Generation Agent: Create agents that generate custom reports based on natural language requests
- Data Quality Agent: Develop agents that monitor and validate data quality in real-time
- Business Intelligence Agent: Build agents that answer complex business questions by querying multiple data sources
- Automated Workflow Agent: Create agents that trigger actions based on data conditions in PingOne
Testing Your Agent
Once deployed to ADK Web, you can interact with your agent through natural language queries. For example:
- "Show me all customers from the last 30 days"
- "What are the top performing products this quarter?"
- "Analyze sales trends and identify anomalies"
- "Generate a summary report of active projects"
- "Find all records that match specific criteria"
Your Google ADK agent will automatically translate these natural language queries into appropriate SQL queries and execute them against your PingOne data through the CData Connect AI MCP Server, providing real-time insights without requiring users to write complex SQL or understand the underlying data structure.
Get CData Connect AI
To get live data access to hundreds of SaaS, Big Data, and NoSQL sources directly from your Google ADK agents and cloud applications, try CData Connect AI today!