


Use Grok to Talk to Your PingOne Data via CData Connect AI
Grok AI is a large language model developed by xAI for real-time reasoning, tool invocation, and agentic workflows. It enables developers to build AI agents that can reason over live data, discover tools dynamically, and take intelligent actions.
CData Connect AI provides a secure cloud-to-cloud interface for integrating hundreds of enterprise data sources with Grok AI. Using Connect AI, live PingOne data is exposed through a remote MCP endpoint without replication, allowing Grok AI agents to securely query and analyze governed enterprise data in real time.
Step 1: Configure PingOne in CData Connect AI
To enable Grok to query live PingOne data, first create a PingOne connection in CData Connect AI. This connection is exposed through the CData Remote MCP Server.
-
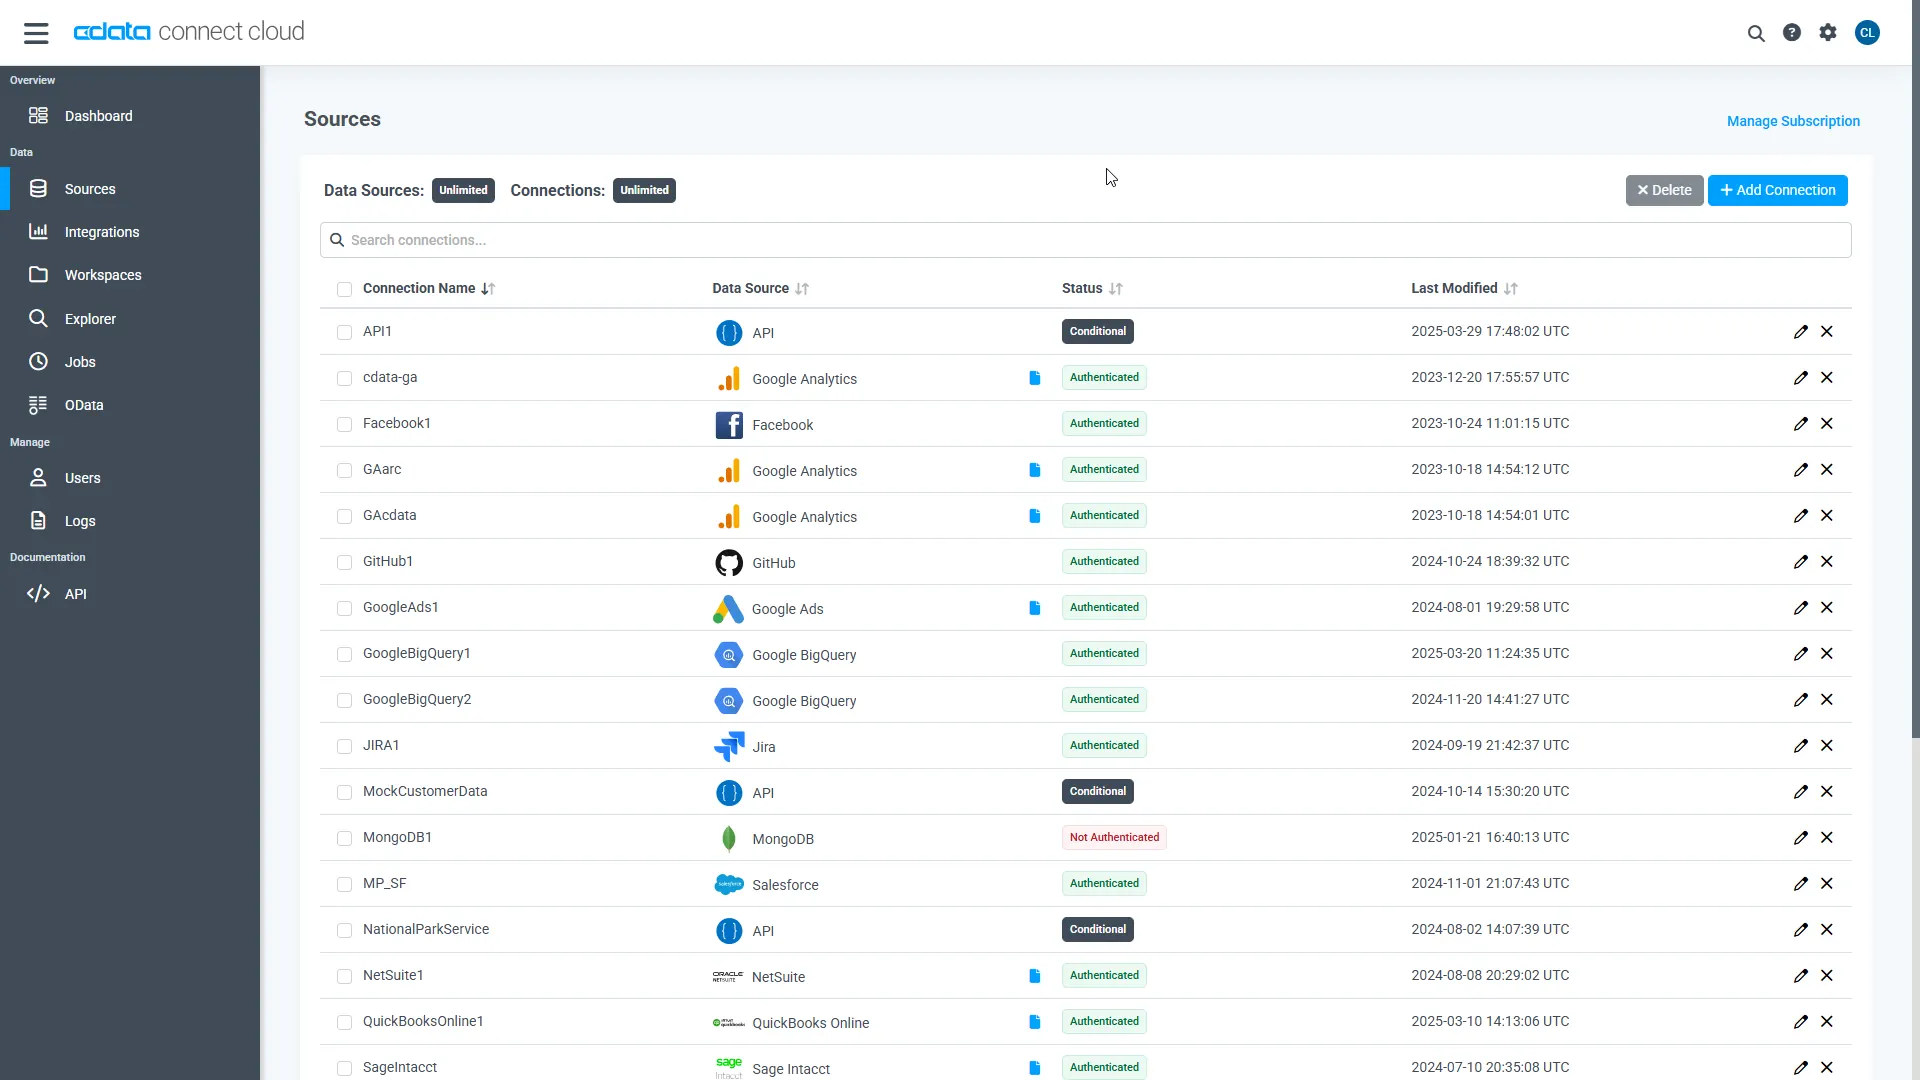
Log into Connect AI, click Sources, and then click Add Connection.
-
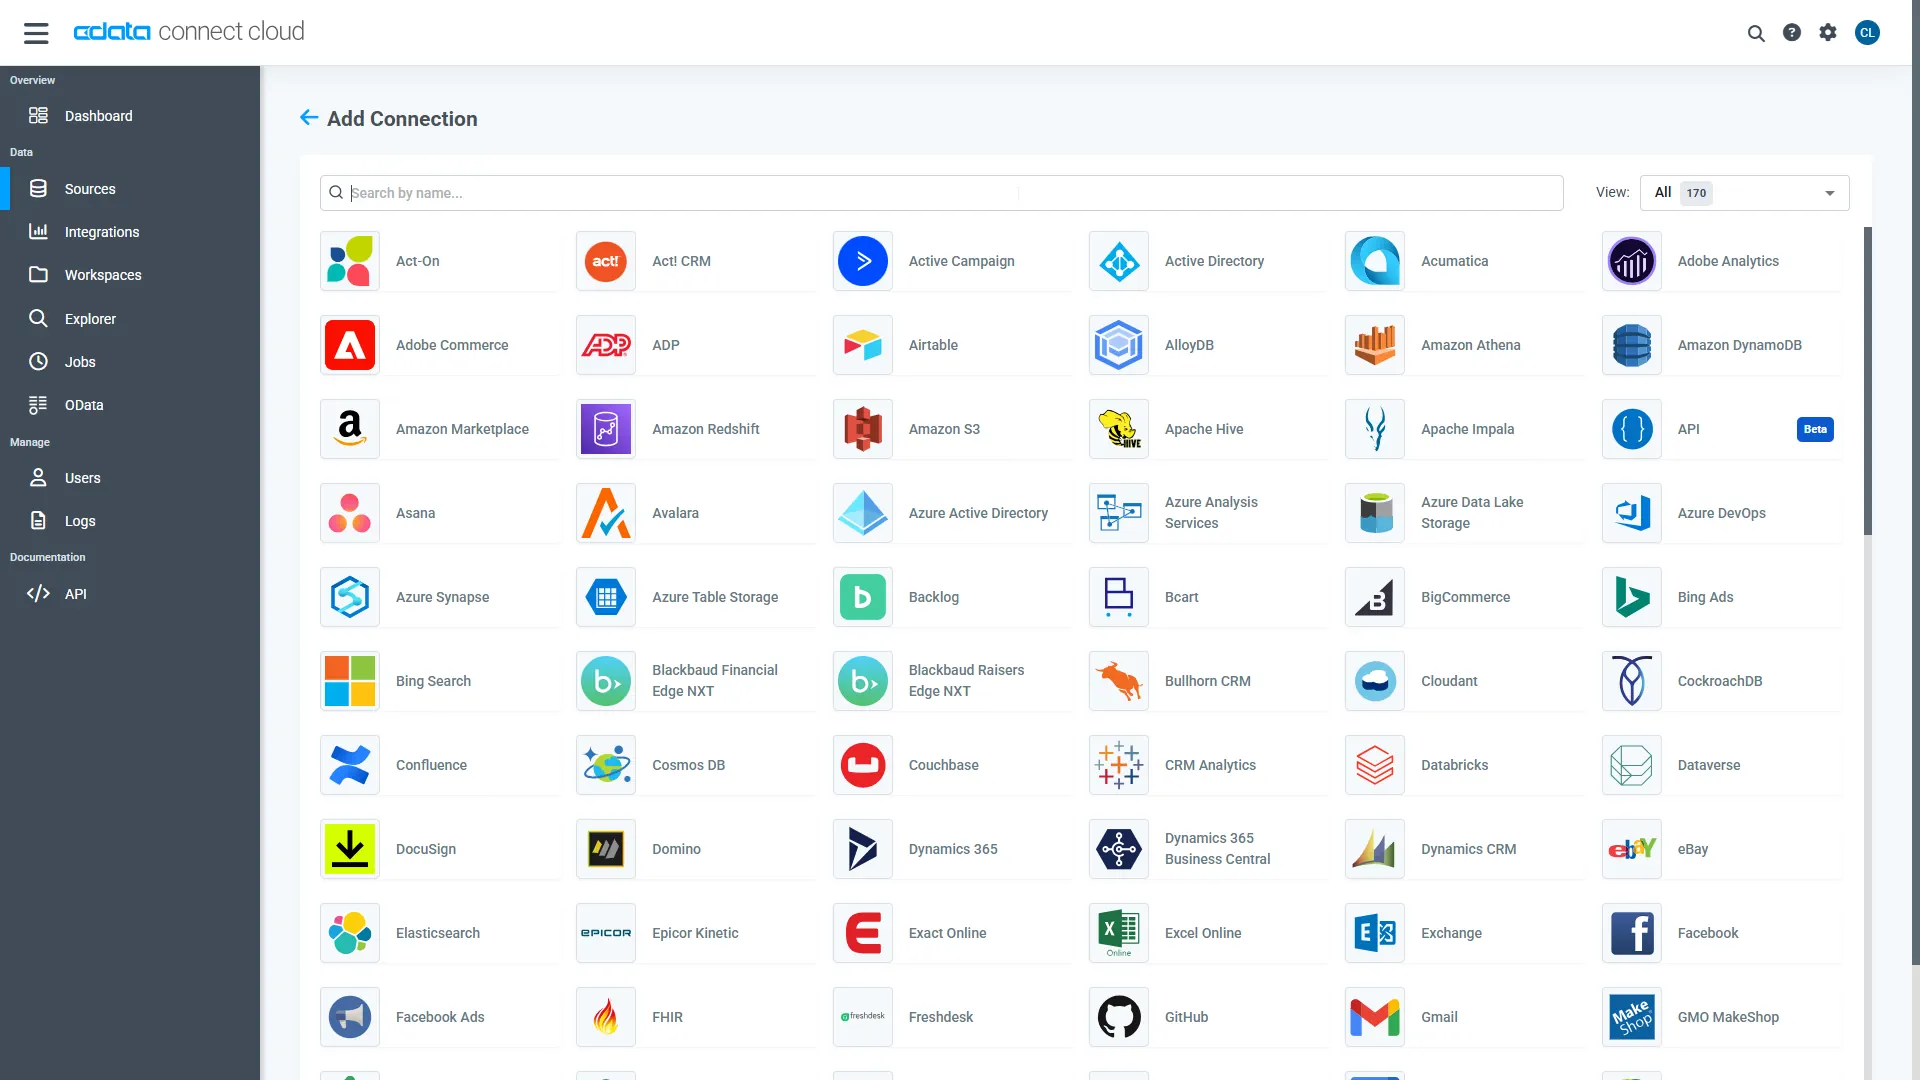
Select "PingOne" from the Add Connection panel.
-
Enter the required authentication properties.
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
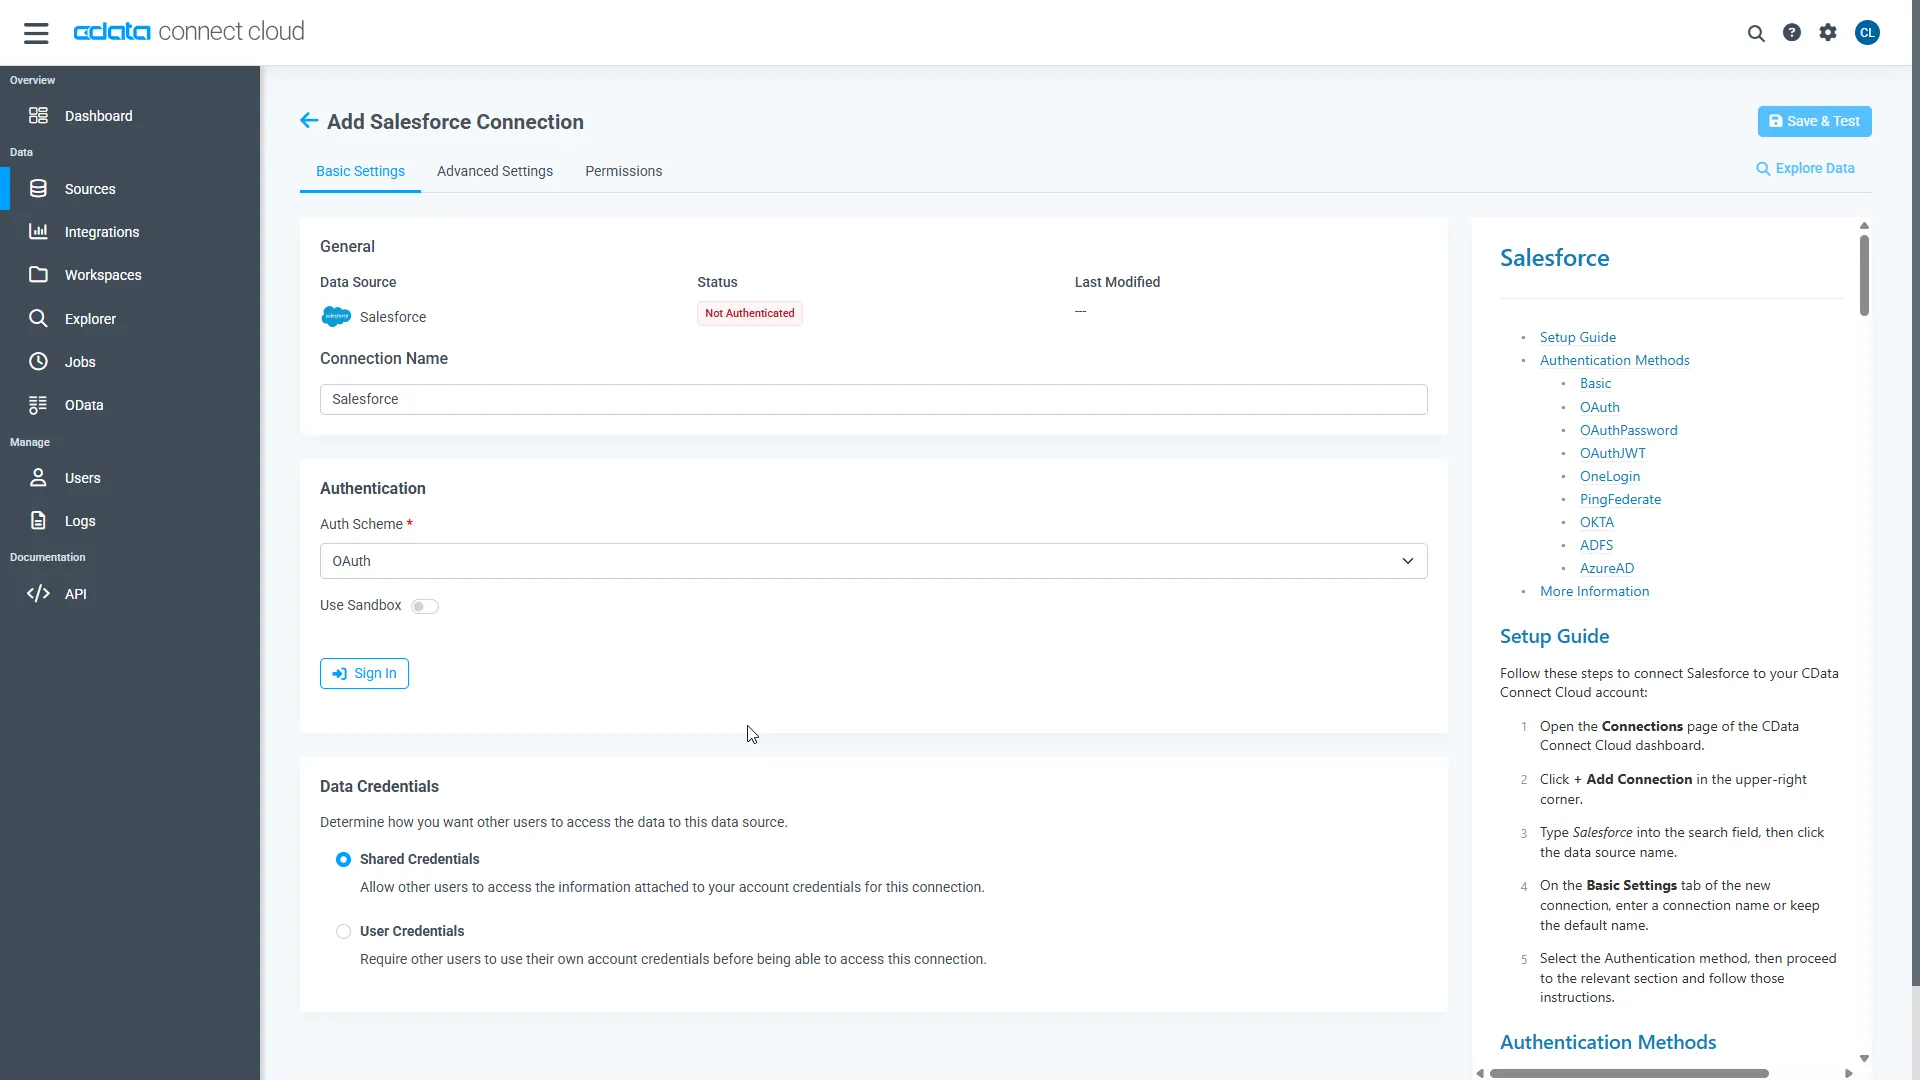 Click Create & Test.
-
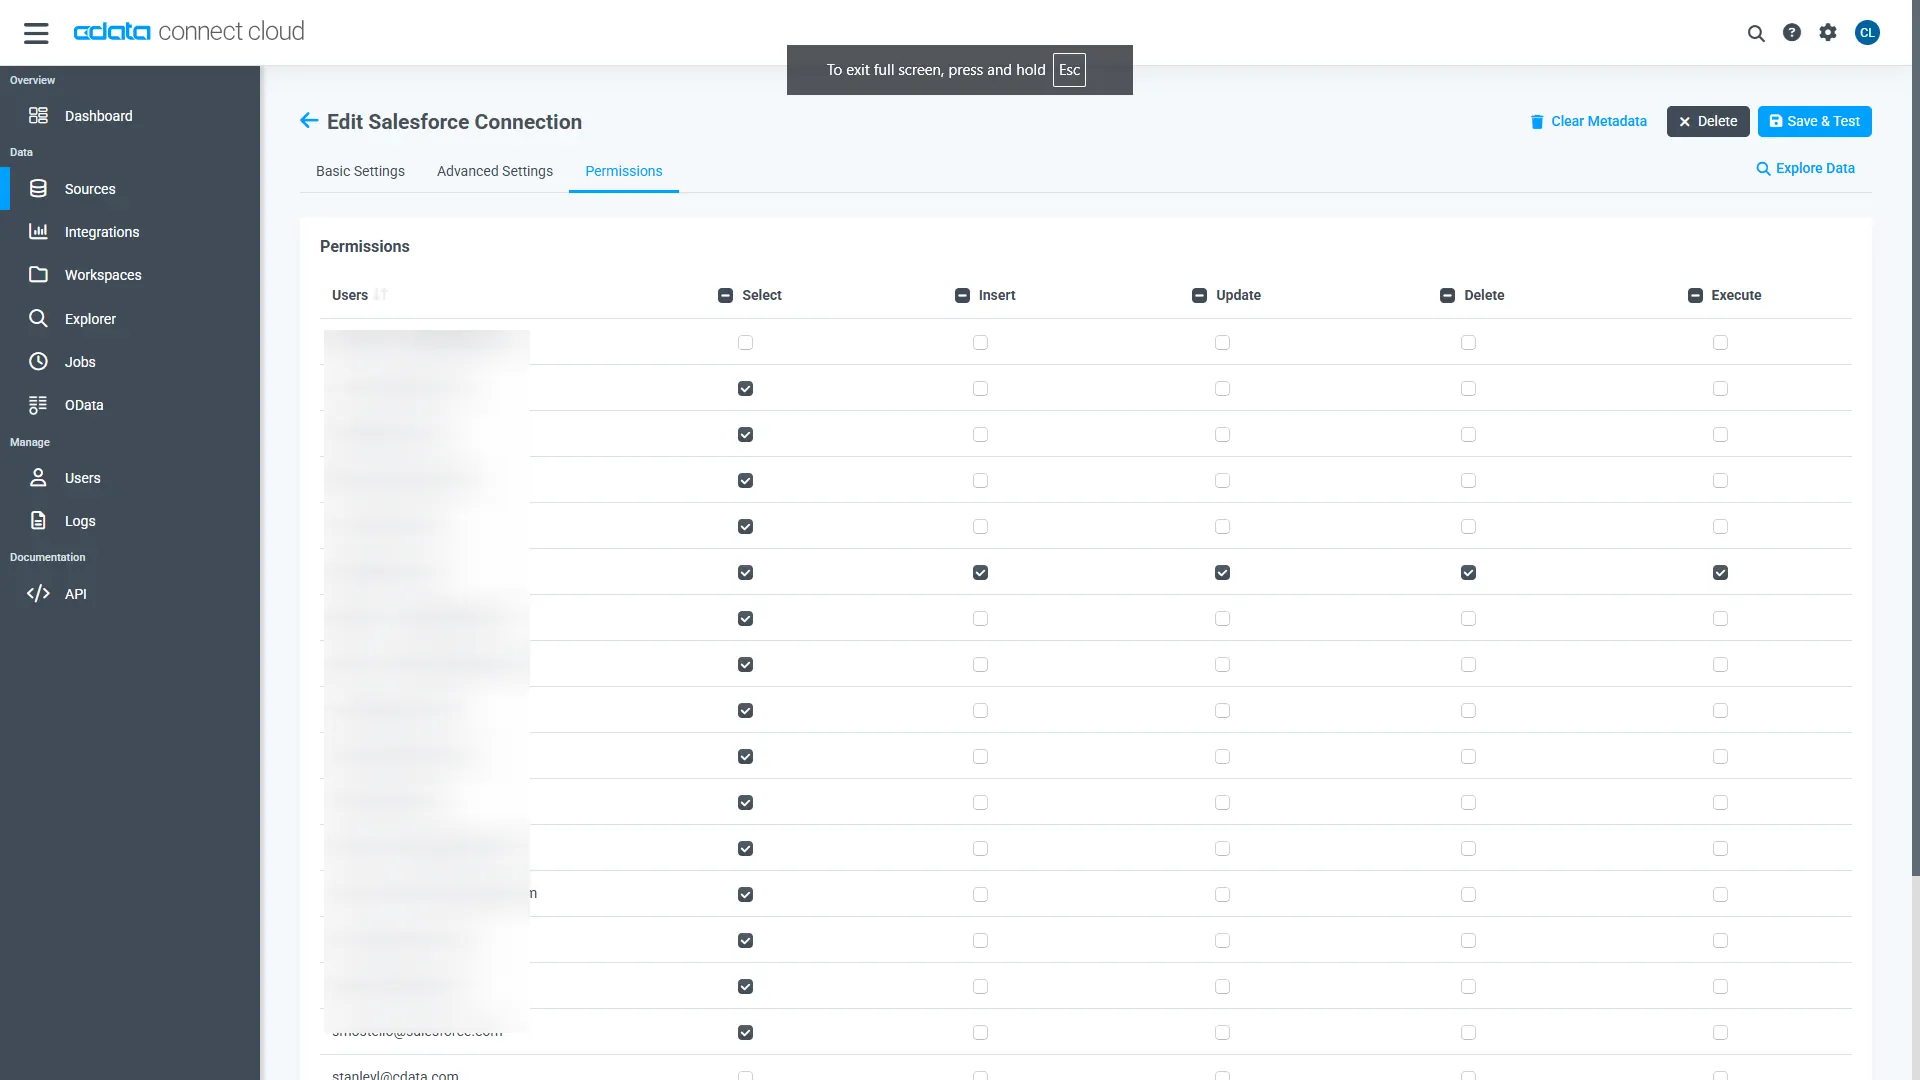
Open the Permissions tab and configure user access.
Add a Personal Access Token
A Personal Access Token (PAT) authenticates MCP requests from Agno to CData Connect AI.
- Open Settings and navigate to Access Tokens.
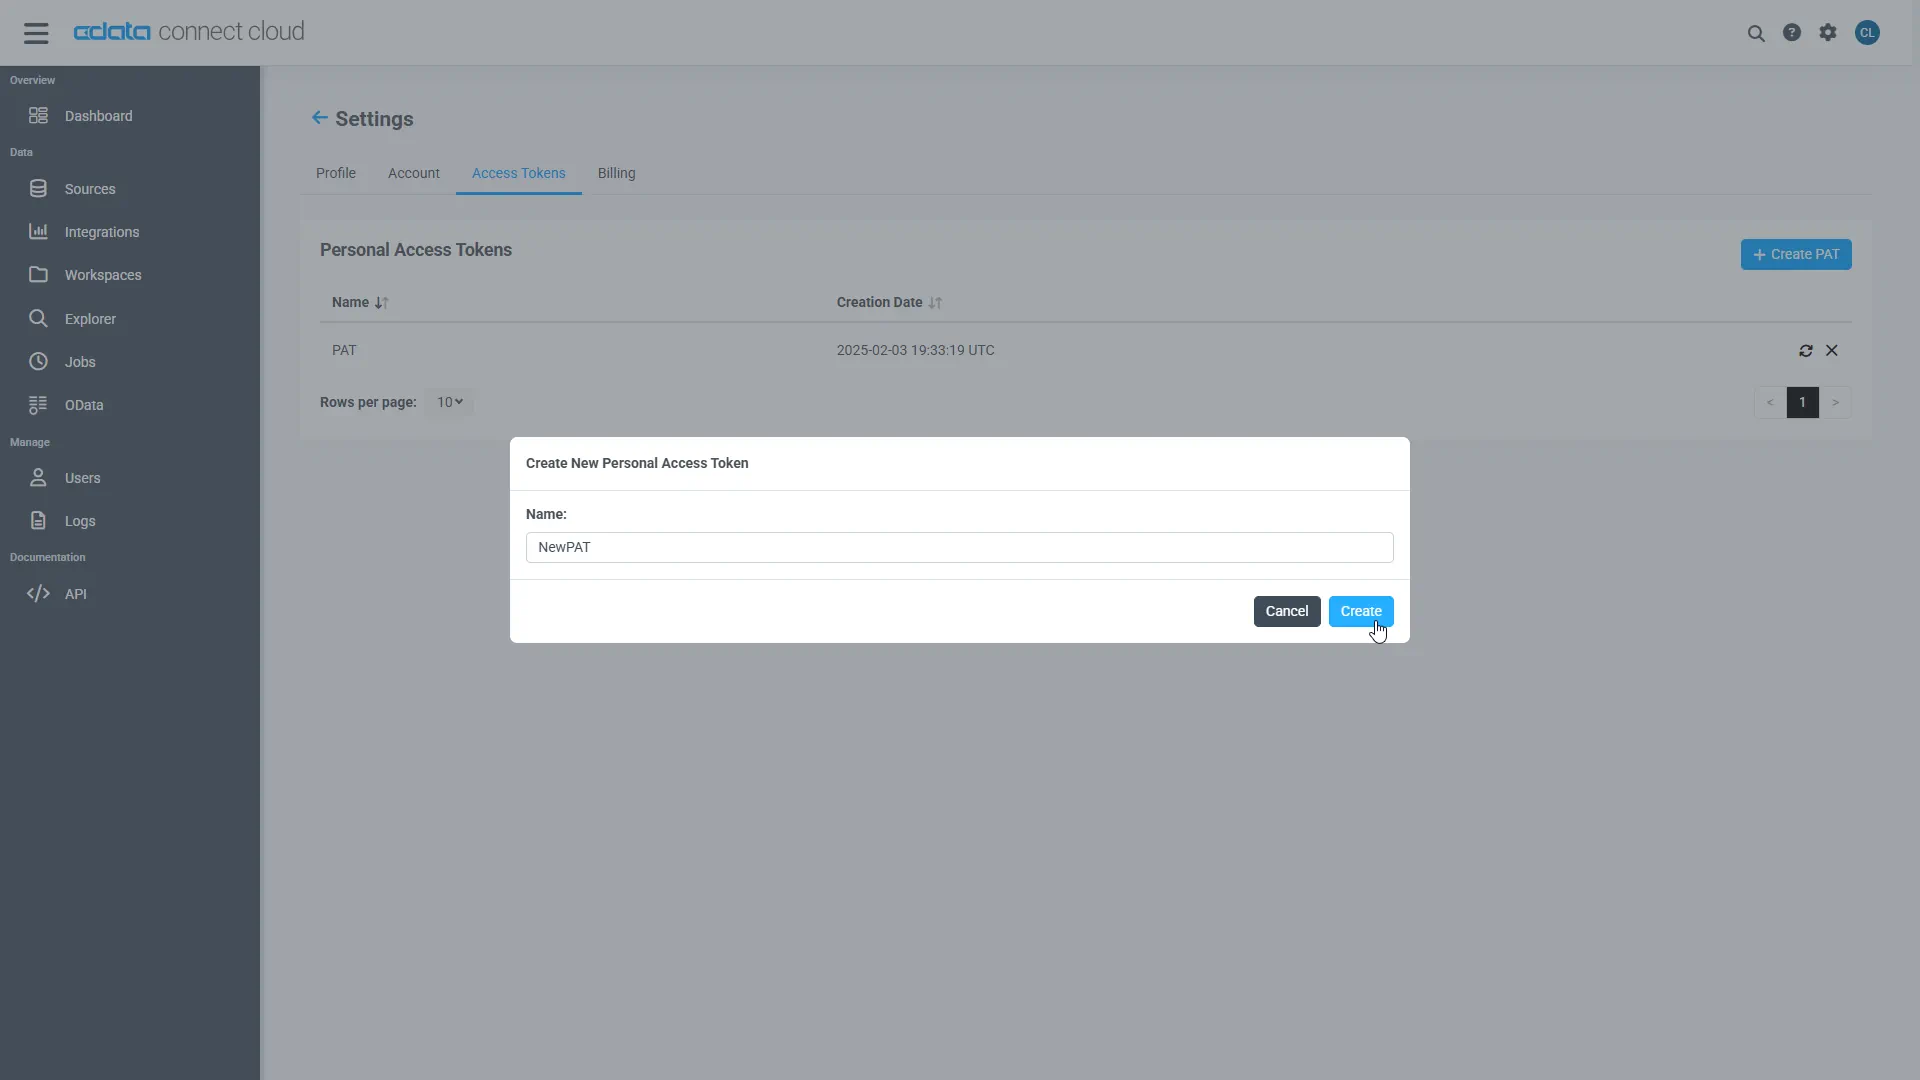
- Click Create PAT.
-
Save the generated token securely.
Step 2: Install required dependencies
Remote MCP Tools allow Grok to connect to external MCP (Model Context Protocol) servers, extending its capabilities with custom tools from third parties or your own implementations. Simply specify a server URL and optional configuration xAI manages the MCP server connection and interaction on your behalf.
Open the terminal and install the required dependencies for the MCP integration using pip.
pip install xai-sdk==1.4.0
The xai-sdk (v1.4.0) enables Remote MCP tools, and python-dotenv is used to securely load environment variables.
pip install python-dotenv
Step 3: Generate an xAI API key
- Create or login to xAI account
- Open xAI API console
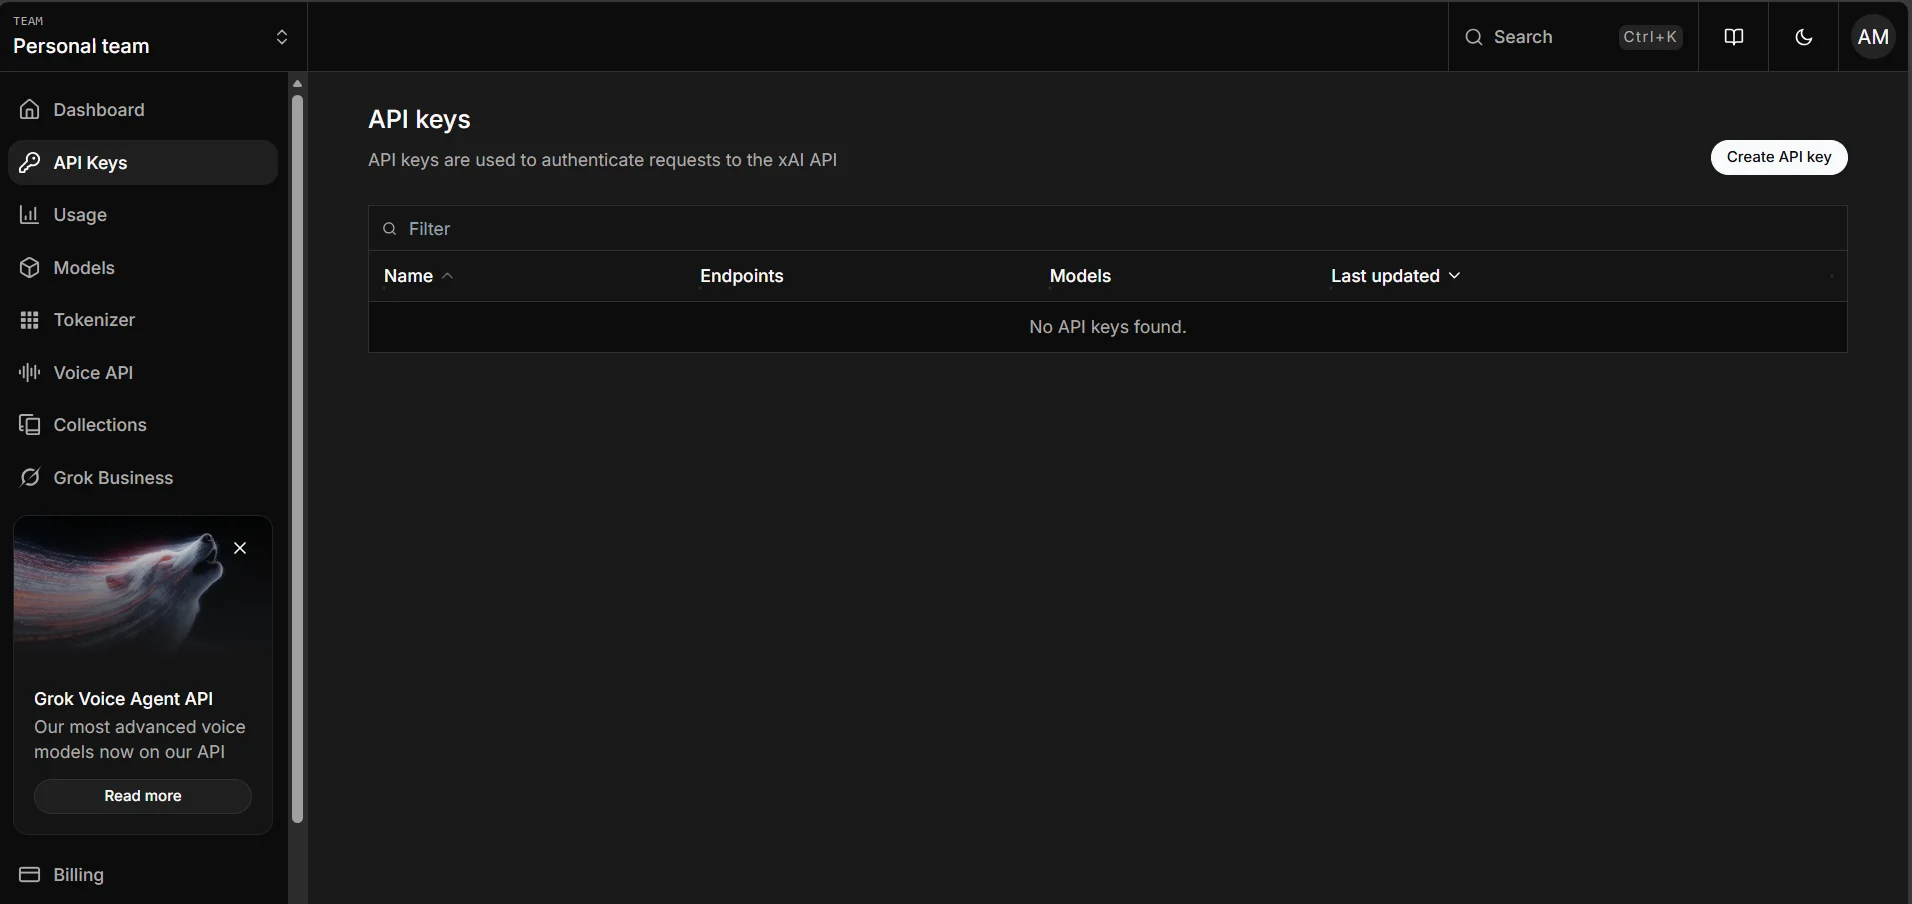
- Navigate to API Keys
- Click on create API key
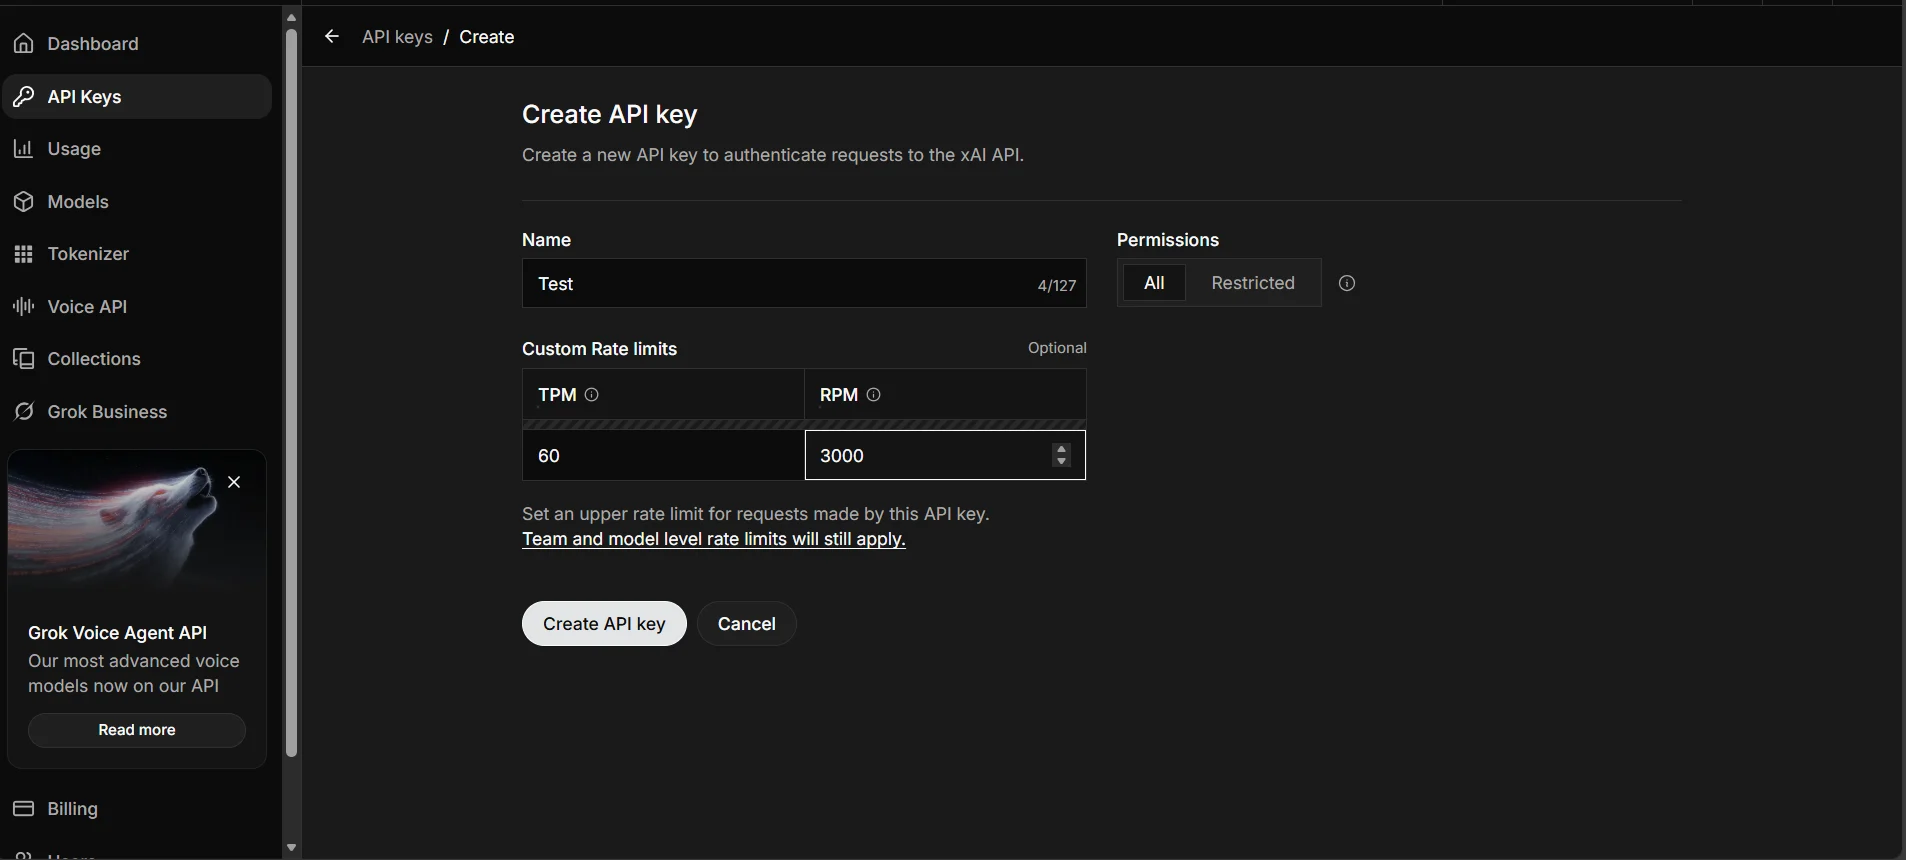
After generating an API key, user need to save it somewhere safe. Recommended option is to export it as an environment variable in your terminal or save it to a .env file.
Step 4: Connect to CData Connect AI
Initialize the Grok client and configure the MCP connection to CData Connect AI. The code below establishes a secure connection and sends a natural language query to your data source.
import os

from xai_sdk import Client
from xai_sdk.chat import user
from xai_sdk.tools import mcp

client = Client(api_key="Your_xAI-API_KEY")
chat = client.chat.create(
	model="grok-4-1-fast-non-reasoning",
	tools=[
		mcp(
			server_url="https://mcp.cloud.cdata.com/mcp",
			extra_headers={"Authorization": "Basic Username:PAT"} #Base64 Encoded Username:PAT
		)
		],
	include=["verbose_streaming"],
)

chat.append(user("List the top two catalogs for me please"))

is_thinking = True
for response, chunk in chat.stream():
	# View the server-side tool calls as they are being made in real-time
	for tool_call in chunk.tool_calls:
		print(f"
Calling tool: {tool_call.function.name} with arguments: {tool_call.function.arguments}")
	if response.usage.reasoning_tokens and is_thinking:
		print(f"
Thinking... ({response.usage.reasoning_tokens} tokens)", end="", flush=True)
	if chunk.content and is_thinking:
		print("

Final Response:")
		is_thinking = False
	if chunk.content and not is_thinking:
		print(chunk.content, end="", flush=True)

print("

Usage:")
print(response.usage)
print(response.server_side_tool_usage)
print("

Server Side Tool Calls:")
print(response.tool_calls)
This code initializes the Grok AI client, connects to CData Connect AI via MCP using Basic Authentication, and streams the response in real-time. The agent automatically discovers available tools, invokes them to query your live data, and displays both the tool calls and final results.
Run the script to see Grok query your connected data source.
Query Results
The output shows Grok invoking MCP tools through CData Connect AI and returning live data from your connected source.
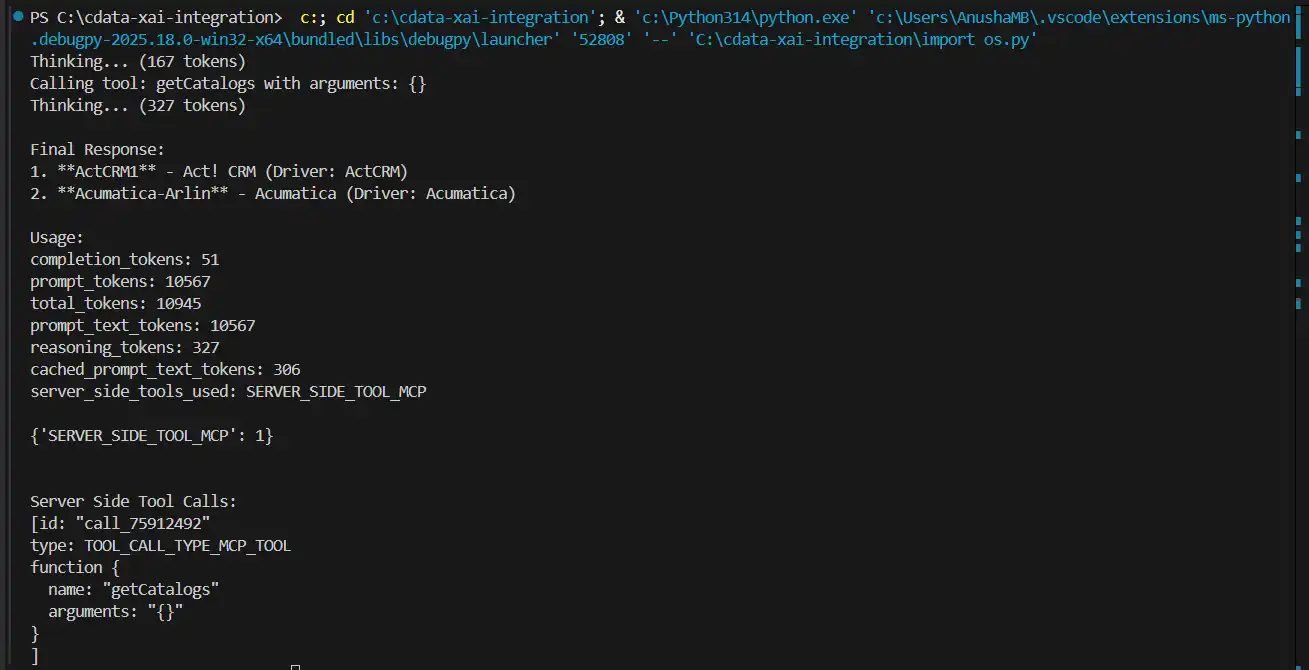
User can now query live data using natural language through Grok AI.
Build agentic workflows with Grok and CData Connect AI
Combining Grok AI with CData Connect AI delivers AI-powered data access without pipelines or custom integrations. Start your free trial today to see how CData can empower Grok with live, secure access to hundreds of external systems.