


Integrating LangChain with PingOne Data via CData Connect AI
LangChain is a framework used by developers, data engineers, and AI practitioners for building AI-powered applications and workflows by combining reasoning models (LLMs), tools, APIs, and data connectors. By integrating LangChain with CData Connect AI through the built-in MCP Server, workflows can effortlessly access and interact with live PingOne data in real time.
CData Connect AI offers a secure, low-code environment to connect PingOne and other data sources, removing the need for complex ETL and enabling seamless automation across business applications with live data.
This article outlines how to configure PingOne connectivity in CData Connect AI, register the MCP server with LangChain, and build a workflow that queries PingOne data in real time.
Prerequisites
- An account in CData Connect AI
- Python version 3.10 or higher, to install the LangChain and LangGraph packages
- Generate and save an OpenAI API key
- Install Visual Studio Code in your system
Step 1: Configure PingOne Connectivity for LangChain
Before LangChain can access PingOne, a PingOne connection must be created in CData Connect AI. This connection is then exposed to LangChain through the remote MCP server.
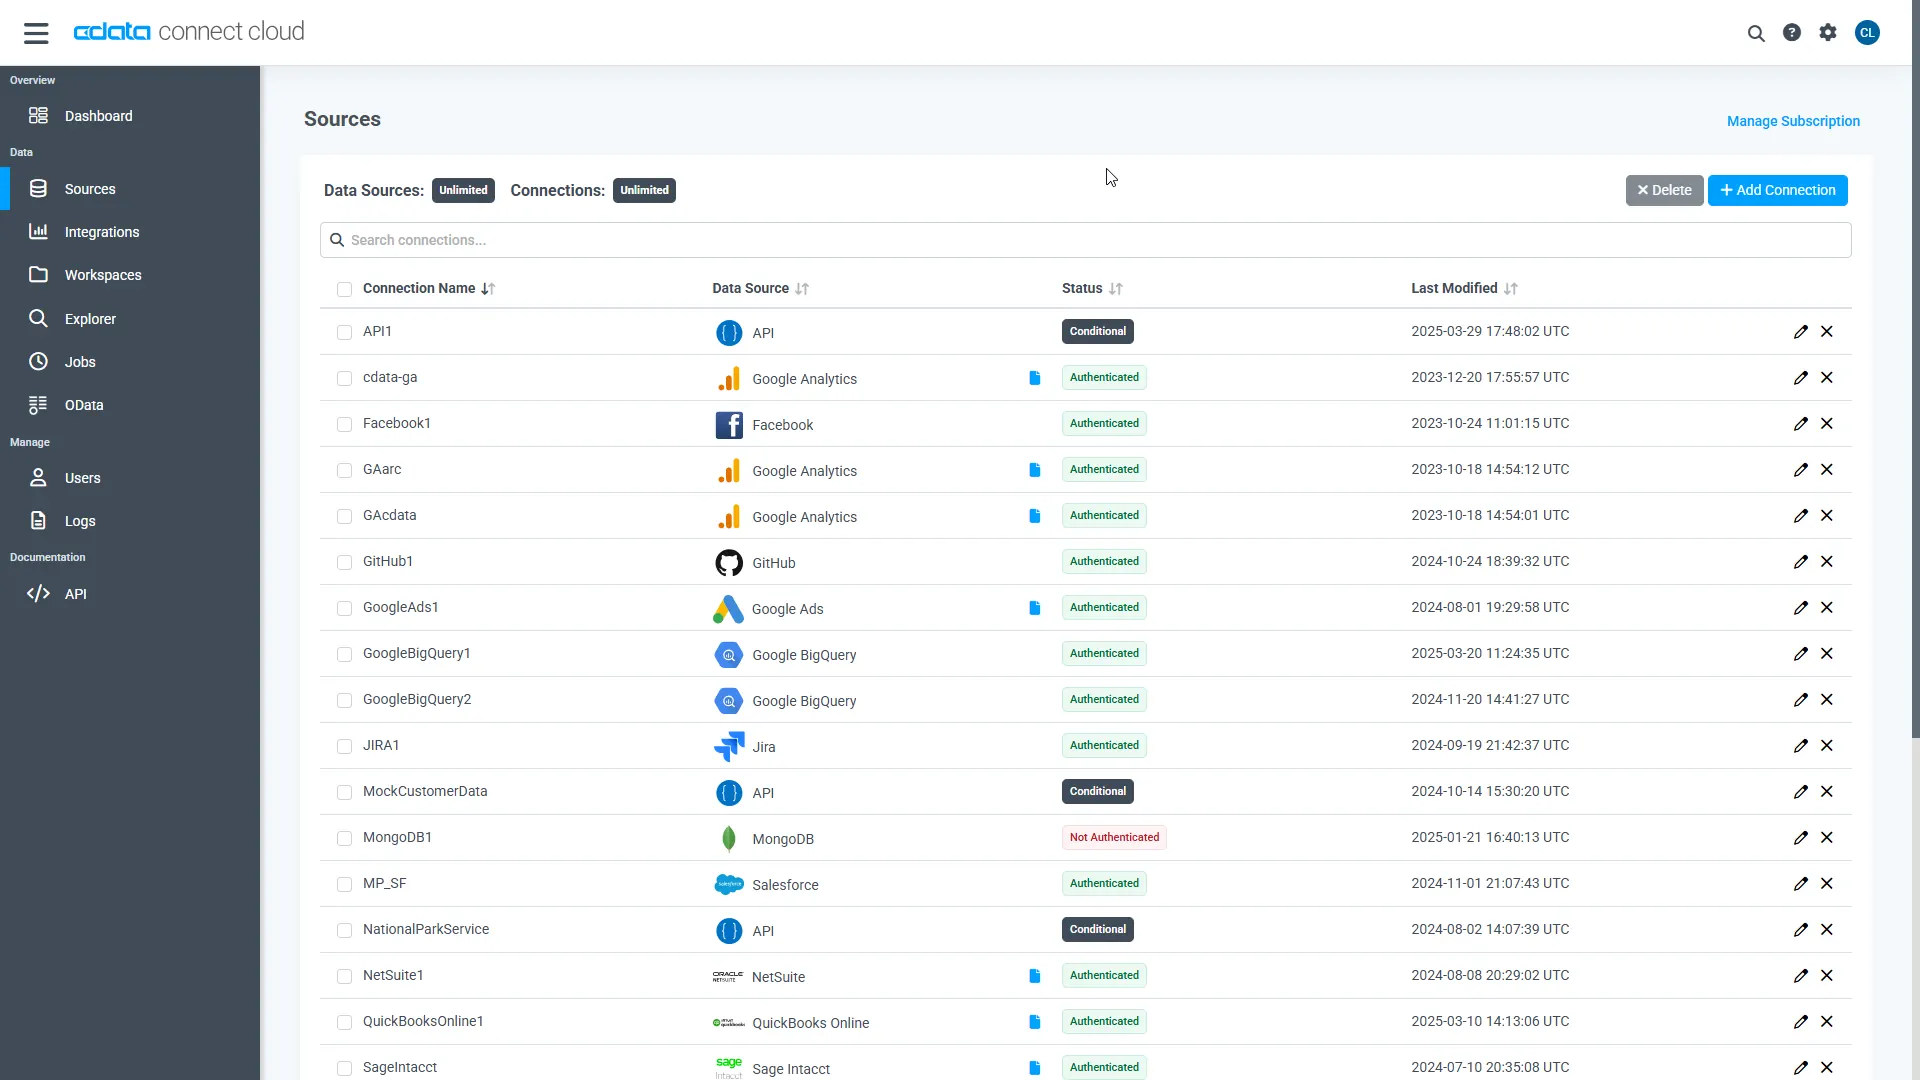
- Log in to Connect AI click Sources, and then click + Add Connection
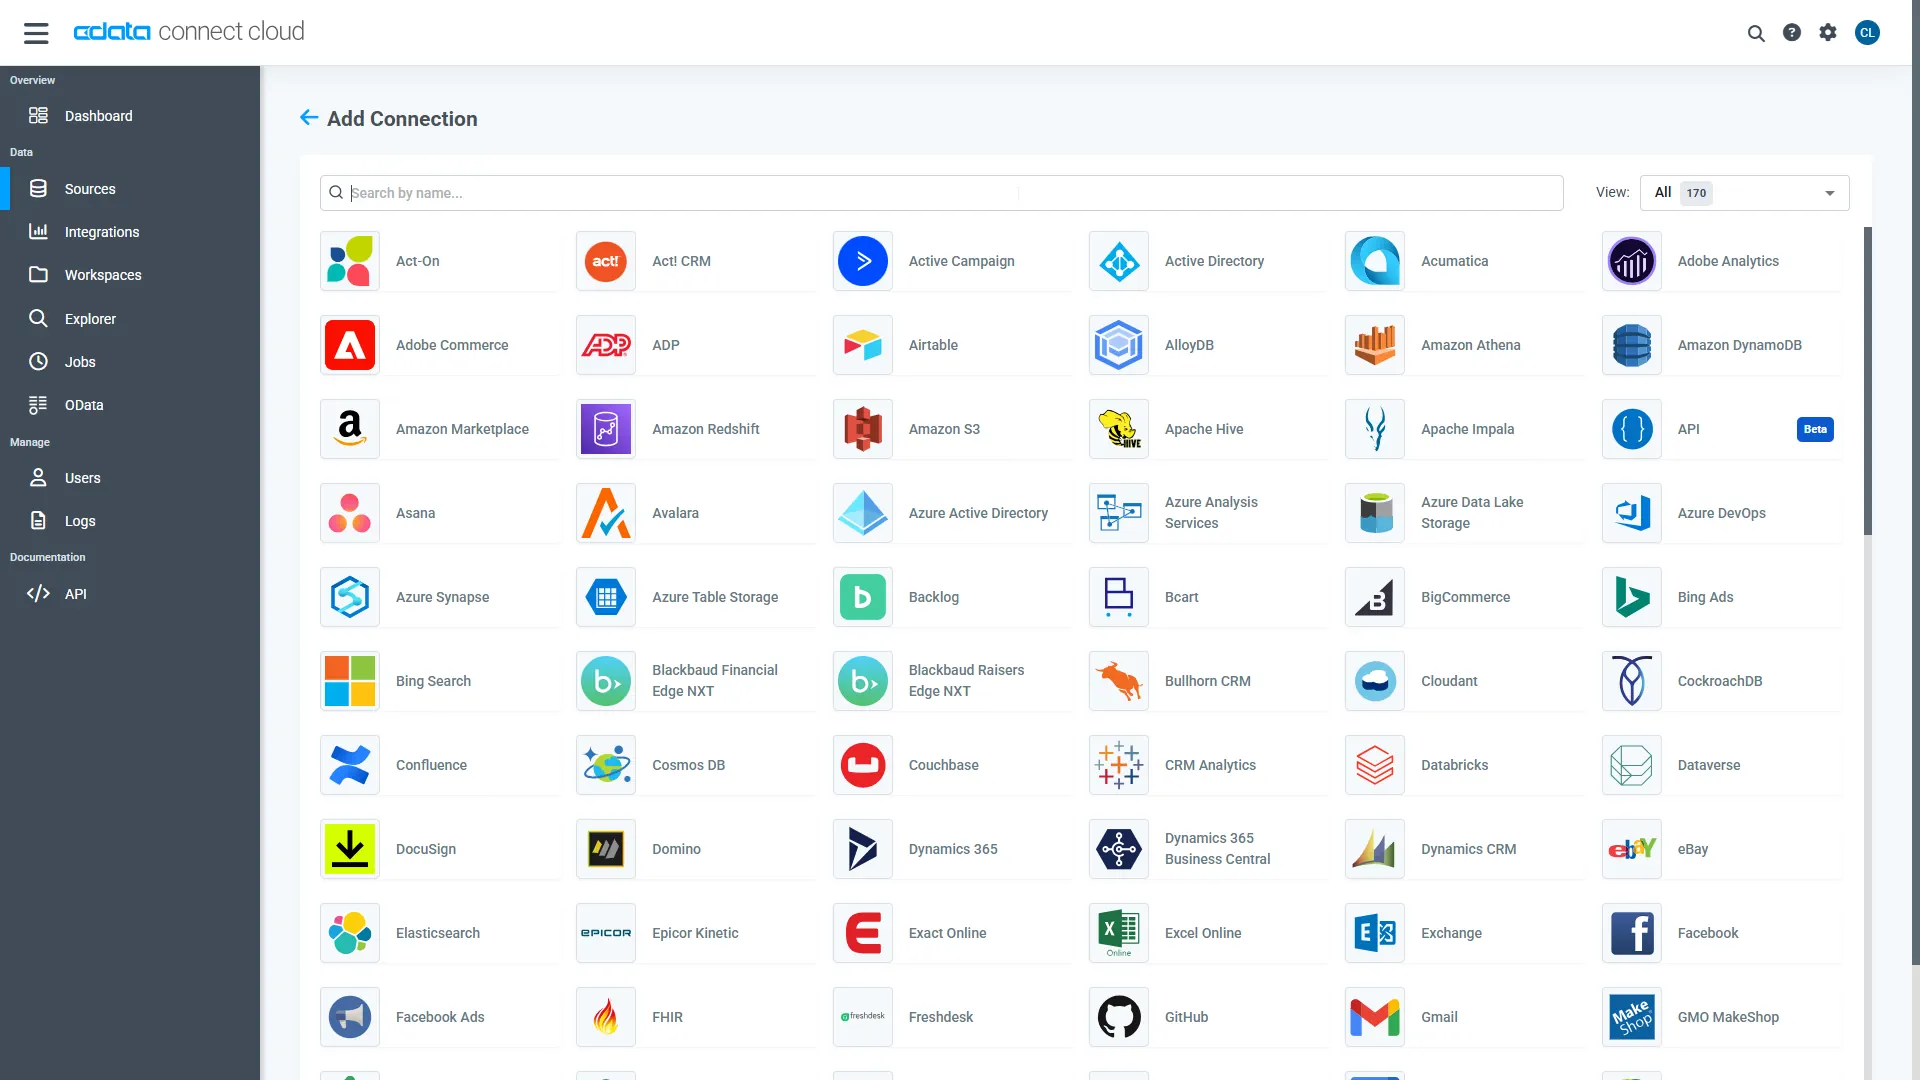
- From the available data sources, choose PingOne
-
Enter the necessary authentication properties to connect to PingOne
To connect to PingOne, configure these properties:
- Region: The region where the data for your PingOne organization is being hosted.
- AuthScheme: The type of authentication to use when connecting to PingOne.
- Either WorkerAppEnvironmentId (required when using the default PingOne domain) or AuthorizationServerURL, configured as described below.
Configuring WorkerAppEnvironmentId
WorkerAppEnvironmentId is the ID of the PingOne environment in which your Worker application resides. This parameter is used only when the environment is using the default PingOne domain (auth.pingone). It is configured after you have created the custom OAuth application you will use to authenticate to PingOne, as described in Creating a Custom OAuth Application in the Help documentation.
First, find the value for this property:
- From the home page of your PingOne organization, move to the navigation sidebar and click Environments.
- Find the environment in which you have created your custom OAuth/Worker application (usually Administrators), and click Manage Environment. The environment's home page displays.
- In the environment's home page navigation sidebar, click Applications.
- Find your OAuth or Worker application details in the list.
-
Copy the value in the Environment ID field.
It should look similar to:
WorkerAppEnvironmentId='11e96fc7-aa4d-4a60-8196-9acf91424eca'
Now set WorkerAppEnvironmentId to the value of the Environment ID field.
Configuring AuthorizationServerURL
AuthorizationServerURL is the base URL of the PingOne authorization server for the environment where your application is located. This property is only used when you have set up a custom domain for the environment, as described in the PingOne platform API documentation. See Custom Domains.
Authenticating to PingOne with OAuth
PingOne supports both OAuth and OAuthClient authentication. In addition to performing the configuration steps described above, there are two more steps to complete to support OAuth or OAuthCliet authentication:
- Create and configure a custom OAuth application, as described in Creating a Custom OAuth Application in the Help documentation.
- To ensure that the driver can access the entities in Data Model, confirm that you have configured the correct roles for the admin user/worker application you will be using, as described in Administrator Roles in the Help documentation.
- Set the appropriate properties for the authscheme and authflow of your choice, as described in the following subsections.
OAuth (Authorization Code grant)
Set AuthScheme to OAuth.
Desktop Applications
Get and Refresh the OAuth Access Token
After setting the following, you are ready to connect:
- InitiateOAuth: GETANDREFRESH. To avoid the need to repeat the OAuth exchange and manually setting the OAuthAccessToken each time you connect, use InitiateOAuth.
- OAuthClientId: The Client ID you obtained when you created your custom OAuth application.
- OAuthClientSecret: The Client Secret you obtained when you created your custom OAuth application.
- CallbackURL: The redirect URI you defined when you registered your custom OAuth application. For example: https://localhost:3333
When you connect, the driver opens PingOne's OAuth endpoint in your default browser. Log in and grant permissions to the application. The driver then completes the OAuth process:
- The driver obtains an access token from PingOne and uses it to request data.
- The OAuth values are saved in the location specified in OAuthSettingsLocation, to be persisted across connections.
The driver refreshes the access token automatically when it expires.
For other OAuth methods, including Web Applications, Headless Machines, or Client Credentials Grant, refer to the Help documentation.
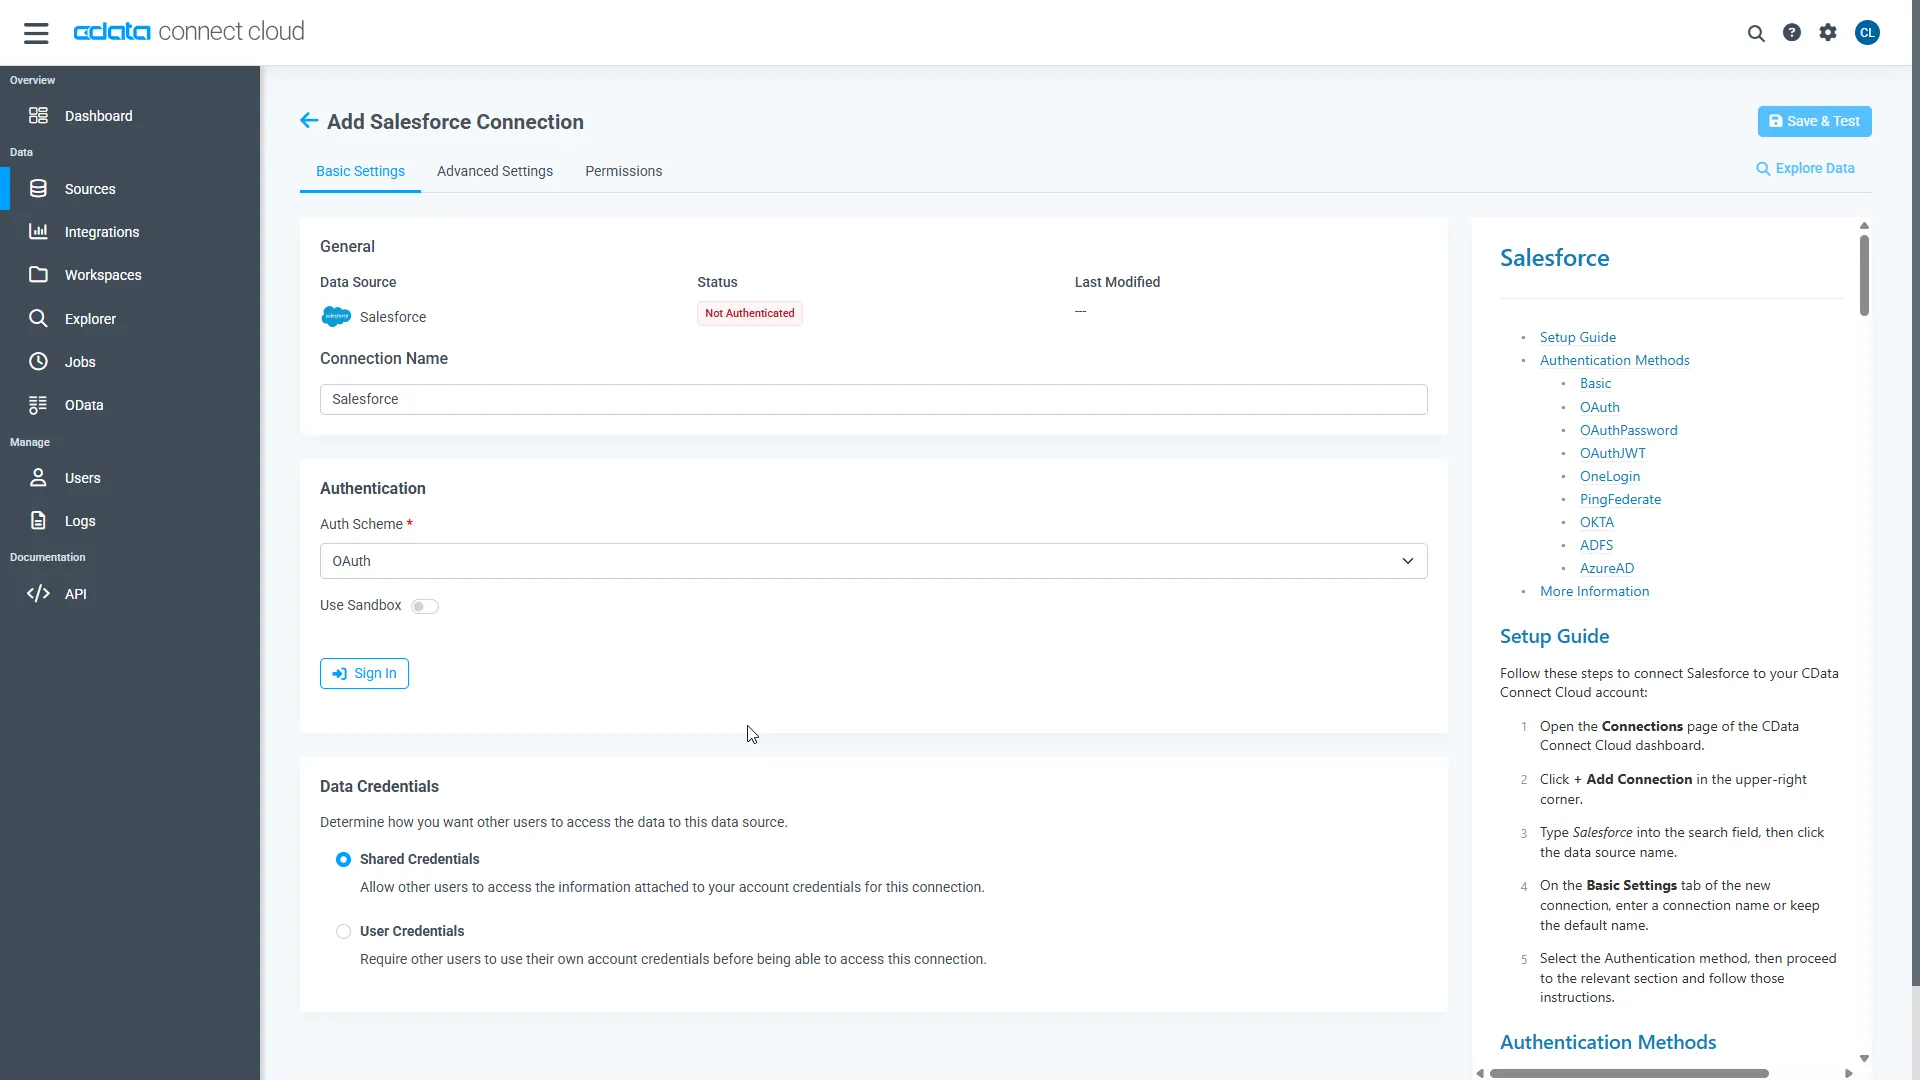
- Click Save & Test
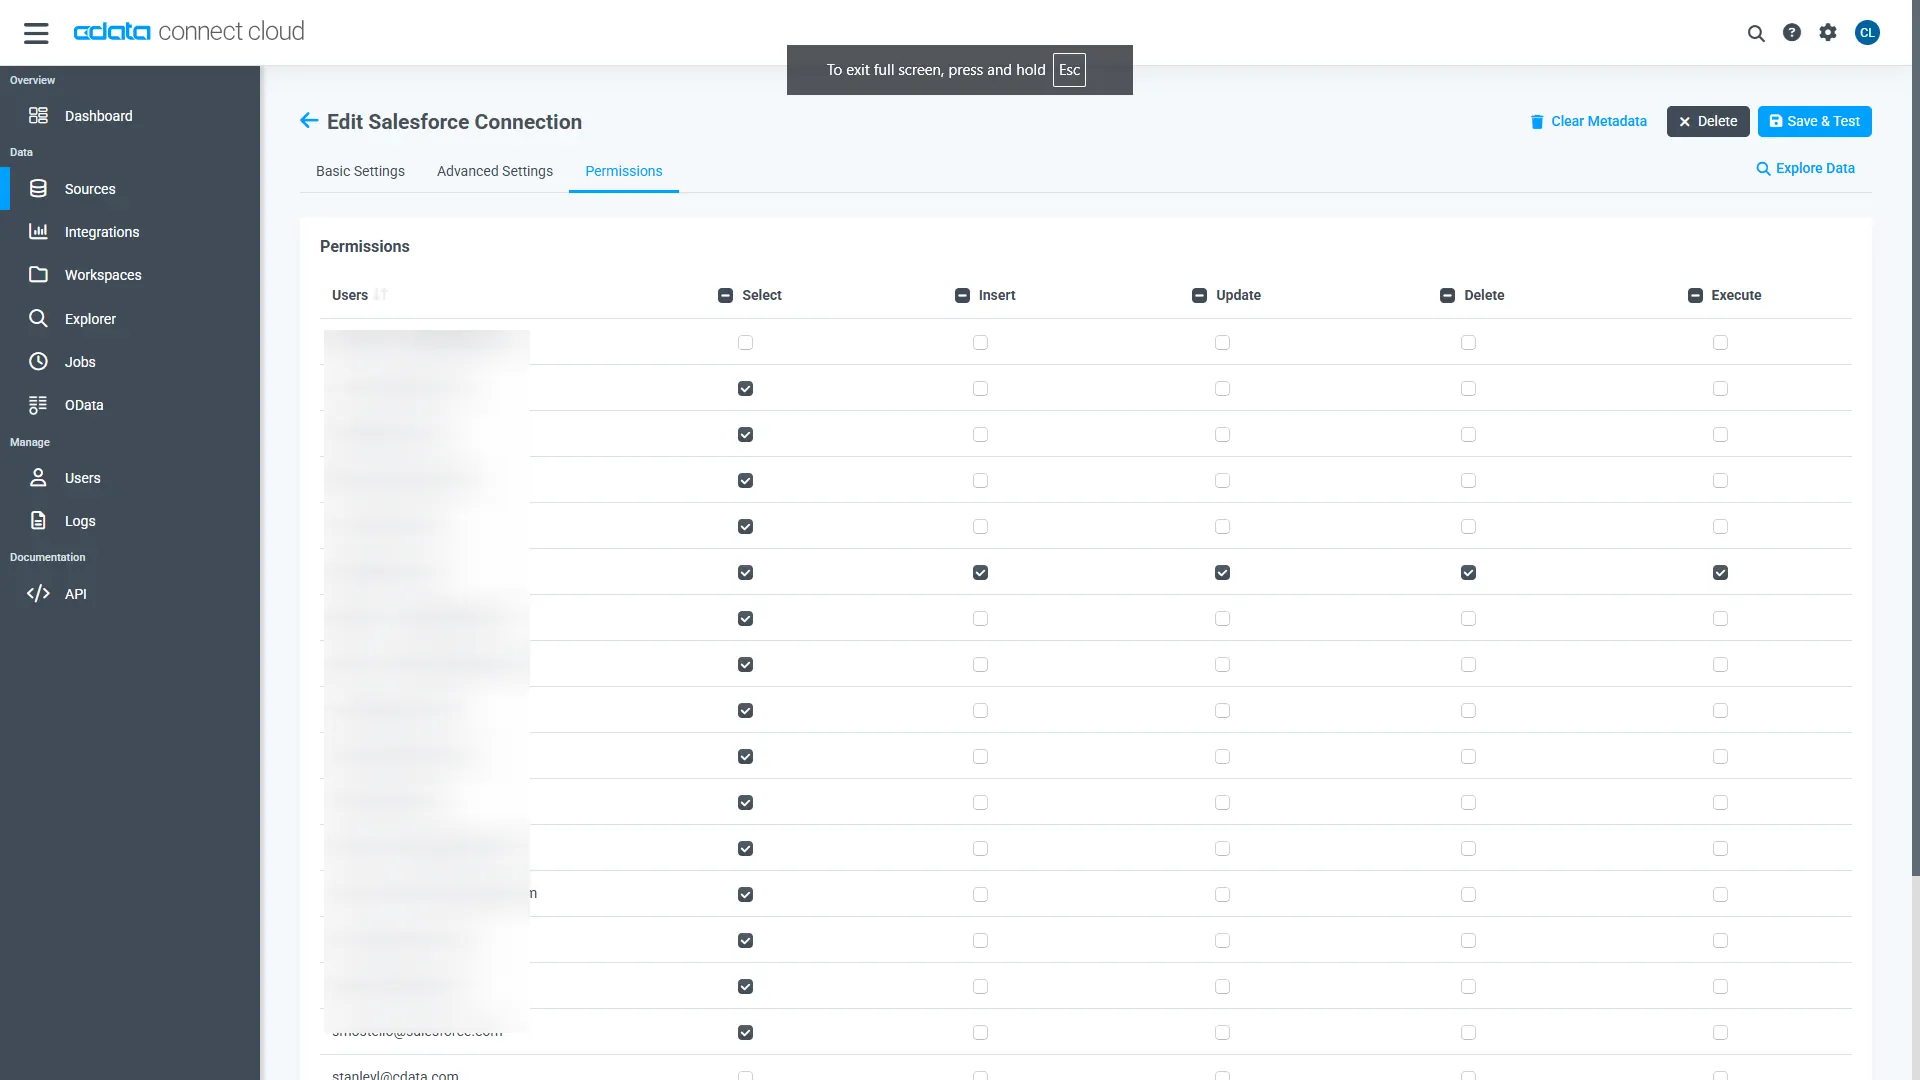
- Once authenticated, open the Permissions tab in the PingOne connection and configure user-based permissions as required
Generate a Personal Access Token (PAT)
LangChain authenticates to Connect AI using an account email and a Personal Access Token (PAT). Creating separate PATs for each integration is recommended to maintain access control granularity.
- In Connect AI, select the Gear icon in the top-right to open Settings
- Under Access Tokens, select Create PAT
- Provide a descriptive name for the token and select Create
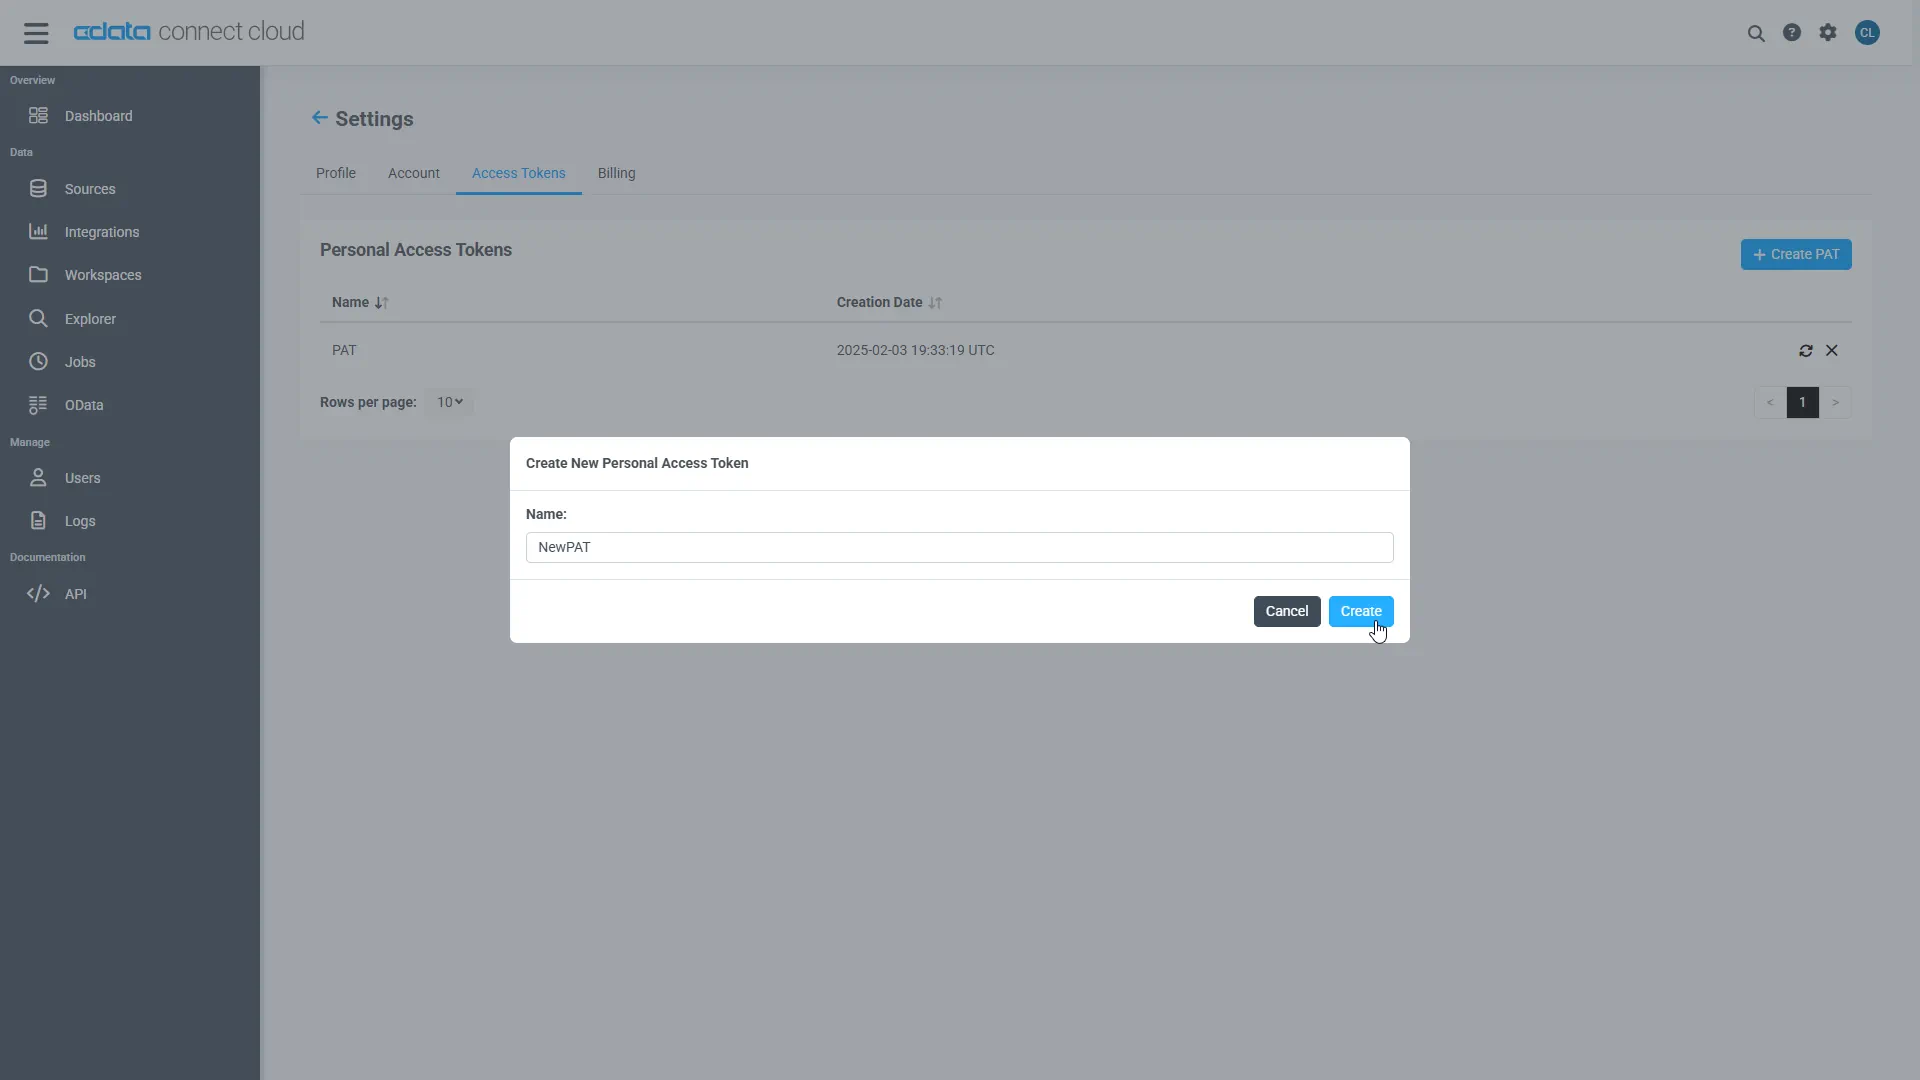
- Copy the token and store it securely. The PAT will only be visible during creation
With the PingOne connection configured and a PAT generated, LangChain is prepared to connect to PingOne data through the CData MCP server.
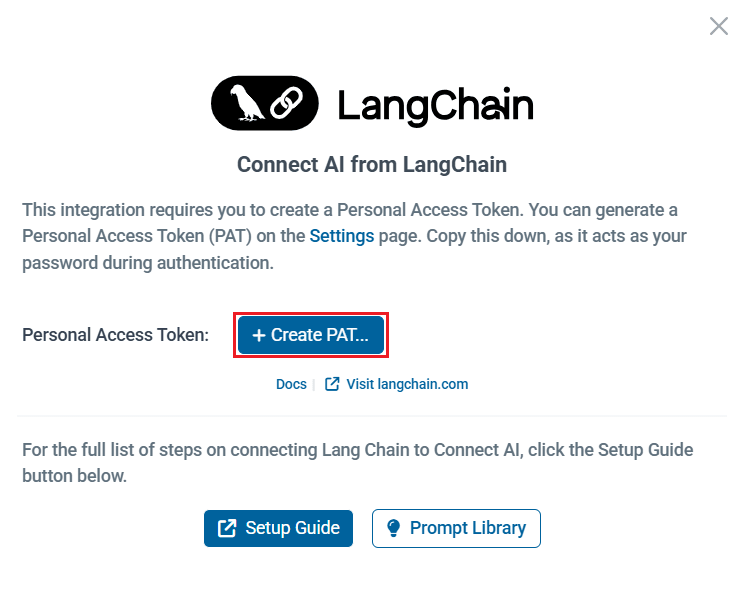
Note: You can also generate a PAT from LangChain in the Integrations section of Connect AI. Simply click Connect --> Create PAT to generate it.

Step 2: Connect to the MCP server in LangChain
To connect LangChain with CData Connect AI Remote MCP Server and use OpenAI (ChatGPT) for reasoning, you need to configure your MCP server endpoint and authentication values in a config.py file. These values allow LangChain to call the MCP server tools, while OpenAI handles the natural language reasoning.
- Create a folder for LangChain MCP
- Create two Python files within the folder: config.py and langchain.py
- In config.py, create a class Config to define your MCP server authentication and URL. You need to provide your Base64-encoded CData Connect AI username and PAT (obtained in the prerequisites):
class Config: MCP_BASE_URL = "https://mcp.cloud.cdata.com/mcp" #MCP Server URL MCP_AUTH = "base64encoded(EMAIL:PAT)" #Base64 encoded Connect AI Email:PATNote: You can create the base64 encoded version of MCP_AUTH using any Base64 encoding tool.
- In langchain.py, set up your MCP server and MCP client to call the tools and prompts:
"""
Integrates a LangChain ReAct agent with CData Connect AI MCP server.
The script demonstrates fetching, filtering, and using tools with an LLM for agent-based reasoning.
"""

import asyncio
from langchain_mcp_adapters.client import MultiServerMCPClient
from langchain_openai import ChatOpenAI
from langgraph.prebuilt import create_react_agent
from config import Config

async def main():

# Initialize MCP client with one or more server URLs
mcp_client = MultiServerMCPClient(
  connections={
    "default": { # you can name this anything
    "transport": "streamable_http",
    "url": Config.MCP_BASE_URL,
    "headers": {"Authorization": f"Basic {Config.MCP_AUTH}"},
    }
  }
)

# Load remote MCP tools exposed by the server
all_mcp_tools = await mcp_client.get_tools()
print("Discovered MCP tools:", [tool.name for tool in all_mcp_tools])

# Create and run the ReAct style agent
llm = ChatOpenAI(
  model="gpt-4o",
  temperature=0.2,
  api_key="YOUR_OPEN_API_KEY" #Use your OpenAI API Key here, this can be found here: https://platform.openai.com/
)

agent = create_react_agent(llm, all_mcp_tools)

user_prompt = "How many tables are available in PingOne1?" #Change prompts as per need
print(f"
User prompt: {user_prompt}")

# Send a prompt asking the agent to use the MCP tools
response = await agent.ainvoke(
  { "messages": [{ "role": "user", "content": (user_prompt),}]}
)

# Print out the agent's final response
final_msg = response["messages"][-1].content
print("Agent final response:", final_msg)

if __name__ == "__main__":

asyncio.run(main())
Step 3: Install the LangChain and LangGraph packages
Since this workflow uses LangChain together with CData Connect AI MCP and integrates OpenAI for reasoning, you need to install the required Python packages.
Run the following command in your project terminal:
pip install langchain-mcp-adapters langchain-openai langgraph
Step 4: Prompt PingOne using LangChain (via the MCP server)
- When the installation finishes, run python langchain.py to execute the script
- The script connects to the MCP server and discovers the CData Connect AI MCP tools available for querying your connected data
- Supply a prompt (e.g., "How many tables are available in PingOne?")
- Accordingly, the agent responds with the results

Get CData Connect AI
To get live data access to hundreds of SaaS, Big Data, and NoSQL sources directly from your cloud applications, try CData Connect AI today!